chiprook

Cybersecurity News

September 15
Security

BambooToken Malware Controls Windows and Linux Systems via MQTT

Black Lotus Labs (Lumen) described BambooToken malware active since 2023. Since 2024-2025 it uses MQTT for command servers, infecting Windows and Linux via signed Tendyron OnKey software and a fake Kingsoft Office. About a dozen organizations in Asia and South America were affected.
BambooToken Malware Controls Windows and Linux Systems via MQTT
Security

Hackers target WordPress sites via third-party WooCommerce plugin

A critical vulnerability CVE-2026-27540 in the premium WooCommerce Wholesale Lead Capture plugin (versions 2.0.3.1 and older) allows unauthenticated PHP backdoor uploads. Wordfence blocked over 100,000 attacks; a fix was released in version 2.0.3.2 on 20 February.

Hackers target WordPress sites via third-party WooCommerce plugin
Security

Nearly 8000 organizations hit by fake voicemail transcript phishing

Check Point Research uncovered a campaign of 58,000 emails mimicking automatic voicemail transcripts. Malicious SVG attachments with JavaScript redirect victims to fake login pages to steal credentials.

Nearly 8000 organizations hit by fake voicemail transcript phishing
Security

Women secretly recorded on London street via Ray-Ban glasses sold as dating course

A University of Sydney researcher analyzed about 350 videos in which men secretly filmed women through Meta Ray-Ban glasses and sold the footage as ads for pickup courses. Meta sold about 7 million pairs by 2025; filming in public without consent remains legal in the UK, but Wetherspoon pubs and ATG theatres have banned the glasses.

Women secretly recorded on London street via Ray-Ban glasses sold as dating course
Security

Cops searched thousands of Flock cameras for reasons 'LMAO,' 'IDK,' 'Hehe,' 'Asdfg'

EFF analyzed search logs in the Flock license plate recognition system: dozens of officers entered reasons like 'LMAO,' 'LOL,' 'idk,' 'asdfg' and insults. One officer in Indiana searched a plate across a database of more than 19,000 cameras in 1,558 cities with the reason 'LMAO.'

Cops searched thousands of Flock cameras for reasons 'LMAO,' 'IDK,' 'Hehe,' 'Asdfg'
Security

AI can unmask how thousands of Georgia voters cast their ballots

Princeton researcher Max Springer found Dominion scanners in Georgia shuffle ballots with a deterministic algorithm rather than randomly. Using AI agents for about $20, he reconstructed the submission order of 1.52 million ballots (98.9%) in 114 of 139 counties and uniquely matched about 15,000 people to voters. The state election board declined to require counties to install patch 5.17 before the November election.

AI can unmask how thousands of Georgia voters cast their ballots
Security

Most firms unable to recover quickly from ransomware

Fenix24 studied more than 500 ransomware recoveries: only 0.5% of 800+ clients came close to their 24–48 hour goals, and only partially. Full recovery took weeks, and 99.2% of clients had no documented recovery plan for identity systems.

Most firms unable to recover quickly from ransomware
Security

CenterPoint Energy Confirms Intruder Accessed Customer Information

Texas utility CenterPoint Energy confirmed an intruder obtained personal data of some customers through a third-party system. The company serves about 7 million customers; electricity and gas supply were not interrupted. A criminal forum claimed 7.49 million files were stolen via a poorly secured API.

CenterPoint Energy Confirms Intruder Accessed Customer Information
Security

F5 Bot Defense uses real-time risk scoring to detect fraud and abuse

F5 announced enhancements to Distributed Cloud Bot Defense with persistent device identification and real-time risk scoring. The system distinguishes humans, trusted AI agents, and malicious bots, reducing CAPTCHA challenges and false positives.

Security

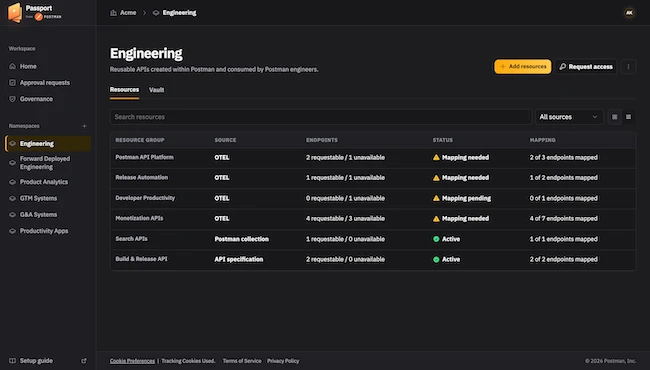
Postman Passport controls API access without exposing credentials

Postman announced Passport, a separate product for secure API access. Real keys and tokens remain in the client's infrastructure, while developers and AI agents receive only a cryptographic link tied to their identity. Permissions are granted per action, host, and path; revocation takes seconds.

Postman Passport controls API access without exposing credentials
Security

New cloud security vulnerability uncovered

An international team of researchers, including Professor David Oswald from the University of Birmingham, discovered a vulnerability in cloud computing that could compromise users' confidential data.

New cloud security vulnerability uncovered
Security

Thai Broadband Provider Hacked via Fortinet Vulnerability

Attackers gained access to Thai provider 3BB's systems via CVE-2024-21762 in FortiGate SSL-VPN and reconnaissance against F5 BIG-IP. The attack was discovered after hackers left 298 files with tools in an open directory on infrastructure in Thailand.

Thai Broadband Provider Hacked via Fortinet Vulnerability
Security

Swiss court sentences 52-year-old Ukrainian ransomware dev to nearly 13 years in the cooler

The Zurich District Court sentenced a 52-year-old Ukrainian to 12 years and 9 months in prison for developing the LockerGoga, MegaCortex, and Nefilim ransomware. He also received a 10-year ban on entering Switzerland; the sentence can be appealed.

Swiss court sentences 52-year-old Ukrainian ransomware dev to nearly 13 years in the cooler
Security

From data residency to key sovereignty: Thales launches UK cloud HSM

Thales introduced a UK version of its Luna Cloud HSM service: cryptographic keys are generated, stored, used, backed up, and destroyed within the UK. The service is available via the Data Protection on Demand marketplace and is not tied to a specific hyperscaler.

From data residency to key sovereignty: Thales launches UK cloud HSM
Security

Customers of 45 insurers exposed in South African cyber breach

Hackers accessed the Jira platform of IT provider MIP Holdings and stole about 400,000 records of customers from roughly 45 South African insurance companies. The attackers entered via an employee's personal laptop with stolen credentials and remained in the system for about three weeks. MIP paid a ransom, but the data still appeared on a leak site.

Customers of 45 insurers exposed in South African cyber breach
Security

AI the Top Priority for New Spend as Cyber Budgets Flatline

According to IANS, 69% of 500 surveyed US security leaders named AI the top area for additional spending. Meanwhile, 55% of respondents said their budgets stayed flat or were cut due to economic conditions.

AI the Top Priority for New Spend as Cyber Budgets Flatline
Security

Exaforce Extends Its AI Security Tool to Monitor More Than Just Claude

Exaforce released Exaforce AI Security, a tool that detects and monitors AI agents using existing SOC telemetry, with no new agents or gateways. Besides Claude, it supports OpenAI, Gemini, Microsoft Copilot and OAuth apps; on a threat it can revoke a session, disable an API key or isolate a device.

Exaforce Extends Its AI Security Tool to Monitor More Than Just Claude
Security

ENISA Used an OpenAI Model to Find Four Flaws in EU Code, Politico Reports

EU cybersecurity agency ENISA, with CERT-EU, analyzed the code of an EU project using an advanced OpenAI model and found four vulnerabilities, one rated high risk (CVE-2026-73431, score 8.8). The flaws have been fixed; the EU gained access to advanced US models in July.

ENISA Used an OpenAI Model to Find Four Flaws in EU Code, Politico Reports
Security

Enhanced Viewer for Twitch: OAuth token forwarded to JeetBot proxy

The Enhanced Viewer for Twitch extension for Chrome and Firefox contained code that sent OAuth tokens from the Authorization header to a proxy linked to JeetBot. According to Socket, the Chrome extension alone has approximately 30,000 users.

Enhanced Viewer for Twitch: OAuth token forwarded to JeetBot proxy
Security

Hacking Cat: Destructive breaches using Gorilla RAT and Monkey ransomware

Kaspersky reported a campaign by the Hacking Cat group against Russian organizations: attackers exploit Exchange vulnerabilities, deploy Gorilla RAT for remote control, and encrypt data with Monkey ransomware on Windows, Linux, and ESXi. Some variants do not save decryption keys, making losses irreversible.

Hacking Cat: Destructive breaches using Gorilla RAT and Monkey ransomware
Security

OpenAI investigates report linking AI agents to RubyGems attack

Researchers said OpenAI AI agents attacked RubyGems.org in May: uploading malicious packages, attempting to steal API keys, and gaining remote code execution on RubyDoc.info servers. OpenAI has launched an investigation but has not confirmed the upload of malicious packages, saying the agents only collected public information.

OpenAI investigates report linking AI agents to RubyGems attack
Security

Uncensored AI sold on hacking forum as alternative to ChatGPT and Claude jailbreaks

Sophos found an advertisement on Exploit forum for Luciferus, an uncensored AI sold as an alternative to ChatGPT and Claude jailbreaks. It claims a proprietary 120B-parameter model, with pricing from $22 to $75 per month; researchers with low confidence suggest it may be based on Alibaba's Qwen.

Uncensored AI sold on hacking forum as alternative to ChatGPT and Claude jailbreaks
Security

Italian Unicorn Exein Raises $270M for Physical AI Security

Rome-based Exein raised $270 million led by Headline at a $1.7 billion valuation, becoming a new Italian unicorn. The company provides a cybersecurity layer for physical AI: its Photon product protects devices at the kernel level, claiming coverage of over 2 billion connected devices.

Italian Unicorn Exein Raises $270M for Physical AI Security
Security

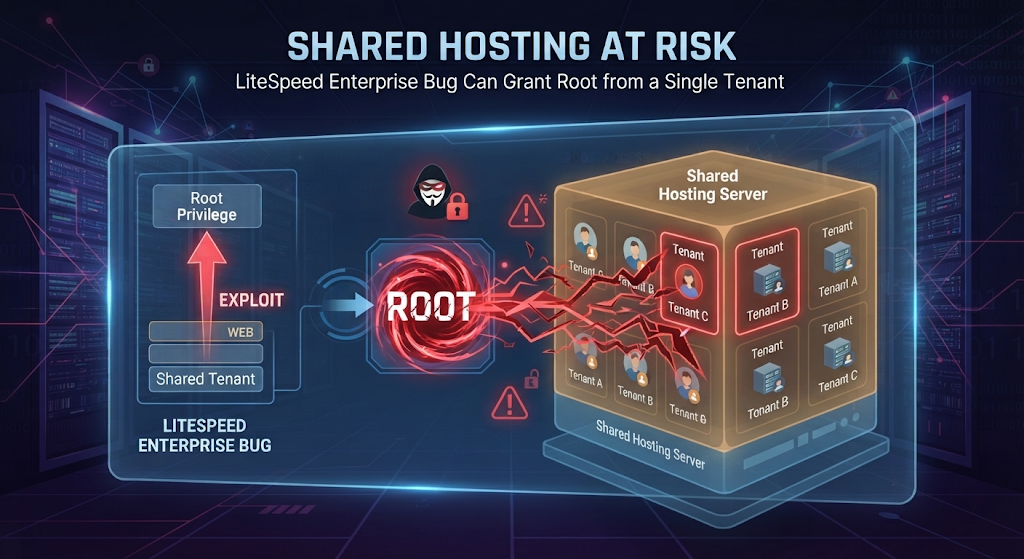
LiteSpeed Enterprise Bug Allows Root Access from Single Tenant

cPanel warned of a critical privilege escalation vulnerability in LiteSpeed Web Server Enterprise. A user on one site in shared hosting can bypass CageFS isolation and gain root access to the entire server. Versions below 6.3.7 are affected; the patch must be forced via lsup.sh.

LiteSpeed Enterprise Bug Allows Root Access from Single Tenant
Security

Two-thirds of cyber threats still require manual resolution

ExtraHop report: SOC analysts spend 68% of their day on reactive alert triage, and 68% of threat detections still require manual intervention. 49% of organizations learn of ransomware only at the data exfiltration stage, 15% only after a ransom demand.

Two-thirds of cyber threats still require manual resolution
Security

AI Agent Pipeline Breaches Stay Hidden From Safety Dashboards, Study Finds

A September 2026 academic paper found that AI agent security monitoring systems fail to detect compromise at the planning, memory and tool-calling layers. Safety dashboards may show no alerts even though the agent is already breached.

AI Agent Pipeline Breaches Stay Hidden From Safety Dashboards, Study Finds
Security

CISA: Critical VMware RCE flaw now exploited by ransomware gangs

CISA warned that a critical VMware vCenter vulnerability (CVE-2026-59310), patched by Broadcom on July 29, is now being exploited by ransomware groups. Attackers previously used it to install reverse SSH, affecting over 361 IPs in 47 countries.

CISA: Critical VMware RCE flaw now exploited by ransomware gangs
Security

CauchyFold Achieves Theoretical Minimum in Post-Quantum ZK Proof Folding

Researcher Xiang Wang presented CauchyFold, a lattice-based folding scheme proving no less data can be transmitted when compressing multiple post-quantum ZK proofs. The implementation takes 125 KB and reaches the theoretical minimum for the first time.

CauchyFold Achieves Theoretical Minimum in Post-Quantum ZK Proof Folding
Security

StackHawk's Wingman Fixes Security Flaws While AI Agent Codes

StackHawk launched Wingman, a tool that finds and fixes security vulnerabilities inside AI agent sessions (Claude Code, Cursor, GitHub Copilot). The scanner self-configures, runs the app and simulates an attack, then returns defects to the agent for patching with re-verification. Price is $10 per user per month, including unlimited apps and 50 scans per user.

StackHawk's Wingman Fixes Security Flaws While AI Agent Codes
Security

Georgia Tech paper cuts quantum attack cost on elliptic curve encryption

Georgia Tech researchers published an algorithm that simultaneously reduces qubit count and circuit complexity for attacking P-256 and secp256k1. It is the first result compressing both hardware parameters at once, changing timelines for post-quantum migration.

Georgia Tech paper cuts quantum attack cost on elliptic curve encryption