Postman Passport controls API access without exposing credentials
Postman announced Passport, a separate product for secure API access. Real keys and tokens remain in the client's infrastructure, while developers and AI agents receive only a cryptographic link tied to their identity. Permissions are granted per action, host, and path; revocation takes seconds.
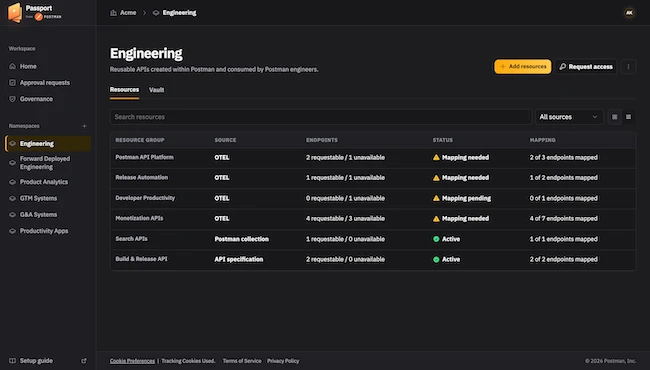
- Secrets stored in client cloud and vault, not transmitted externally
- Permissions configured down to specific action, host, and request path
- Agents get ephemeral identities, sub-agents only part of parent rights
- Access revocation in seconds with full call attribution
Read next
Security