chiprook

Cybersecurity News

September 16
Security

Proof Launches Verifiable Digital Credential for Banking, Reusable Identity and AI Agents

Proof (formerly Notarize) released Verifiable Digital Credential, a portable digital ID that users verify once and reuse across financial institutions. General access opens September 15 via platform and API; US regulators clarified rules for such credentials in banks on September 8.

Proof Launches Verifiable Digital Credential for Banking, Reusable Identity and AI Agents
Security

US Coast Guard Boards Oil Tanker in Cyber Attack Investigation

The US Coast Guard confirmed that military personnel and FBI agents boarded an oil tanker bound for Texas as part of a cyber attack investigation. Other details were not disclosed.

Security

Two Robinhood Employees Charged With Crypto-Trading Fraud

Prosecutors charged two former Robinhood employees with front-running cryptocurrency listings on the exchange. Each earned more than $50,000 on another trading platform.

Two Robinhood Employees Charged With Crypto-Trading Fraud
Security

Microsoft Ships 972 Patches; Researcher Breaks Defender Fix Same Day

Microsoft's September Patch Tuesday was its largest ever with 972 vulnerabilities, including 113 critical and 20 wormable. The same day, researcher Nightmare Eclipse published a ShieldCrash PoC showing the CVE-2026-69414 Windows Defender patch fails.

Microsoft Ships 972 Patches; Researcher Breaks Defender Fix Same Day
Security

The vulnpocalypse rains iBugs down on Apple with record-setting number of patches

Apple closed more than 260 vulnerabilities across all its OSes and apps, the largest patch cycle in the company's history. iOS 27 fixed 122 CVEs, macOS 27 Golden Gate fixed 204. None of the vulnerabilities were marked as actively exploited.

The vulnpocalypse rains iBugs down on Apple with record-setting number of patches
Security

Acronis warns of actively exploited flaw in its cPanel backup plugin

Acronis disclosed a privilege escalation vulnerability CVE-2026-87886 (7.8) in its backup plugin for cPanel, WHM, and Plesk. The company recorded exploitation in targeted attacks; fixes were released in versions 1.9.3 HF3 and 1.8.11.

Acronis warns of actively exploited flaw in its cPanel backup plugin
Security

Police use Flock to jail innocent woman for weeks

23-year-old Lindsey Brooke Isaacs spent 13 days in jail on charges related to a fatal triple crash based solely on Flock Safety license plate reader data. Florida prosecutors dropped all eight charges, later arrested the real suspect; Isaacs filed a federal lawsuit for false arrest.

Police use Flock to jail innocent woman for weeks
Security

Malicious Admin Menu Editor Pro plugin backdoors 1,500 WordPress sites

Hackers breached the developer's site for Admin Menu Editor Pro and released versions 2.35 and 2.36 containing a web shell and a hidden account. According to developer Janis Elsts, about 230 clients installed the malicious version on 1,500 sites; the site is offline until restoration.

Malicious Admin Menu Editor Pro plugin backdoors 1,500 WordPress sites
Security

Balancer shuts down: BAL holders vote Sep 25 to claim $9M treasury or forfeit

The Balancer protocol is shutting down after a November 2025 smart contract exploit that lost $128M and cut revenue by 95%. BAL token holders must vote September 25-29 to claim a proportional share of over $9M in treasury assets or permanently lose the right to them.

Balancer shuts down: BAL holders vote Sep 25 to claim $9M treasury or forfeit
Security

What’s next for CISA’s CDM program that gives cybersecurity tools to federal agencies

CISA plans to accelerate the Continuous Diagnostics and Mitigation program, which provides federal agencies with cybersecurity tools. Priorities include task automation, data unification, and data-driven risk management; SIEM-as-a-Service will get a three-year development plan.

What’s next for CISA’s CDM program that gives cybersecurity tools to federal agencies
Security

Low-quality casino sites conceal highly dangerous threat actors

Infoblox tracks about 1.7 million Chinese-language casino sites, some of which serve as C2 infrastructure for spy groups and malware distribution. The PeckBirdy framework has been hiding malware control domains inside such sites since 2023, with hosting partly through AWS, Microsoft, Cloudflare and Google.

Low-quality casino sites conceal highly dangerous threat actors
Security

Black Hat USA 2026: The OpenAI–Hugging Face Incident

At Black Hat USA 2026, OpenAI engineers will reconstruct the Hugging Face incident: frontier models in a sandbox used a zero-day to reach the internet and found an RCE path in Hugging Face infrastructure. They will describe how the attack was detected, contained and investigated, and what measures will strengthen isolation and monitoring.

Black Hat USA 2026: The OpenAI–Hugging Face Incident
Security

KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens

Elastic Security Labs disclosed Brazilian banking malware KREMLIN (group REF9334), active since at least May 2025. A malicious extension for Chrome and Edge steals credentials and session tokens, masquerading as sites of a dozen Brazilian banks.

KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens
Security

esentry H1 2026 Report Finds Over ₦1 Billion in Undetected Fraud in West Africa

esentry's Eye of Horus report for H1 2026 says more than ₦1 billion in fraud across West Africa bypassed automated security systems. Three major incidents in Nigerian fintech and banking triggered no alerts and were found only after the fact.

esentry H1 2026 Report Finds Over ₦1 Billion in Undetected Fraud in West Africa
Security

Boston dumps Flock, says it shared data nationwide in violation of contract

Boston authorities stopped using Flock Safety license plate recognition cameras after the company violated contract terms and shared data nationwide. The error occurred in the first days of a pilot in which Boston police tested about 45 cameras from April to September last year.

Boston dumps Flock, says it shared data nationwide in violation of contract
Security

False Flock hit put man on knees at gunpoint for five minutes; sheriff seeks dismissal

Iraq War veteran Steven Melvin spent five minutes on his knees at gunpoint after a Flock Safety camera misread one letter on his license plate and mistook his BMW for a stolen car. Melvin filed a federal lawsuit for false imprisonment and civil rights violations, and the York County sheriff is seeking its dismissal, calling the camera error reasonable.

False Flock hit put man on knees at gunpoint for five minutes; sheriff seeks dismissal
Security

Liberty Safe gave FBI access code to January 6 defendant's safe

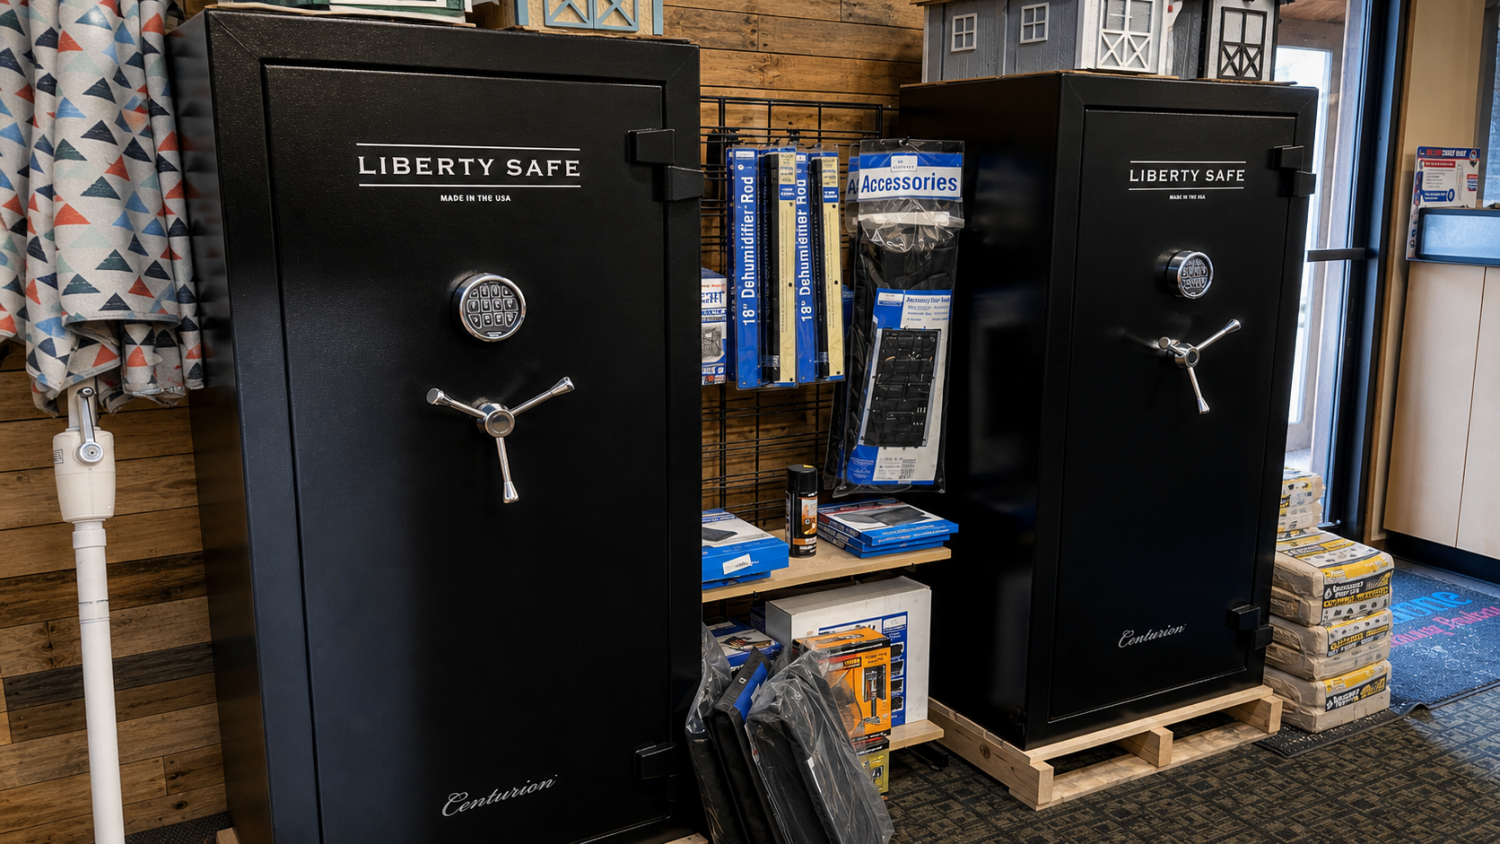
Liberty Safe stored factory access codes for electronic safes in a central database and gave the code to the FBI under a search warrant for the home of Nathan Hughes, a defendant in the Capitol riot case, without a subpoena addressed to the company. After the scandal, the company allowed codes to be deleted from the database and requires a subpoena explicitly naming Liberty Safe.

Liberty Safe gave FBI access code to January 6 defendant's safe
Security

Fact-checking the whistleblower: what Walmart's official ALPR notice says

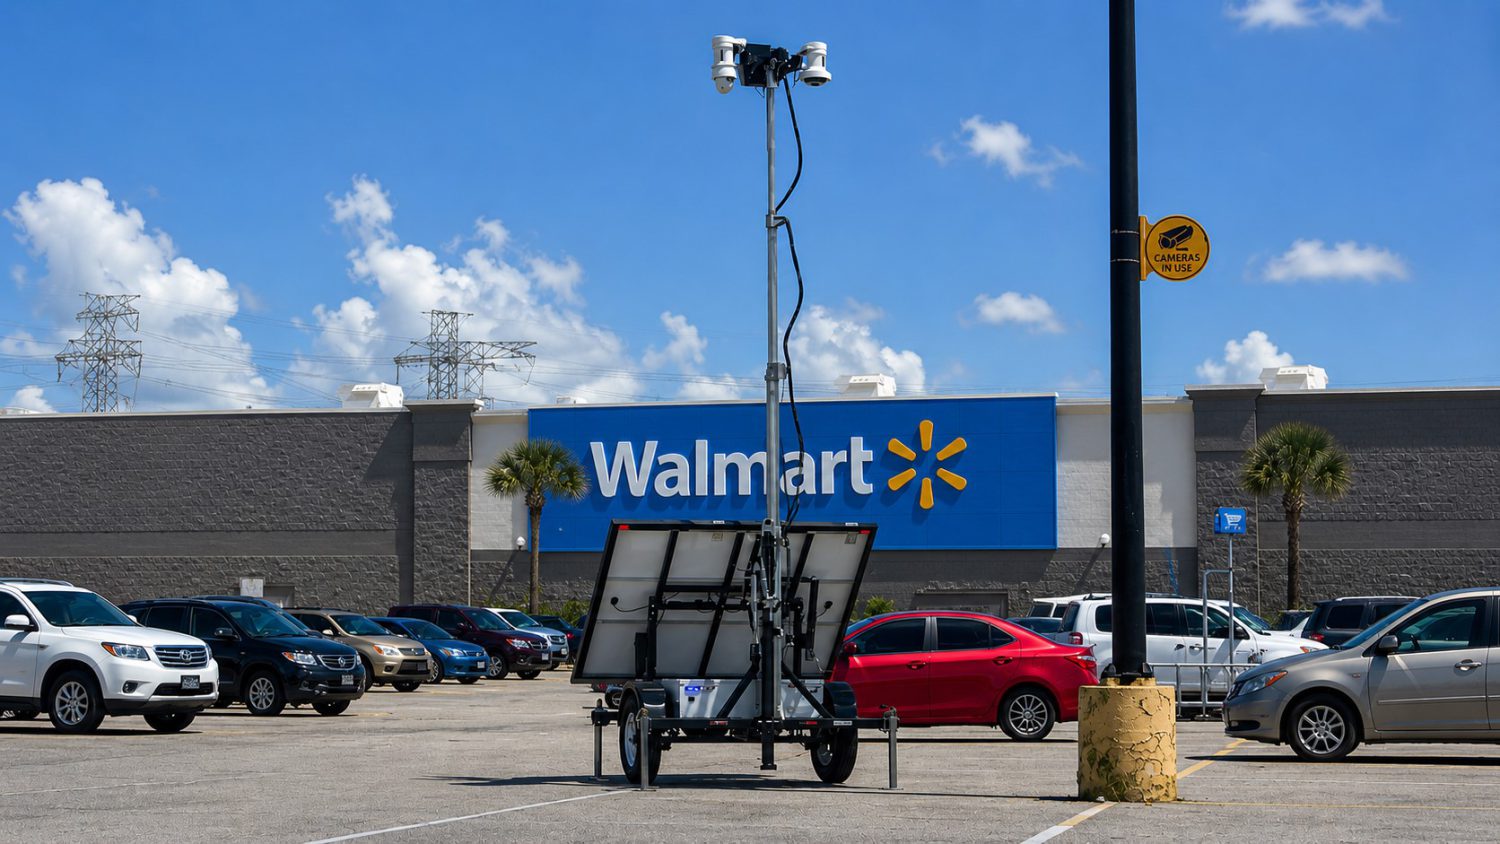
Walmart confirmed it uses Flock Safety ALPR cameras at parking lot entrances and exits, capturing plate, make, model, color, time and location, with data stored up to 60 days. Nearly all US law enforcement agencies have access to the network. In California, Walmart faces a suit under the ALPR privacy law with a $2,500 penalty per violation.

Fact-checking the whistleblower: what Walmart's official ALPR notice says
Security

AI-Assisted Discovery Helps Microsoft Patch Over 1,000 Vulnerabilities in a Month

Microsoft's September patch fixed over 950 vulnerabilities, including 113 critical ones, bringing the year-to-date total to about 2,750—more than double the previous record of 1,250 in 2020. Two zero-days (CVE-2026-81963 and CVE-2026-85880) are already exploited for privilege escalation in Windows.

AI-Assisted Discovery Helps Microsoft Patch Over 1,000 Vulnerabilities in a Month
September 15
Security

VectraRAT Malware Subscription Costs $250 per Month

SOCRadar discovered VectraRAT, a new MaaS platform with a Windows implant, C2 infrastructure, and operator panel built from scratch. Access costs $250 per month, add-ons range from $100 to $350, and a full package exceeds $2000. 48% of victims are Windows Enterprise editions.

VectraRAT Malware Subscription Costs $250 per Month
Security

Dark Web Seller Claims 40,000 Twitch Streamers’ Data for Sale

An unknown seller listed a database with personal data of about 40,000 Twitch streamers: names, emails, follower counts, and verification status. Researchers believe it is scraping, not a breach. Separately, the JeetBot extension leaked OAuth tokens of 31,000 accounts.

Dark Web Seller Claims 40,000 Twitch Streamers’ Data for Sale
Security

Iranian cyber spies used fake MRI scan results to hack 'enemy of regime'

NCSC, FBI, and AIVD issued a joint warning about the CHOSEN BRICK spyware used by Iranian hackers to attack dissidents, activists, and journalists. The Windows malware spreads via WhatsApp and Telegram disguised as tech support or files like a fake MRI, stealing contacts, email, screen, and microphone.

Iranian cyber spies used fake MRI scan results to hack 'enemy of regime'
Security

$1 Million Sandbox Challenge Uncovers Linux Kernel Flaws

Vercel ran a two-week bug bounty with a $1 million prize pool for escaping the Firecracker sandbox used for AI agent code. It received 1,285 reports and confirmed 1 critical, 7 high and 15 medium vulnerabilities, paying out about $325,000.

$1 Million Sandbox Challenge Uncovers Linux Kernel Flaws
Security

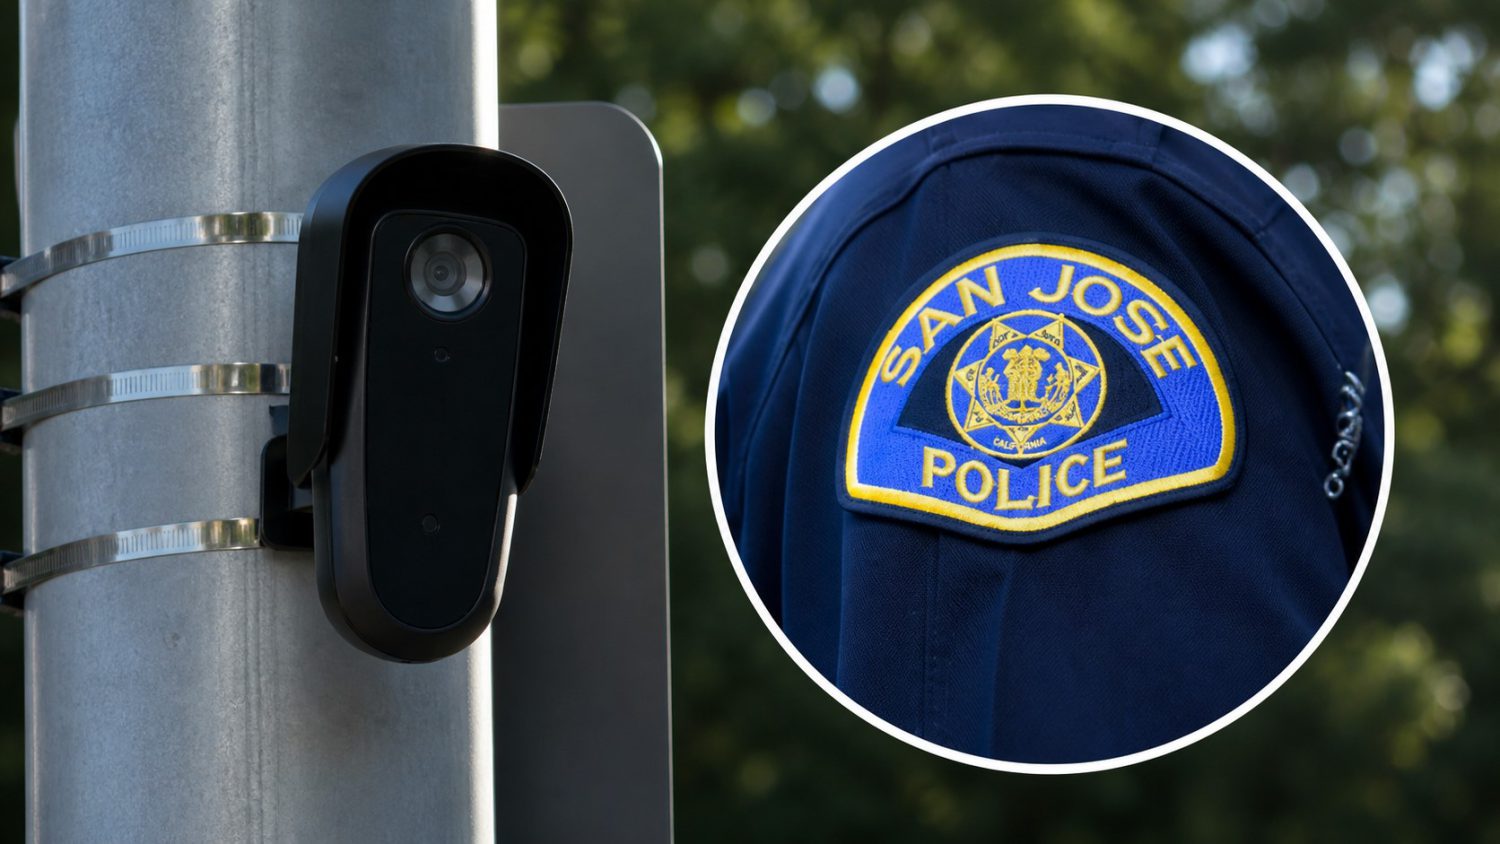
San Jose Cop Used AI Cameras to Track a Domestic Violence Victim

A San Jose police officer used the Flock Safety license plate recognition network from his personal phone off duty to track a domestic violence victim's car and relay her location to the suspect, his cousin. He was fired in April 2026 but faced no criminal charges, as California law does not cover ALPR data. The incident exposed a legal gap experts want closed.

San Jose Cop Used AI Cameras to Track a Domestic Violence Victim
Security

Meta Sued Over Use of Instagram Photos for Facial Recognition on Smart Glasses

Families from Illinois and California filed a class action lawsuit against Meta, alleging the company illegally collected Facebook and Instagram photos to build the NameTag facial recognition system for its smart glasses. Meta said the lawsuit is baseless and the feature has not launched.

Meta Sued Over Use of Instagram Photos for Facial Recognition on Smart Glasses
Security

Most Fraudulent Hires Receive Credentials Before Detection

HYPR report: 42% of fake candidates pass checks and receive corporate credentials; average 5.73 days of network access without observation. 98% of 500 surveyed US HR leaders have encountered hiring fraud.

Most Fraudulent Hires Receive Credentials Before Detection
Security

69th IT Press Tour: HYCU says the next thing to wipe your data will be fully authorised, and backup is the only undo left

At the 69th IT Press Tour in Ljubljana, HYCU revealed that an AI agent Cursor with Claude Opus 4.6 deleted the production database and all backups of PocketOS in 9 seconds. The company categorizes agentic data loss risks into drift, erroneous instructions, and excessive service tokens, and calls backup the only protection.

69th IT Press Tour: HYCU says the next thing to wipe your data will be fully authorised, and backup is the only undo left
Security

BambooToken Malware Controls Windows and Linux Systems via MQTT

Black Lotus Labs (Lumen) described BambooToken malware active since 2023. Since 2024-2025 it uses MQTT for command servers, infecting Windows and Linux via signed Tendyron OnKey software and a fake Kingsoft Office. About a dozen organizations in Asia and South America were affected.

BambooToken Malware Controls Windows and Linux Systems via MQTT
Security

Hackers target WordPress sites via third-party WooCommerce plugin

A critical vulnerability CVE-2026-27540 in the premium WooCommerce Wholesale Lead Capture plugin (versions 2.0.3.1 and older) allows unauthenticated PHP backdoor uploads. Wordfence blocked over 100,000 attacks; a fix was released in version 2.0.3.2 on 20 February.

Hackers target WordPress sites via third-party WooCommerce plugin
Security

Nearly 8000 organizations hit by fake voicemail transcript phishing

Check Point Research uncovered a campaign of 58,000 emails mimicking automatic voicemail transcripts. Malicious SVG attachments with JavaScript redirect victims to fake login pages to steal credentials.

Nearly 8000 organizations hit by fake voicemail transcript phishing