chiprook

Cybersecurity News

September 17
Security

Cisco Fixes Dozens of Flaws Across FMC, ISE and Nexus Dashboard

Cisco released patches for dozens of critical vulnerabilities in Secure Firewall Management Center, Identity Services Engine and Nexus Dashboard. ISE has 20 CVEs, including 12 critical; three were publicly disclosed, and an authentication bypass was exploited as a zero-day.

Cisco Fixes Dozens of Flaws Across FMC, ISE and Nexus Dashboard
Security

Cyber Essentials Has Record Year but Takeup Remains Low

The UK Cyber Essentials certification scheme issued a record 61,430 certificates from July 2025 to June 2026, up 20% year over year. Nearly three-quarters were recertifications, and coverage remains low against 5.7 million UK SMEs.

Cyber Essentials Has Record Year but Takeup Remains Low
Security

Israeli contractor BlackCore trained Angolan officials in online influence operations

Citizen Lab reports that Israeli firm BlackCore ran a 14-week course for Angolan officials on running online influence campaigns, including creating fake personas and advertising on Facebook, Instagram and TikTok. Participants produced over 40 items, with some posts reaching up to 50,000 likes.

Israeli contractor BlackCore trained Angolan officials in online influence operations
Security

Inside Google’s faster Chrome patch strategy to block AI attacks on your browser

Google cut Chrome's update cycle from four to two weeks to reduce the window between vulnerability disclosure and patch. The reason is AI agents that find and exploit vulnerabilities in hours instead of weeks, and scale targeted phishing. The company is also considering dynamic patch installation without restarting the browser.

Inside Google’s faster Chrome patch strategy to block AI attacks on your browser
Security

Malicious JavaScript evaded VirusTotal in seven of eight storefront attacks

A study found malicious JavaScript campaigns on e-commerce storefronts evaded VirusTotal in 7 of 8 cases, exposing a weakness in signature scanning. Cloudflare's graph neural network caught all eight payloads in real time, while URLScan detected none.

Malicious JavaScript evaded VirusTotal in seven of eight storefront attacks
Security

Scammers Pose as Airline Support to Steal Credit Card Info

Check Point warned of a scam campaign where fraudsters impersonate airline customer support on social media. Hundreds of fake accounts are created daily, victims are led to private chats, and payment data is stolen.

Scammers Pose as Airline Support to Steal Credit Card Info
Security

Chinese Counterfeit Cosmetics Sold on Coupang, Naver

South Korea's Ministry of Food and Drug Safety and Intellectual Property Office detained a broker who sold Chinese counterfeit cosmetics, supplements, and electronics on Coupang and Naver. From October 2024 to November 2025, 61 product types worth 4.5 billion won ($3.25 million) were sold, and 18,124 units were seized.

Chinese Counterfeit Cosmetics Sold on Coupang, Naver
Security

US takes down NightmareStresser DDoS-for-hire platform

The FBI seized the domains of NightmareStresser, one of the oldest DDoS-for-hire platforms. The service, with over 566,000 registered users, was used for hundreds of thousands of attacks since 2022; the operation was part of Operation PowerOFF.

US takes down NightmareStresser DDoS-for-hire platform
Security

Hackers find encryption keys on stolen Flock camera despite denials

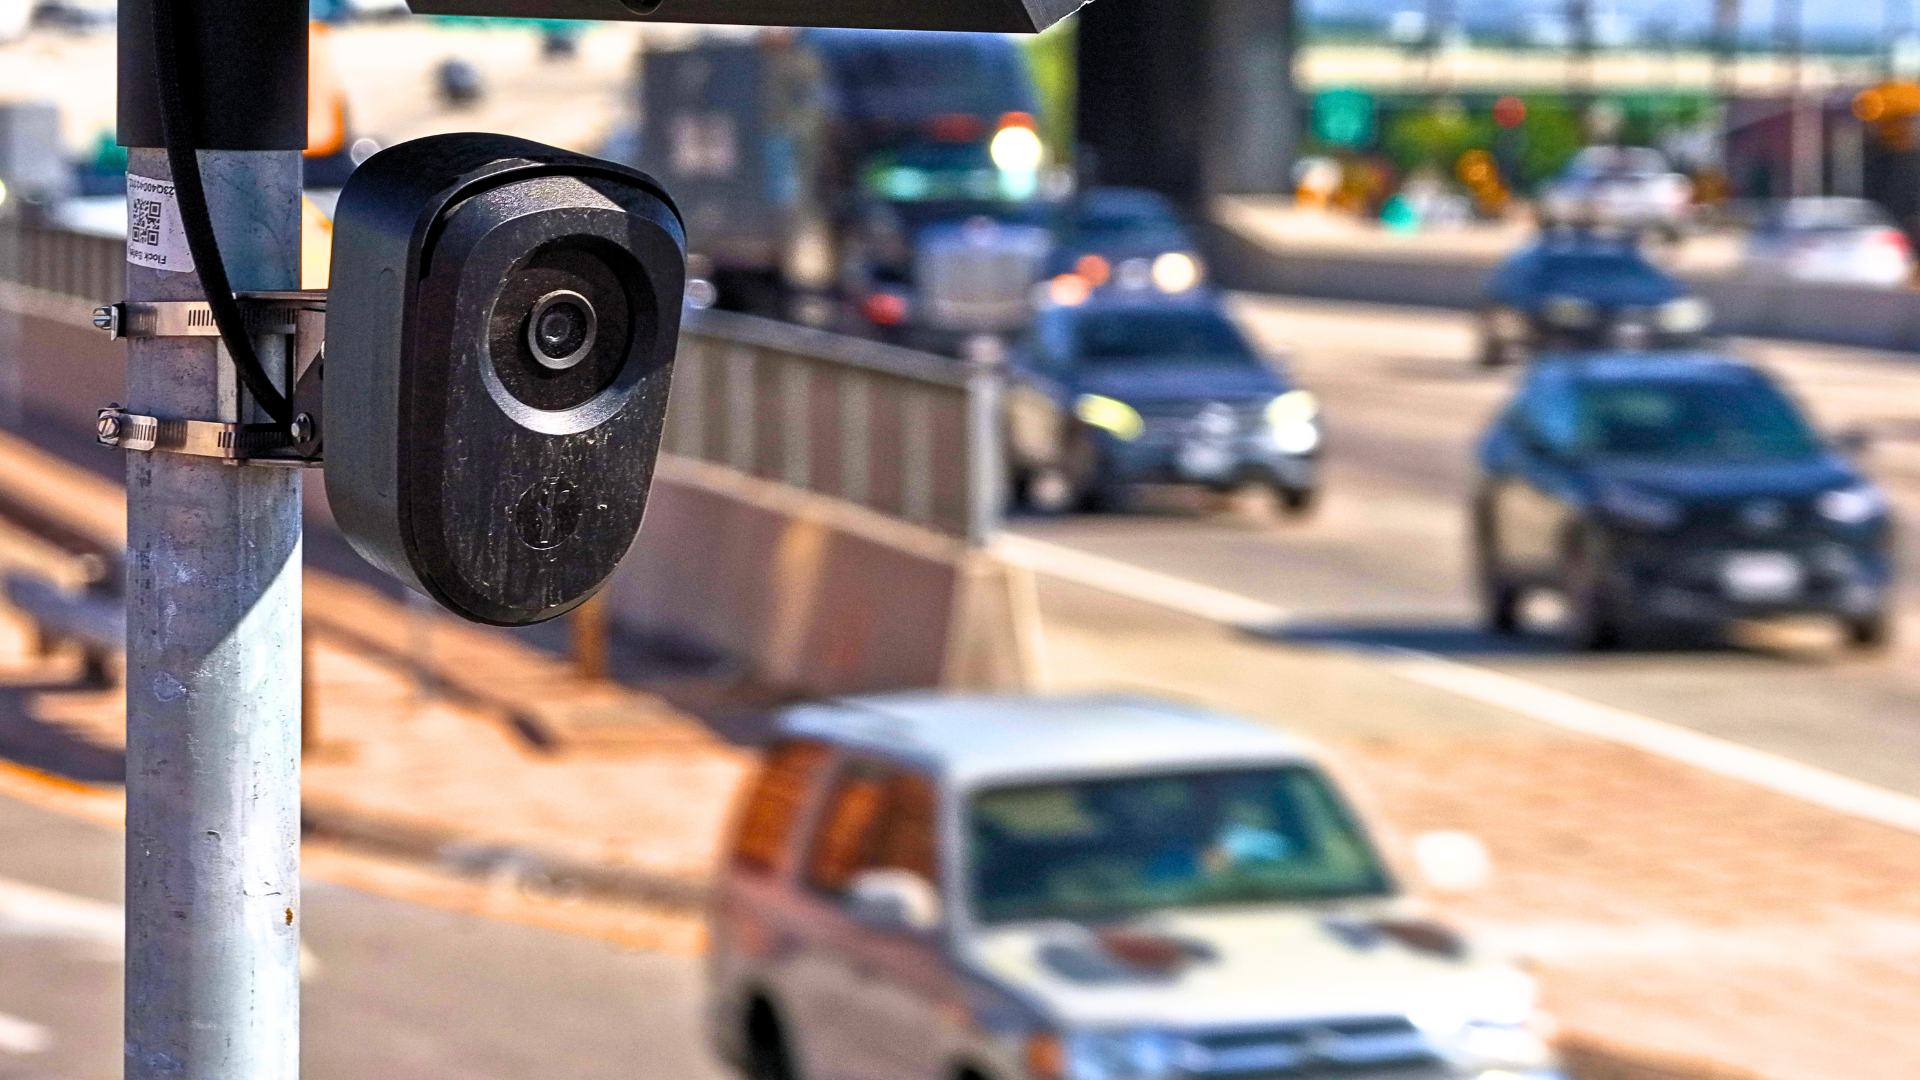
Group stegan0gram removed a Flock camera from a road and extracted an encryption key from the 'media' partition, gaining access to 1.6 million images and 27,321 video clips over 21 days. Flock had previously claimed data is protected by on-device encryption and stored only briefly.

Hackers find encryption keys on stolen Flock camera despite denials
Security

Third-party cyber breaches hit South African firms

South African financial and telecom companies EasyEquities, Satrix, Cell C and Alexforbes warned clients of possible personal data leaks from third-party supplier incidents. At Alexforbes client data was affected via RelyComply, at EasyEquities via a verification provider; the companies' own systems were not compromised.

Third-party cyber breaches hit South African firms
Security

Scammers leave AI fingerprints all over fake antivirus renewal page

Malwarebytes discovered a fake page mimicking Avast Premium Security renewal for €129.99 targeting users in Belgium. Code and text indicate the page was created with AI: the form does not submit data, French comments remain, and extra styles are present.

Scammers leave AI fingerprints all over fake antivirus renewal page
Security

Fake SARS e-mails get smarter this tax season

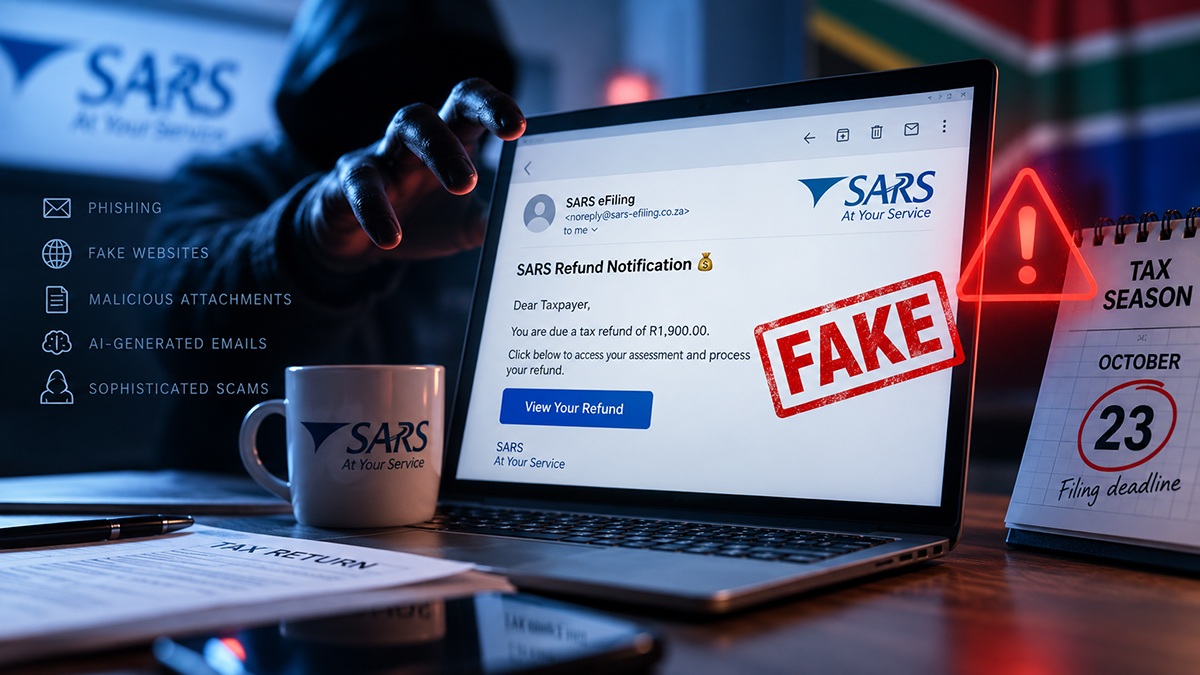
Kaspersky warned of a phishing wave impersonating the South African Revenue Service (SARS) ahead of the October 23 filing deadline. AI helps scammers create convincing emails and sites, and uploading tax documents to chatbots risks leaking personal data.

Fake SARS e-mails get smarter this tax season
Security

Malicious npm Package Found in Job Take-Home Test

A developer discovered malicious code in transitive dependency @aaron205whitmore/postcss-animate-utils@1.0.2, pulled via animatecss-tailwind-adapter@2.0.6 in a take-home test from Antfarm DAO. The package connects to 153.75.81.2:1224 and can execute arbitrary JavaScript via new Function.

Malicious npm Package Found in Job Take-Home Test
Security

CISA adds Acronis Backup, Cisco ISE, and Google Pixel flaws to Known Exploited Vulnerabilities catalog

CISA added three vulnerabilities to its Known Exploited Vulnerabilities catalog: authentication bypass in Cisco ISE (CVSS 10.0), privilege escalation in Acronis Backup, and privilege escalation in Google Pixel modem (CVSS 8.8). All three are exploited in real attacks; U.S. federal agencies must remediate by deadline.

CISA adds Acronis Backup, Cisco ISE, and Google Pixel flaws to Known Exploited Vulnerabilities catalog
Security

Microsoft CEO on AI safety: why agents are insider risks

Microsoft CEO Satya Nadella explained why AI agents create new security risks and represent an insider threat. He also noted that avoiding vendor lock-in is critical for margin control.

Microsoft CEO on AI safety: why agents are insider risks
Security

Chinese hackers use SparroWocky malware in govt espionage attacks

China-linked group FamousSparrow has attacked government organizations in Latin America for over a year with a new backdoor, SparroWocky, replacing SparrowDoor. ESET recorded targets in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico and Venezuela, plus 18 C2 addresses.

Chinese hackers use SparroWocky malware in govt espionage attacks
Security

Flock Once Touted Its Cameras as 'Made in the USA.' Now It's Not So Clear

WIRED found that Flock Safety, which for years claimed its cameras were made in the USA, removed those statements from its marketing. Import records show growing shipments of cameras and radars from Taiwan's Primax Electronics, which has factories in Thailand and China.

Flock Once Touted Its Cameras as 'Made in the USA.' Now It's Not So Clear
Security

3,988 Hypervisor Consoles on the Open Internet: ZoomEye on Exposed Proxmox VE

Search engine ZoomEye found 3,988 hosts with open port 8006, the Proxmox VE web management interface. An authentication bypass vulnerability affects versions 7.x-8.0.3, and for such hosts an attack is possible with a single HTTP request.

3,988 Hypervisor Consoles on the Open Internet: ZoomEye on Exposed Proxmox VE
Security

Fake AI Trading Agent Steals Crypto Wallet Passwords

HP uncovered an April–June 2026 campaign: tradingclaw[.]pro offered an installer for a fake AI crypto trading agent, but it contained a Microsoft-signed OLEView that used DLL side-loading to run Needle Stealer. The malware swaps extensions in seven browser wallets, including MetaMask, Coinbase Wallet and Phantom, and sends passwords to attackers.

Fake AI Trading Agent Steals Crypto Wallet Passwords
Security

ChainDrop npm Worm Hijacks 444 Packages with 2B Monthly Downloads

The ChainDrop worm, a variant of the Shai-Hulud attack, has taken over publishing rights for 444 npm packages with approximately 2 billion monthly downloads. Infection is triggered via malicious hooks in Claude Code and VS Code when opening a compromised branch or starting a session.

ChainDrop npm Worm Hijacks 444 Packages with 2B Monthly Downloads
Security

Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records

Helpfeel reported a breach of image-sharing service Gyazo. About 23.62 million user records with email and password hashes, and approximately 490 million image metadata records, mostly uploaded before January 2019, including image link IDs, were leaked.

Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records
Security

Repeated VM Escapes By GPT-5.6-Cyber Based Agents Prove VMs and OS' Require Better Maintenance

Researchers tested an autonomous agent based on GPT-5.6-Cyber against QEMU/KVM on Linux: it searched for vulnerabilities for hours and made multiple sandbox escapes by exploiting kernels and zero-days. In Firecracker, the agent was contained but still froze the machine due to Linux kernel bugs.

Repeated VM Escapes By GPT-5.6-Cyber Based Agents Prove VMs and OS' Require Better Maintenance
Security

Active Exploitation Triggers Emergency Patch for Cisco ISE Zero-Day

Cisco released emergency patches for a critical authentication bypass vulnerability CVE-2026-76460 (CVSS 10/10) in Identity Services Engine, which is already being exploited. The attack allows bypassing the web management interface and gaining access to the device, including root privileges. CISA added the vulnerability to its KEV catalog and requires US federal agencies to patch it within three days.

Active Exploitation Triggers Emergency Patch for Cisco ISE Zero-Day
Security

2,967 MCP servers advertise OAuth; only 8% meet July spec

A scan of the official MCP registry found 32,380 unique servers, of which 2,967 claim OAuth support. Only 8% fully comply with the July 28, 2026 specification, including CIMD and RFC 9207.

2,967 MCP servers advertise OAuth; only 8% meet July spec
Security

Port of LA foiled around 120 million cyberattacks last month

The largest US container port said it repelled more than 120 million cyberattack attempts in August. The attacks pose a constant threat to port operations amid shifting tariff policy.

Security

Microsoft wants organizations to ditch traditional VPNs for Entra Private Access

Microsoft is urging organizations to abandon traditional VPNs in favor of Entra Private Access, citing security risks when employees connect to private resources.

Microsoft wants organizations to ditch traditional VPNs for Entra Private Access
Security

mySCADA myPRO Manager: Two Missing-Authorization Flaws in an ICS Management Platform

CISA warned about two missing-authorization vulnerabilities in mySCADA myPRO Manager — CVE-2026-73807 (CVSS 9.8) and CVE-2026-82567 (CVSS 6.3). Both allow acting without credentials if network access is available; a fix was released in version 2.2, and no exploitation cases have been recorded.

mySCADA myPRO Manager: Two Missing-Authorization Flaws in an ICS Management Platform
Security

CVE-2026-19490: NetScaler SAML Bypass Detection and Mitigation

An authentication bypass via SAML (CWE-288, CVSS 9.3) has been found in NetScaler ADC and Gateway: the device accepts an assertion without a valid signature and grants a session as any user. Citrix issued bulletin CTX696939, and CISA added the vulnerability to its exploited catalog on September 9, 2026.

CVE-2026-19490: NetScaler SAML Bypass Detection and Mitigation
Security

161,764 Assets on Port 102: Sizing the Industrial Control Surface That AA26-231A Described

ZoomEye measured the industrial controller surface described in joint advisory AA26-231A from NSA, CISA, FBI, DOE, and EPA. Port 102 is accessible on 161,764 devices, 95,395 classified as PLCs, but only 173 match the Siemens S7 fingerprint.

161,764 Assets on Port 102: Sizing the Industrial Control Surface That AA26-231A Described
Security

Two RouterOS Bugs, One Escalation Path: What CVE-2026-67277 and CVE-2026-86060 Mean for Edge Routers

NVD published CVE-2026-86060 (CVSS 9.8) and CVE-2026-67277 (CVSS 8.2) in MikroTik RouterOS. The first allows privilege escalation via a username parsing error in SSH; the second allows running a UDP test without authentication and obtaining uninitialized data from the kernel buffer. The fix is updating firmware and closing SSH and btest from the internet.

Two RouterOS Bugs, One Escalation Path: What CVE-2026-67277 and CVE-2026-86060 Mean for Edge Routers