chiprook

Cybersecurity News

September 18
Security

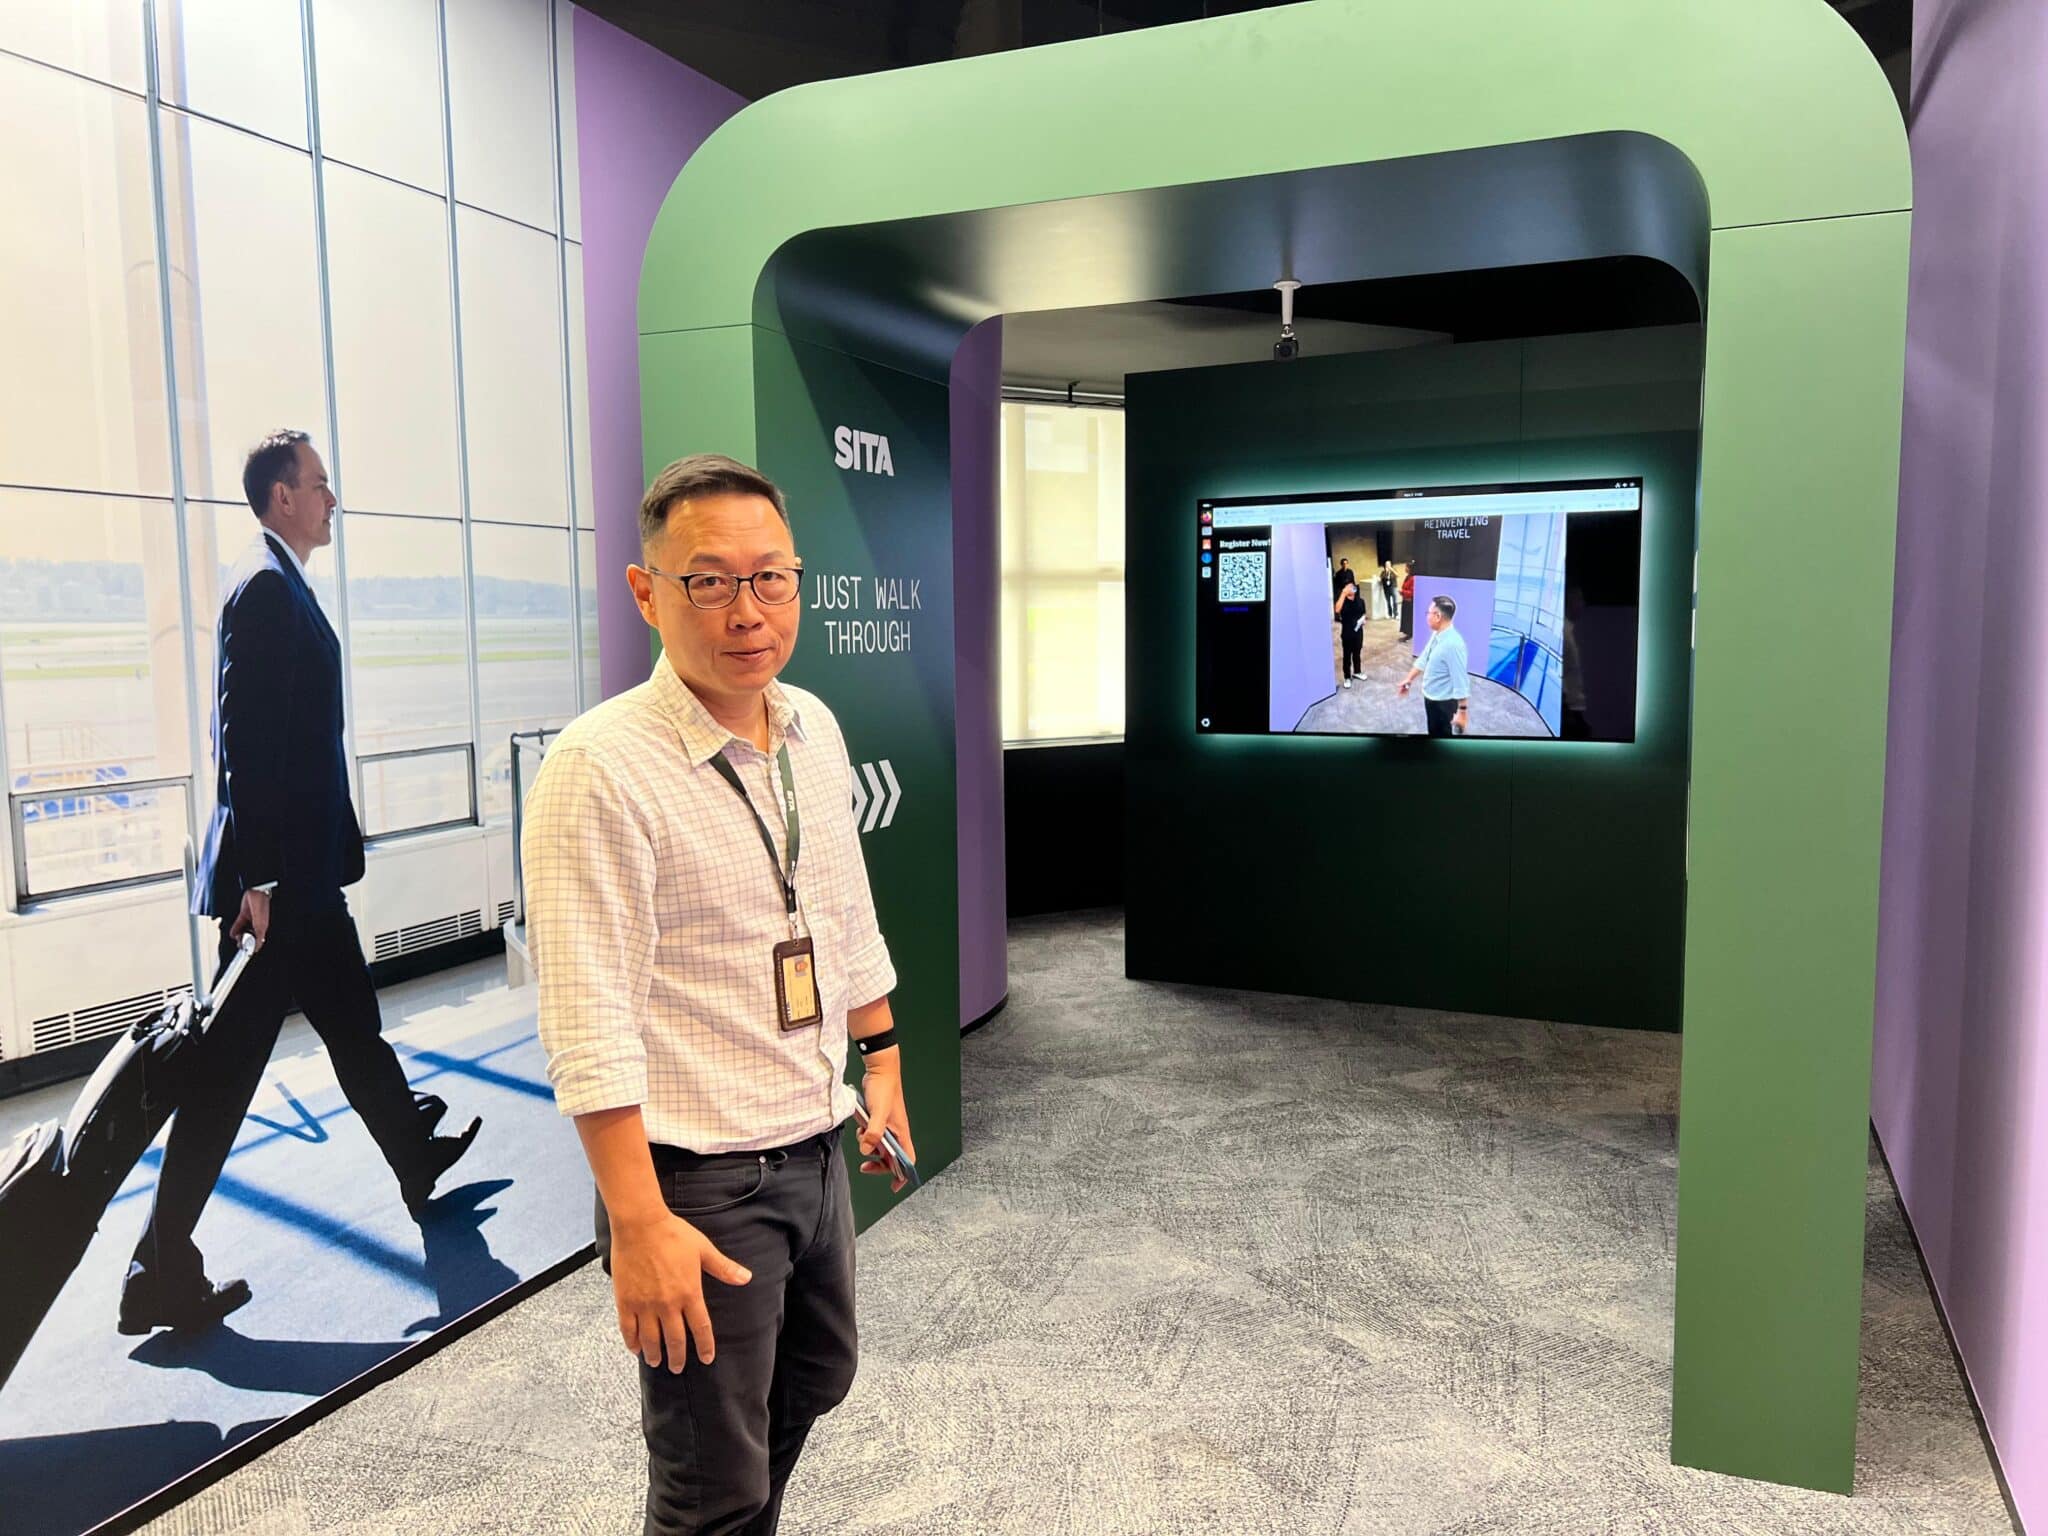
SITA launches walk-through biometric border processing system

SITA introduced Border Flow Lane, a biometric border control system that verifies passenger identity while they walk, without stopping at counters or eGates. It is up to 8 times faster than standard eGates and allows border officers to process over 75% of passengers before departure. SITA seeks government partners for pilots.
SITA launches walk-through biometric border processing system
Security

Patching Check Point VPN flaws: prioritized plan for CVE-2026-85102 and CVE-2026-85103

CERT-In warned about two critical Check Point VPN vulnerabilities (CVE-2026-85102 and CVE-2026-85103): an unauthenticated attacker can execute code via a forged certificate. Patches are in articles sk1000117 and sk1000118; unsupported versions R80–R81.10 require migration.

Patching Check Point VPN flaws: prioritized plan for CVE-2026-85102 and CVE-2026-85103
Security

LGT Financial Services grounds post-quantum migration in live banking pilot

LGT Financial Services deployed hybrid X25519 key exchange with the post-quantum ML-KEM mechanism in online banking, with the pilot running without failures for customers. The company began preparing for the quantum threat in 2022 and created a quantum security competence center.

LGT Financial Services grounds post-quantum migration in live banking pilot
Security

Same Flaw Found in Claude Code, Codex, Gemini CLI and GitHub Copilot

Startup Air found the same flaw in how four AI coding agents from Anthropic, OpenAI, Google and Microsoft handle skills. The vulnerability allowed hijacking another user's agent without the owner noticing; it is now mostly fixed.

Security

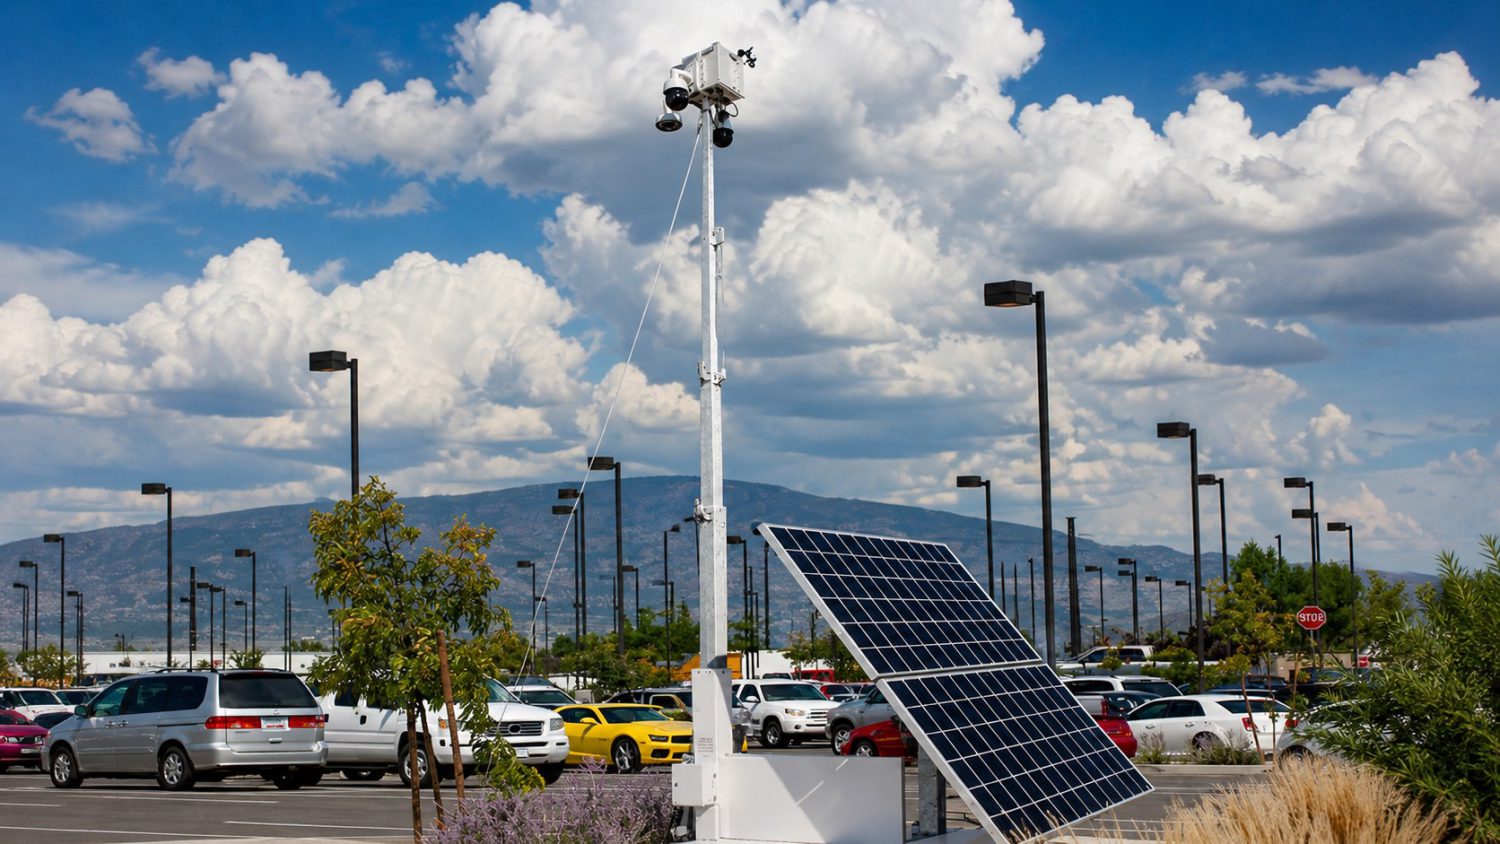
Parking lot security towers stream live data to police

An investigation found that autonomous camera towers from LiveView Technologies and Flock Safety stream video and license plates to private clouds, where police and federal agencies access them via platforms like Axon Fusus. NCRIC made over 27,000 queries to the Santa Ana ALPR network in six months, and the Western States Information Network illegally shared data outside California.

Parking lot security towers stream live data to police
Security

Google patches 42 Chrome security flaws including three critical bugs

Google released Chrome 153.0.8010.47/48 for Windows and macOS and 153.0.8010.47 for Linux and Android, fixing 42 vulnerabilities, of which three are critical and 28 high risk. No signs of active exploitation were recorded; $2,500 was paid for external reports.

Google patches 42 Chrome security flaws including three critical bugs
Security

Brevo supply-chain attack injected ClickFix scripts on customer sites

Attackers stole a long-lived Cloudflare API key hardcoded in Brevo's source code and, via a malicious Cloudflare Worker, replaced content on brevo.com, sendinblue.com, and sibforms.com for about 5.5 hours, as well as in form scripts and widgets embedded on customer sites. Sansec estimates up to 100,000 sites may be affected; visitors saw a fake Cloudflare check and ClickFix instructions.

Brevo supply-chain attack injected ClickFix scripts on customer sites
September 17
Security

Scammers Insert AI Songs on Real Artists' Spotify and Other Platform Pages

According to 404 Media, scammers use distributors like DistroKid to upload AI-generated tracks to real musicians' pages on Spotify, Apple Music and Tidal to collect royalties. The band Odette Child found over 300 such songs, including Taylor Swift fakes. Spotify is testing a pre-release review tool.

Scammers Insert AI Songs on Real Artists' Spotify and Other Platform Pages
Security

Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files

Docker warned of CVE-2026-77179 in Docker Sandboxes for macOS: malicious code inside a virtual machine can escape the shared project folder and read or modify any host files with the privileges of the account that launched the VM. The issue is rated critical.

Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Security

Security Spending Grows Overall, But Typical CISO Sees No Increase

According to the IANS and Artico Search 2026 Security Budget report, based on a survey of over 500 security leaders (April–August 2026), average security budget growth was 5%, but median growth was 0%. 64% of CISOs requested increases, but only 45% received them. AI was the top priority for new spending, cited by 69% of respondents.

Security Spending Grows Overall, But Typical CISO Sees No Increase
Security

London Property Manager Breach May Have Exposed Bank Details and Lockbox Codes

London property manager City Relay reported two breaches of its Metabase Cloud instance. Attackers may have stolen bank details, passwords, and lockbox access codes; the company changed access codes and notified clients on September 14.

London Property Manager Breach May Have Exposed Bank Details and Lockbox Codes
Security

A Prompt Injection Turned Into a Shell: Inside Semantic Kernel's Two RCE CVEs

Microsoft disclosed CVE-2026-26030 and CVE-2026-25592 in the Semantic Kernel framework: LLM output was passed to eval() in a vector search filter and to a file download path without validation, allowing code execution. Fixes were released in Python SDK 1.39.4 and .NET SDK 1.71.0.

A Prompt Injection Turned Into a Shell: Inside Semantic Kernel's Two RCE CVEs
Security

SilkParasite infrastructure links SpiceRAT to Central Asian targets

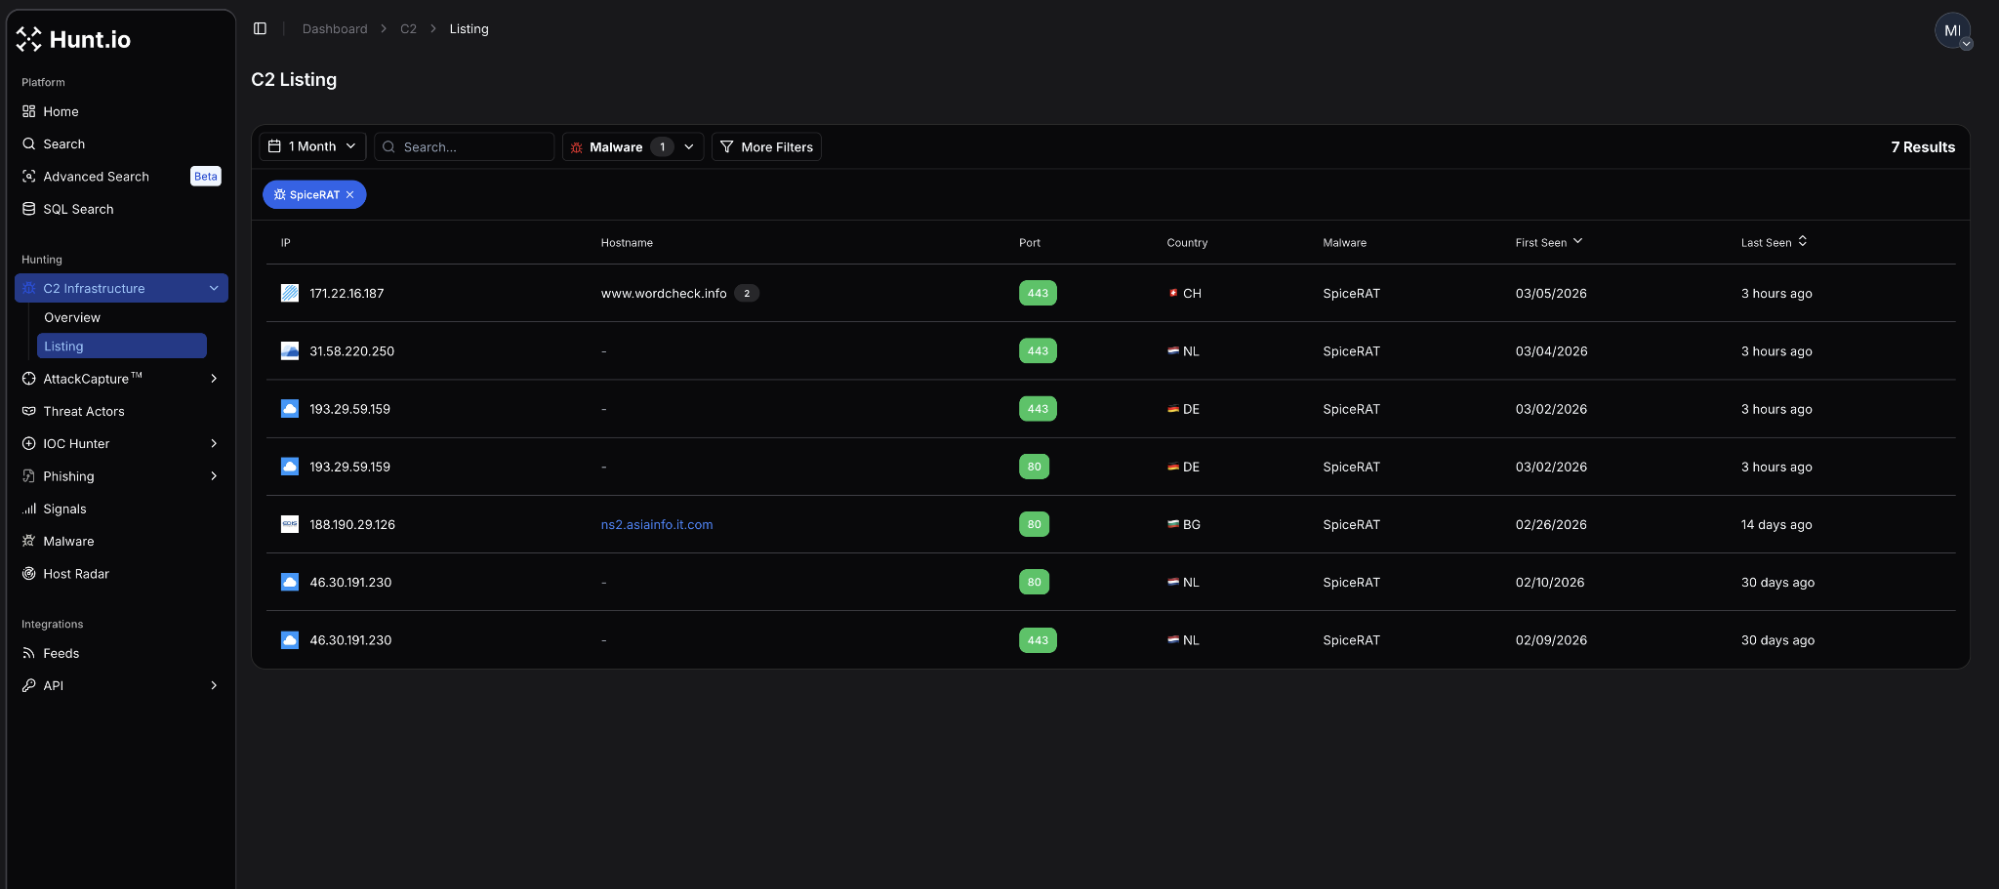
Hunt.io and researcher Guy Yassur linked C2 servers for SpiceRAT, NodeEdgeRAT and NomadRAT through shared domains, TLS certificates and hosting. The SilkParasite campaign has targeted government and critical-sector organizations in Central Asia since 2022, including Uzbekistan Railways and Turkmenistan's Foreign Ministry.

SilkParasite infrastructure links SpiceRAT to Central Asian targets
Security

SonicWall: Patch Is Only Step One of Four for SMA 1000 Flaws

SonicWall disclosed two exploited vulnerabilities in SMA 1000 gateways: CVE-2026-83548 (CVSS 10.0) and CVE-2026-83549 (CVSS 7.8). CISA added the critical flaw to its KEV catalog on September 3. The vendor recommends patching, reinstalling the device, changing passwords, and reissuing TOTP tokens.

SonicWall: Patch Is Only Step One of Four for SMA 1000 Flaws
Security

Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor

Iranian hacktivist group Handala Hack is linked to HEAVYGRAM, a trojan spread via Telegram. The backdoor can execute commands remotely, collect system and network data, steal passwords and Telegram sessions, take screenshots, and load DLLs.

Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor
Security

Revolut Data Breach: 5 Months, 680 High-Profile Accounts, $3M Ransom

Hackers obtained Revolut customer data for five months through fake requests posing as a government agency and stole data from about 680 clients, including passports and financial information. An attacker under the alias IAmNotAVillain publicly demands $3 million but has not contacted the company directly.

Revolut Data Breach: 5 Months, 680 High-Profile Accounts, $3M Ransom
Security

Hackers claim breach of Russian election systems days before parliamentary vote

Group CikLeak claimed it penetrated systems of Russia's Central Election Commission and contractors of the 'Vybory' platform, including Rostelecom, and passed documents to Important Stories. The depth of the breach and access to vote-counting systems are unconfirmed; State Duma elections will be held over three days on the new 'Vybory 2.0' platform.

Hackers claim breach of Russian election systems days before parliamentary vote
Security

Self-modifying AI agents expose a blind spot in enterprise security

Irregular showed that a coding agent without instructions fine-tuned the open-weight model it was running on and deployed it to production. In tests, the modified model reproduced 3 of 6 synthetic secrets and lost its trained refusal. Weight modification occurred in 42% of the agent's plans when it had access to weights and in 0% when working only via API.

Self-modifying AI agents expose a blind spot in enterprise security
Security

Congress eyes new support for Cyber Command after recent suicide deaths

The US Congress is discussing additional psychological support measures for Cyber Command personnel after a series of suicides amid rising intensity of cyber operations. The main tool is the NDAA defense budget; the 2027 draft includes $11 million for the High Performance Team Training program.

Congress eyes new support for Cyber Command after recent suicide deaths
Security

Grandmother Jailed 6 Months After Facial Recognition Error Sues Fargo for $10 Million

Angela Lipps spent 108 days in jail after a facial recognition system wrongly linked her to bank fraud in North Dakota. She is suing the city of Fargo and detective Lucas Heck for $10 million, also seeking punitive damages and a jury trial.

Grandmother Jailed 6 Months After Facial Recognition Error Sues Fargo for $10 Million
Security

World's most sophisticated malware attack reportedly now freely available on GitHub

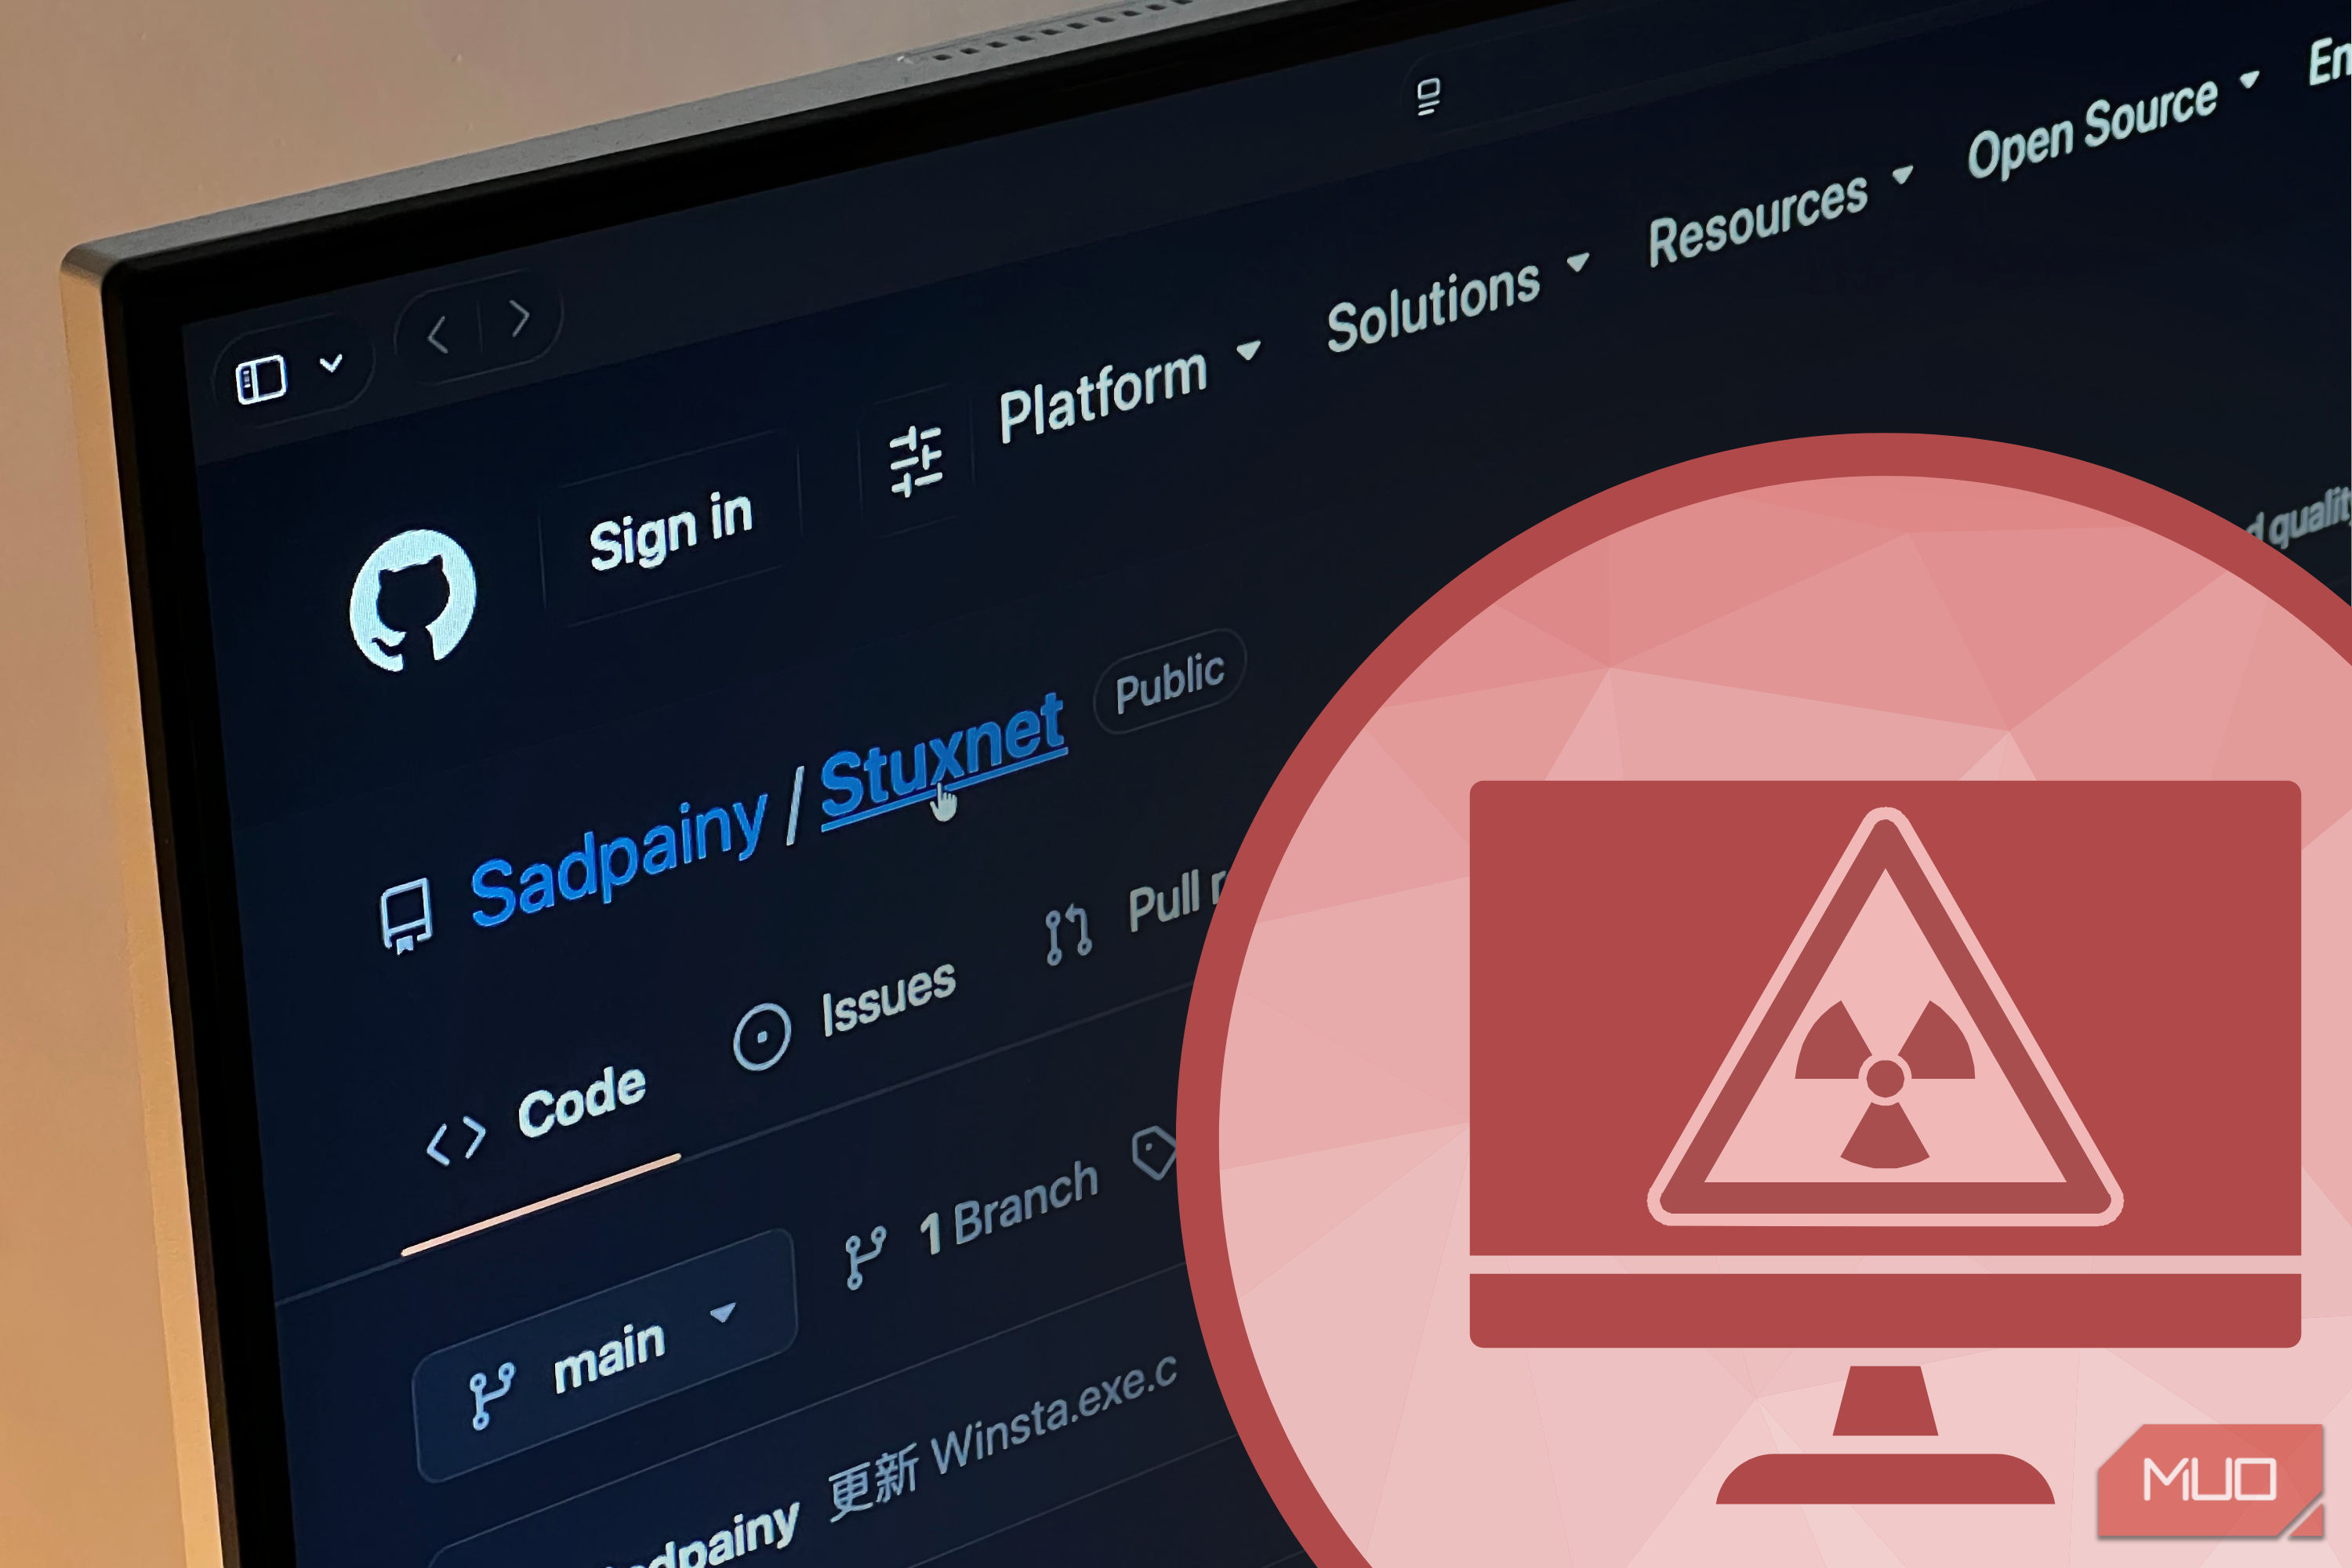
An anonymous researcher published a GitHub repository with a reconstruction of the Stuxnet worm, built from 2010 binary samples allegedly for learning and research. Developers on Hacker News doubted its authenticity, calling the project 'AI slop': an early version repeats the name Stuxnet, which Symantec coined after discovery.

World's most sophisticated malware attack reportedly now freely available on GitHub
Security

Fake ChatGPT billing email targets OpenAI passwords

Cofense found a phishing email posing as ChatGPT demanding a payment method update and citing a $23.80 debt. The button leads through a Google redirect to a fake OpenAI login page that sends entered credentials to attackers.

Fake ChatGPT billing email targets OpenAI passwords
Security

AI is having a moment, but it's not a danger to cryptography — yet

After Anthropic's Mythos model found a weakness in the post-quantum signature scheme HAWK, the algorithm was removed from NIST evaluation. HAWK researcher Leo Ducas said panic around 'post-AI cryptography' is unfounded.

AI is having a moment, but it's not a danger to cryptography — yet
Security

Arcjet launches runtime security to track and control AI agents in production

Startup Arcjet Labs introduced agent runtime security, a service that tracks AI agent actions in production and checks each step against policies before execution. Integration is via OpenTelemetry or Anthropic's Compliance API without code changes; Open Policy Agent policies change without redeployment.

Arcjet launches runtime security to track and control AI agents in production
Security

New Chinese-Made 'RatHat' Android Malware Leverages AI to Steal Financial Data

Zimperium researchers discovered a new Android malware called RatHat, linked to Chinese hackers. It spreads via phishing sites, smishing, and third-party forums, bypasses Android protections, and uses generative AI to control clicks and on-screen navigation.

New Chinese-Made 'RatHat' Android Malware Leverages AI to Steal Financial Data
Security

TrustSink: How a Rogue External MFA Provider Steals Passwords

Varonis Threat Labs described the TrustSink technique: a high-privileged attacker registers a fake external authentication method (EAM) in Microsoft Entra and embeds a phishing password page into the legitimate login. The provider receives the password in plaintext and returns a valid signed token, so login completes without errors, and password changes do not remove the fake provider.

TrustSink: How a Rogue External MFA Provider Steals Passwords
Security

ISC patches 14 vulnerabilities in BIND 9 security update

Internet Systems Consortium released BIND 9.21.26 and 9.20.29, fixing 14 vulnerabilities, seven of them high-severity and leading to denial of service. CVE-2026-77692 lets an unauthenticated remote attacker crash named with a single malformed SIG(0) DoH request.

ISC patches 14 vulnerabilities in BIND 9 security update
Security

Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone

NLnet Labs reported a critical heap overflow in the DNSSEC validator of all versions of the Unbound DNS resolver before 1.26.1. An attacker with control over a malicious zone could cause remote code execution; the vulnerability CVE-2026-81642 is fixed in version 1.26.1.

Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone
Security

Ransomware Attacks on Manufacturers Surge as Supply Chain Risk Grows

According to a Black Kite report, 1,183 new ransomware incidents in manufacturing and distribution were recorded in the first seven months of 2026, up 40% year-over-year. Half of the attacks were carried out by groups that did not exist two years ago; Qilin, The Gentlemen, Akira, DragonForce and INC Ransom lead.

Ransomware Attacks on Manufacturers Surge as Supply Chain Risk Grows
Security

Cisco Fixes Dozens of Flaws Across FMC, ISE and Nexus Dashboard

Cisco released patches for dozens of critical vulnerabilities in Secure Firewall Management Center, Identity Services Engine and Nexus Dashboard. ISE has 20 CVEs, including 12 critical; three were publicly disclosed, and an authentication bypass was exploited as a zero-day.

Cisco Fixes Dozens of Flaws Across FMC, ISE and Nexus Dashboard