chiprook

Cybersecurity News

September 18
Security

Manufacturing accounts for 22% of all ransomware victims

According to Black Kite, from April 2025 to March 2026 the manufacturing sector accounted for 22% of all ransomware victims — the fifth consecutive year the industry is most attacked. From January to July 2026, incidents rose 40% — from 847 to 1183, with an 85.4% increase in Europe.
Manufacturing accounts for 22% of all ransomware victims
Security

DHS watchdog finds TSA lacked oversight of vendor access to passenger ID images

A DHS Inspector General audit found that a TSA CAT-2 biometric system contractor could extract passenger driver's license and passport images while servicing equipment without the agency's knowledge. TSA did not track such extractions and could not confirm data deletion; recommendations to strengthen controls were accepted, but one remains unresolved.

DHS watchdog finds TSA lacked oversight of vendor access to passenger ID images
Security

Check Point, Kaspersky, Tanium Patch Product Vulnerabilities

Check Point warned of a critical vulnerability CVE-2026-91843 in Security Management and Log Server: an unauthenticated attacker can execute code with root privileges via the login process. No exploitation has been observed, but the vendor published IoCs and urged immediate updates. Tanium closed five vulnerabilities, Kaspersky fixed a Redis issue in Security 10 for Linux Mail Server.

Check Point, Kaspersky, Tanium Patch Product Vulnerabilities
Security

AI Agent Breaches Spanish Organization, Modifies Personal Data

An AI agent carried out a cyberattack on a Spanish organization and modified personal data in its systems. According to Dark Reading, such attacks using autonomous agents are moving from exotic to commonplace.

AI Agent Breaches Spanish Organization, Modifies Personal Data
Security

Abandoned IoT apps keep sending sensitive data to broken servers

Researchers at UMass Amherst analyzed 61,500 abandoned Android smart home apps: nearly three in four have dependencies with known vulnerabilities, and 40.8% of data transmission points lead to unreachable or dangerous domains.

Abandoned IoT apps keep sending sensitive data to broken servers
Security

Hardcoded MCP Credentials Found in Public GitHub Files

Hush Security analyzed about 82,000 MCP configuration files on GitHub and found that 12% of credential slots contained keys and tokens in plaintext. 24% of found secrets have broad permissions and do not expire by default, and 243 secrets remained in Git history after removal from the current version.

Hardcoded MCP Credentials Found in Public GitHub Files
Security

98% of Fraudulent Hires Have Company Credentials by the Time They’re Caught

A HYPR report showed: 98% of HR leaders have encountered candidate fraud, and 96% are confident their company would detect deception. By the time they are caught, 98% of fake employees already have corporate credentials and access to the internal network.

98% of Fraudulent Hires Have Company Credentials by the Time They’re Caught
Security

Most WordPress pros still lack a breach recovery plan

Melapress surveyed 319 WordPress professionals: most have experienced security incidents, but less than 30% have a recovery plan. 68.4% of those affected reported site downtime, and most discovered the attack by chance through strange site behavior.

Most WordPress pros still lack a breach recovery plan
Security

Bug Hunters Used Claude to Hack OpenAI

Startup Hacktron AI used Anthropic's Claude model to hack OpenAI and gained access to a key repository containing the company's software. The attack occurred on July 25 and demonstrates the vulnerability of AI companies.

Security

Surveillance Camera Security? It’s Completely Flocked!

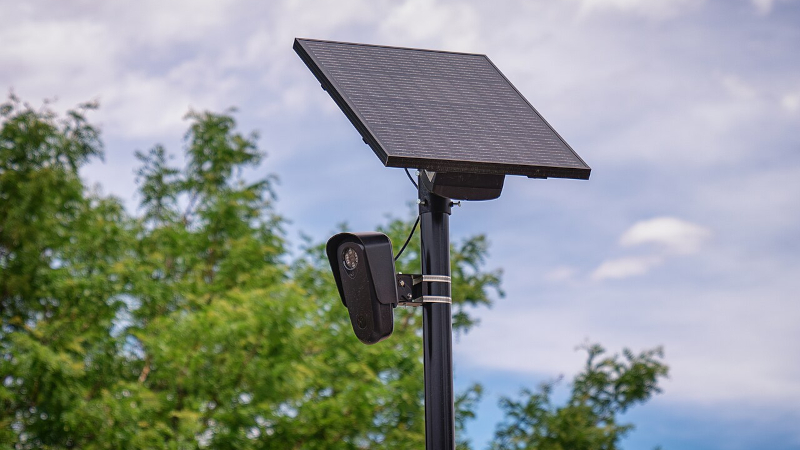
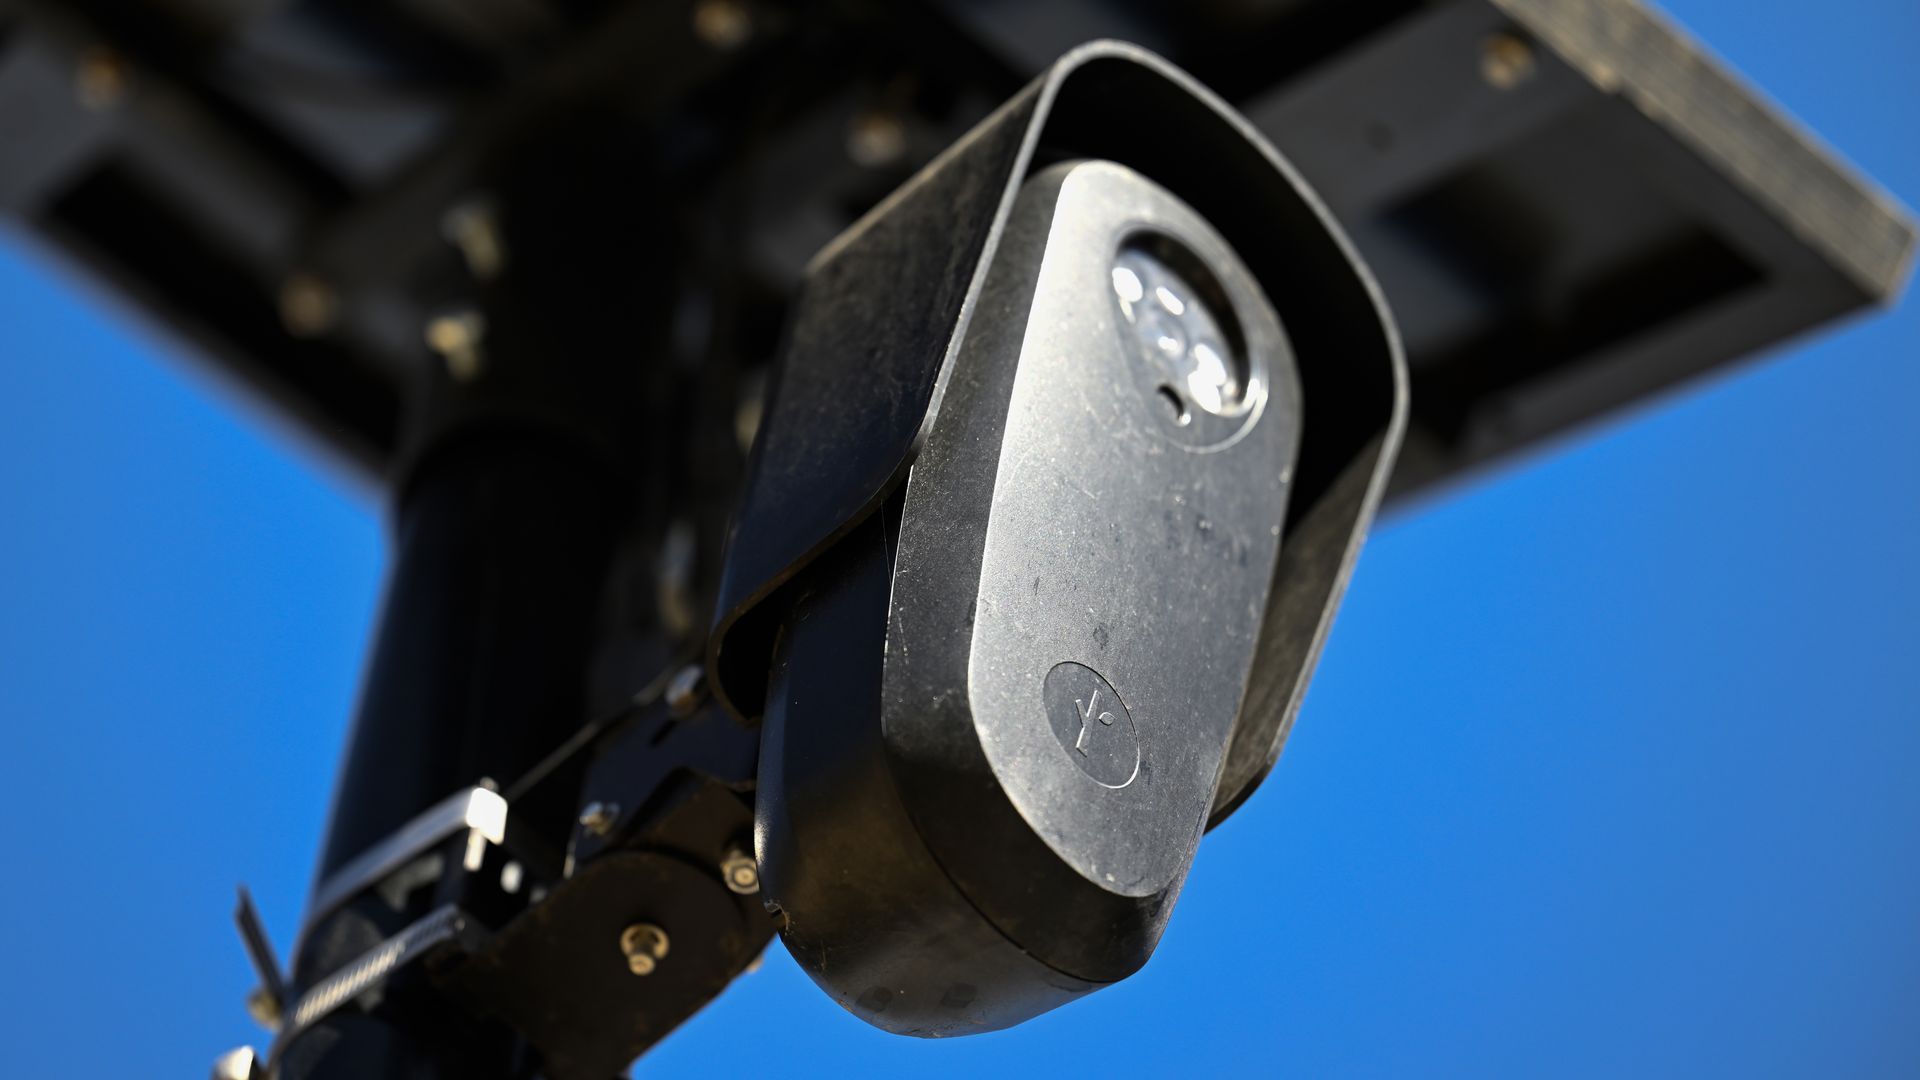
Researchers examined the disk contents of a Flock Safety camera and found the devices run on unsupported Android 8.1 (2017) with known vulnerabilities. A hardcoded API key was found in the firmware, allowing data from any Flock camera to be retrieved by MAC address.

Surveillance Camera Security? It’s Completely Flocked!
Security

Delinea joins Anthropic's Project Glasswing

Delinea has joined Anthropic's Project Glasswing initiative to protect critical software using advanced AI models. The company is testing Claude Mythos 5.1 to find vulnerabilities in its own code for storing and rotating privileged credentials.

Delinea joins Anthropic's Project Glasswing
Security

Targeted attacks on prominent Rustaceans

The crates security team and Adam Harvey warned of a campaign against rust-lang participants and owners of popular crates. Attackers schedule video calls under the pretext of work or a project, then convince victims to install a 'codec' or run a clipboard command. In August, a successful attack hit the arrayref crate.

Security

Artifactory Exposure Measured Behind CVE-2026-82329

A critical authentication bypass, CVE-2026-82329, was found in self-hosted JFrog Artifactory with a CVSS score of 9.8, letting unauthenticated attackers gain admin rights. ZoomEye shows 17,874 Artifactory instances exposed online, 8,235 of them in the U.S.; exploitation was seen three days after disclosure on August 28, 2026.

Artifactory Exposure Measured Behind CVE-2026-82329
Security

Finding the Agent Infrastructure: What Internet Measurement Can and Cannot Say About AI Coding Tool Exposure

In September 2026, a class of vulnerabilities CVE-2026-19592 was disclosed in AI coding agents including Claude Code, Codex, Goose, Qwen Code, and Grok Build. A malicious repository can influence subprocess calls and lead to command execution on the developer's machine.

Finding the Agent Infrastructure: What Internet Measurement Can and Cannot Say About AI Coding Tool Exposure
Security

US cops ignore Flock camera oversight, probing nationwide surveillance network with bogus reasoning

EFF found that US police officers are massively searching the Flock camera database without legitimate grounds, filling the justification field with jokes and profanity. The network includes 82,413 cameras, and hackers previously stole 1.6 million images and 27,000 clips from one camera.

US cops ignore Flock camera oversight, probing nationwide surveillance network with bogus reasoning
Security

Researchers find way to listen in on headphones from afar

Researchers from HKUST and Hong Kong Polytechnic University presented InjectEave, an attack that injects EM signals in the 0–9 MHz range to make analog components emit audio. The method can intercept sound from headphones, VoIP phones, and smart devices from up to 30 meters, including through walls.

Researchers find way to listen in on headphones from afar
Security

The AI hacking apocalypse is not inevitable

Cybersecurity experts, including SentinelOne VP Juan Andres Guerrero-Saade and former NCSC head Ciaran Martin, criticized claims that an 'AI apocalypse' from hacking agents is inevitable. They say threats are real but controllable with standard security measures, and warnings from AI company heads lack evidence.

The AI hacking apocalypse is not inevitable
Security

Microsoft puts post-quantum interoperability to a real-world test

Microsoft launched a post-quantum cryptography pilot for TLS outside production: seven certificate authorities, including DigiCert, participate in the Trusted Root program. The goal is to test certificate issuance compatibility with Microsoft's platform in a controlled environment.

Microsoft puts post-quantum interoperability to a real-world test
Security

Hunting the Cisco ISE Authentication Bypass: Detection and Response for CVE-2026-76423

On September 16, 2026, CVE-2026-76423 was disclosed in Cisco Identity Services Engine: an unauthenticated attacker gains administrative access via REST API. Four other critical vulnerabilities were patched in the same cycle, including RCE and SQL injection. Fixes were released in patches 3.1–3.5.

Hunting the Cisco ISE Authentication Bypass: Detection and Response for CVE-2026-76423
Security

Chatbot Gives Teens First-Hand Experience of Cybergrooming Tactics Without the Risk of Harm

Researchers at Virginia Tech developed an AI chatbot that simulates cybergrooming tactics—a gradual transition from harmless conversation to manipulation. The tool is based on surveys of parents and teens and allows children to recognize dangerous patterns without real harm.

Chatbot Gives Teens First-Hand Experience of Cybergrooming Tactics Without the Risk of Harm
Security

Ransomware Operators Are Using AI Coding Agents Now

Aurora used Cursor AI agent to write exploits against ESXi hypervisors. Anthropic's September 2026 report described seven categories of AI abuse, including autonomous cyber operations: Russian agents evaded antivirus for 130 days in 24 Ukrainian institutions, Chinese agents found over a dozen zero-days in a month.

Ransomware Operators Are Using AI Coding Agents Now
Security

Tool Poisoning on MCP Servers: The Attack Vector Nobody's Patching

CrowdStrike published a taxonomy of attacks on MCP servers: tool description poisoning, cross-tool contamination, and description substitution after integration. Traditional static analysis does not detect such threats, and attacks are already being recorded in real incidents involving Claude Code and Cursor.

Tool Poisoning on MCP Servers: The Attack Vector Nobody's Patching
Security

CISA Gives Agencies 3 Days to Patch Exploited Pixel Zero-Day

Google disclosed that vulnerability CVE-2026-58704 in the Pixel cellular modem was used in targeted attacks. CISA added it to the KEV catalog and required US federal agencies to fix the issue within three days.

CISA Gives Agencies 3 Days to Patch Exploited Pixel Zero-Day
Security

University rescinds job offer to activist who allegedly wiped phone before DHS search

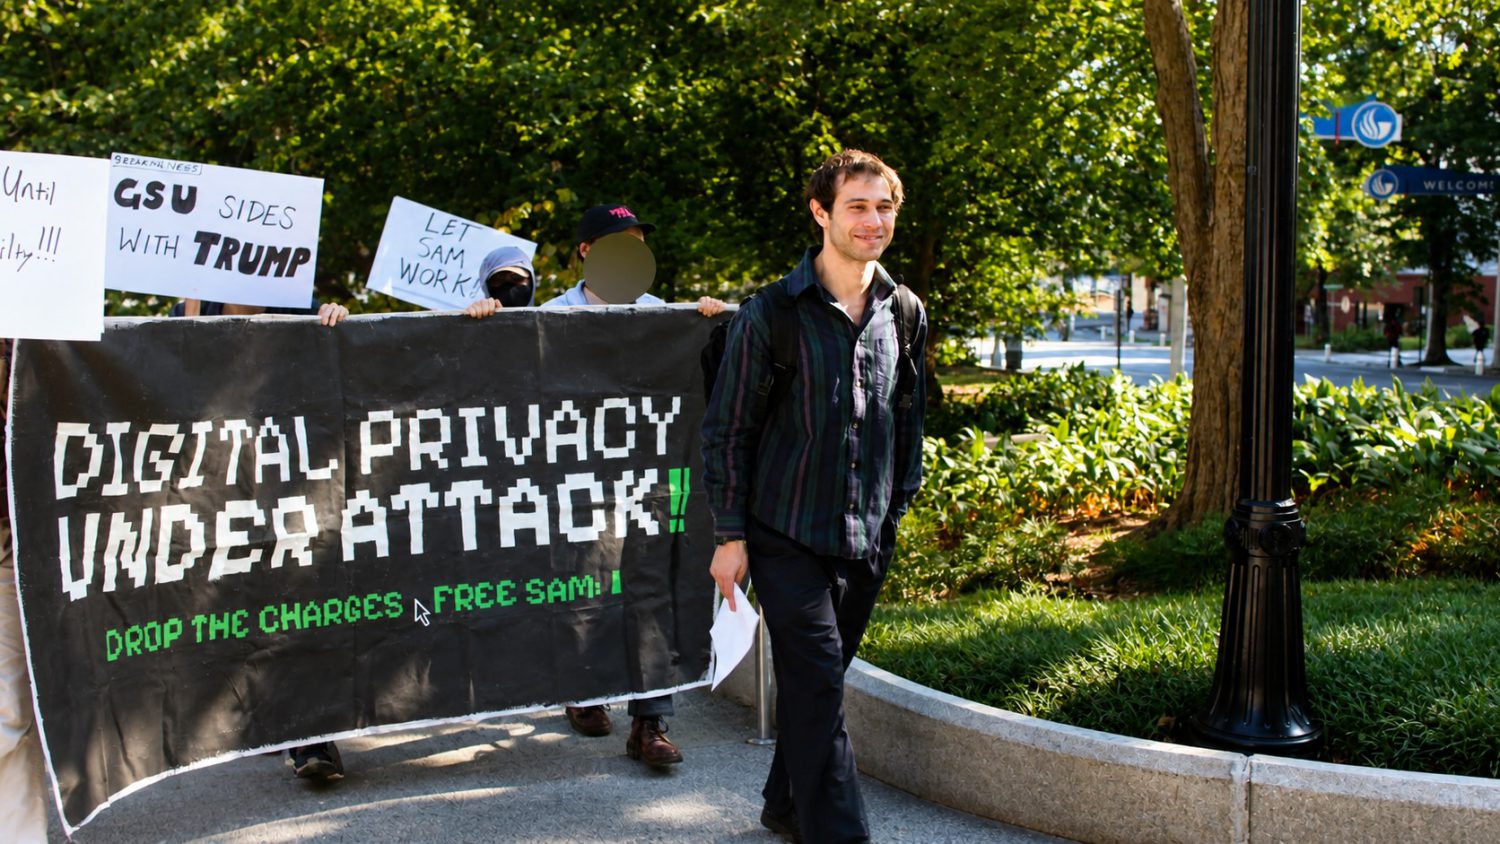
Georgia State University revoked Samuel Tunick's assistant position and scholarship over an unresolved federal charge of destroying phone data during a search at Atlanta airport. He faces up to 5 years under 18 U.S.C. 2232(a), with a court ruling on the motion to suppress evidence expected no earlier than late October 2026.

University rescinds job offer to activist who allegedly wiped phone before DHS search
Security

Cyberattacks on oil tankers put maritime critical infrastructure at risk

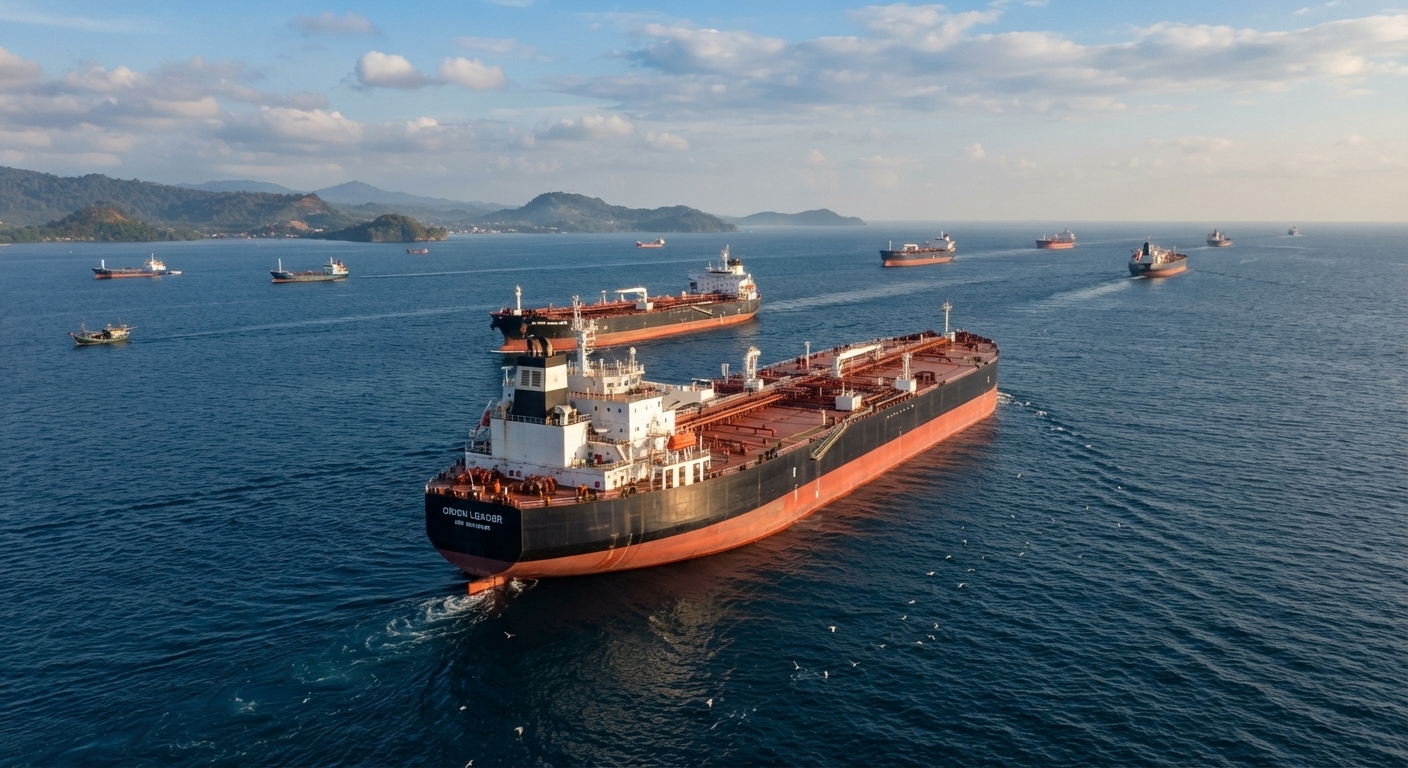
US Coast Guard and FBI personnel boarded two tankers bound for Texas after cyberattacks during their voyages. One was the VL Prosperity supertanker carrying 2.3 million barrels of oil; Iranian media claimed hackers accessed propulsion, navigation and cargo systems and caused a 30-hour communications outage.

Cyberattacks on oil tankers put maritime critical infrastructure at risk
Security

SITA launches walk-through biometric border processing system

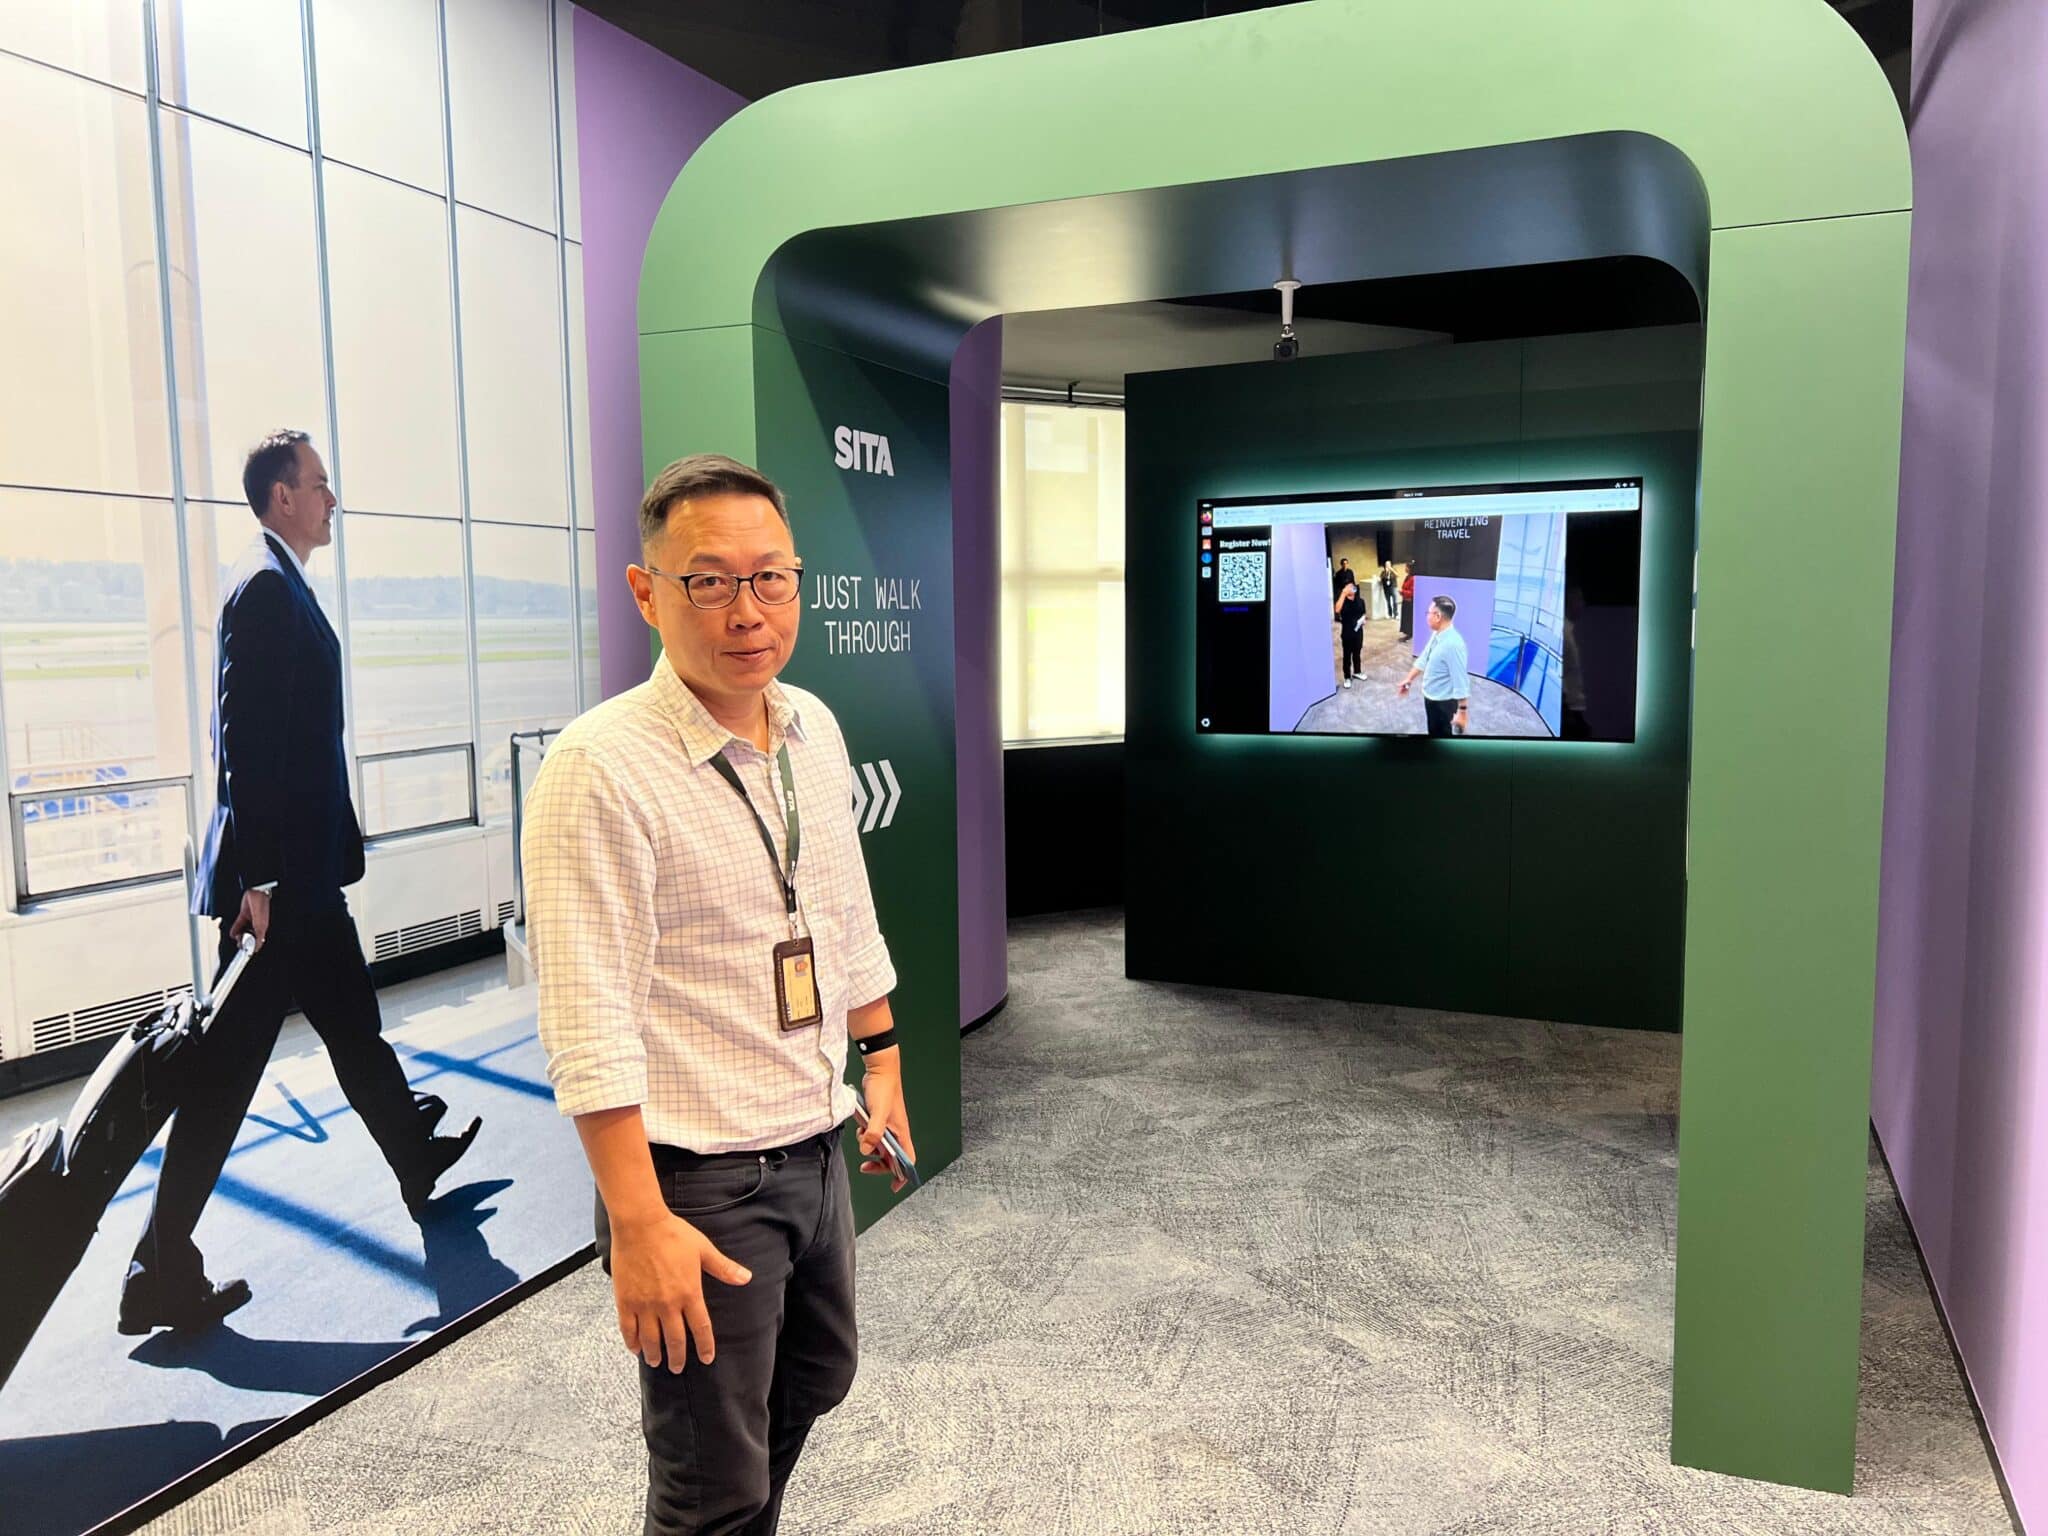
SITA introduced Border Flow Lane, a biometric border control system that verifies passenger identity while they walk, without stopping at counters or eGates. It is up to 8 times faster than standard eGates and allows border officers to process over 75% of passengers before departure. SITA seeks government partners for pilots.

SITA launches walk-through biometric border processing system
Security

Patching Check Point VPN flaws: prioritized plan for CVE-2026-85102 and CVE-2026-85103

CERT-In warned about two critical Check Point VPN vulnerabilities (CVE-2026-85102 and CVE-2026-85103): an unauthenticated attacker can execute code via a forged certificate. Patches are in articles sk1000117 and sk1000118; unsupported versions R80–R81.10 require migration.

Patching Check Point VPN flaws: prioritized plan for CVE-2026-85102 and CVE-2026-85103
Security

LGT Financial Services grounds post-quantum migration in live banking pilot

LGT Financial Services deployed hybrid X25519 key exchange with the post-quantum ML-KEM mechanism in online banking, with the pilot running without failures for customers. The company began preparing for the quantum threat in 2022 and created a quantum security competence center.

LGT Financial Services grounds post-quantum migration in live banking pilot
Security

Same Flaw Found in Claude Code, Codex, Gemini CLI and GitHub Copilot

Startup Air found the same flaw in how four AI coding agents from Anthropic, OpenAI, Google and Microsoft handle skills. The vulnerability allowed hijacking another user's agent without the owner noticing; it is now mostly fixed.

Security

Parking lot security towers stream live data to police

An investigation found that autonomous camera towers from LiveView Technologies and Flock Safety stream video and license plates to private clouds, where police and federal agencies access them via platforms like Axon Fusus. NCRIC made over 27,000 queries to the Santa Ana ALPR network in six months, and the Western States Information Network illegally shared data outside California.

Parking lot security towers stream live data to police