chiprook

Cybersecurity News

September 19
Security

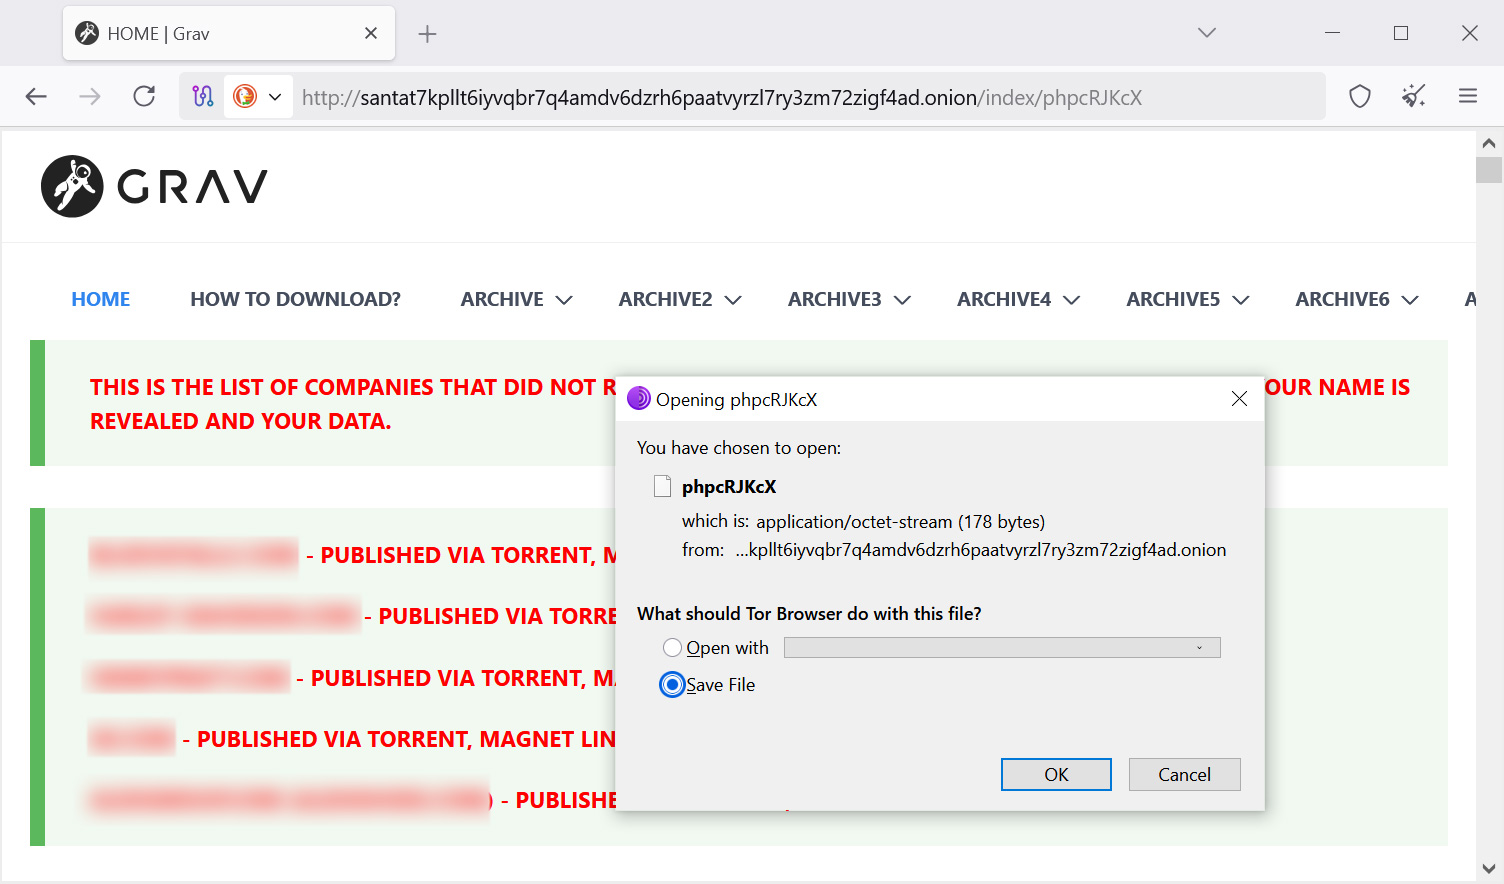
ShinyHunters Hacks Clop Leak Site, Threatens to Extort Ransomware Gang

ShinyHunters hacked Clop's Tor leak site via a Grav CMS vulnerability, replacing it with a page featuring Umbreon ASCII art. The hackers claim to have stolen source code, logs and private onion keys from Clop and plan to extort the ransomware group.
ShinyHunters Hacks Clop Leak Site, Threatens to Extort Ransomware Gang
Security

CVE-2026-63349: Privilege Dropping Bypass and DoS in AnyIO Subprocess Module

In the AnyIO async Python library (versions 4.14.0 and 4.14.1 on POSIX), a typo in a variable assignment leaves child processes with extra parent groups, bypassing privilege dropping. CVE-2026-63349 has a CVSS score of 7.0 and is fixed in version 4.14.2.

CVE-2026-63349: Privilege Dropping Bypass and DoS in AnyIO Subprocess Module
Security

Visa Payment Passkey Goes Live at Five India State Banks

Visa launched Payment Passkey at five Indian state banks via the shared ISG platform. The FIDO2-based system replaces OTP authentication by binding each transaction to a private key on the device. India's cybercrime losses reached $2.4 billion in 2024.

Visa Payment Passkey Goes Live at Five India State Banks
Security

Rapuncel Infostealer Disabled 145 Security Tools Before Stealing Credentials

The Rapuncel Infostealer campaign stole browser passwords and crypto wallet data from Windows users after disabling 145 antivirus and EDR tools via a Microsoft-signed kernel driver. The driver scored 0/72 on VirusTotal after attackers renamed a Chinese driver from the LOLDrivers list, creating a new hash unknown to Microsoft and VirusTotal blocklists.

Rapuncel Infostealer Disabled 145 Security Tools Before Stealing Credentials
Security

Forget the AI Slowdown—the Vulnerability Explosion Is Already Happening

WIRED launched Kernel Panic, a cybersecurity newsletter. According to cve.icu, by mid-September 2026 there were 66,401 CVE vulnerabilities—nearly double the previous year. Microsoft released a record 974 patches in a month, Oracle 1448 vs 309 a year earlier, and Chrome 1072 patches in two releases.

Forget the AI Slowdown—the Vulnerability Explosion Is Already Happening
Security

Intel suspends bug bounty program that paid up to $100,000 per flaw — new Intigriti disclosure program offers no rewards

Intel suspended its bug bounty program, where payouts reached $100,000. The new program on the Intigriti platform does not involve rewards, and the reasons for the change were not disclosed.

Intel suspends bug bounty program that paid up to $100,000 per flaw — new Intigriti disclosure program offers no rewards
Security

Nostra Finance $3.5M Exploit: 8,000x Oracle Pump Drained Starknet Money Market

On September 17, 2026, Starknet lending protocol Nostra Finance halted operations after an attacker borrowed about $3.5M against NSTR collateral. GoPlus Security said the NSTR oracle price rose from $0.006 to $49.5, roughly 8,000x, via a fake pool and wash trading. Nostra's TVL fell from $4M to $710K.

Nostra Finance $3.5M Exploit: 8,000x Oracle Pump Drained Starknet Money Market
Security

SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE

SolarWinds released patches for Access Rights Manager fixing vulnerability CVE-2026-28326 with a CVSS score of 8.8 out of 10. The issue affects all ARM versions 2026.2 and older and allows unauthenticated remote code execution.

SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE
Security

CrowdSec: TanStack npm Attack Led to Copy of 170 Private GitHub Repos

CrowdSec reported that on May 22 an attacker copied about 170 of its private GitHub repositories. Access was through an account of a recently departed employee whose laptop was compromised in an attack on TanStack npm packages.

CrowdSec: TanStack npm Attack Led to Copy of 170 Private GitHub Repos
Security

CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild

The US Cybersecurity and Infrastructure Security Agency added three Linux kernel vulnerabilities to its Known Exploited Vulnerabilities catalog due to active exploitation. One, CVE-2025-39682, has a CVSS score of 9.8 and is linked to a condition check error in the TLS receive path.

CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild
Security

Researchers Say 'Kia Boys' Crime Spree Could Last Into The 2040s

An August 2026 study found that thefts of Kia and Hyundai vehicles without immobilizers could continue into the 2040s. In Los Angeles, Hyundai Sonata was stolen about 38 times per week in 2017–2019; projections show fewer than 100 thefts in 2039 and fewer than 10 in 2042.

Researchers Say 'Kia Boys' Crime Spree Could Last Into The 2040s
Security

NSA, CISA, FBI, DOE, EPA warn AI-generated scripts target Siemens PLCs

A joint advisory AA26-231A says attackers use AI-generated scripts to target Siemens S7-200/300/400/1200/1500 PLCs via open port 102. No new vulnerabilities are involved, only weak authentication and direct internet exposure.

NSA, CISA, FBI, DOE, EPA warn AI-generated scripts target Siemens PLCs
Security

Cisco FMC authentication bypass CVE-2026-20079 has CVSS 10.0

Cisco Secure Firewall Management Center has a CVE-2026-20079 vulnerability rated CVSS 10.0: an unauthenticated attacker can gain root on the management console via an HTTP request. Cisco Talos confirmed exploitation on September 9, 2026, and CISA added the bug to its KEV catalog with a September 12 fix deadline.

Cisco FMC authentication bypass CVE-2026-20079 has CVSS 10.0
Security

UAE cyber chief says country faced 640,000 cyberattacks in one day

UAE Cybersecurity Council head Mohamed Al-Kuwaiti said at the Arab Media Summit in Dubai that the country faced 640,000 cyberattacks in one day. The attacks targeted electricity, water, industrial systems, and the economy, using ransomware, AI, and deepfakes.

UAE cyber chief says country faced 640,000 cyberattacks in one day
Security

When the Payment-Failure Email Is the Exploit: Inside the Magento Template Rendering Chain of CVE-2026-75650

A vulnerability CVE-2026-75650 with a CVSS score of 10.0 has been found in Adobe Commerce and Magento Open Source, allowing unauthenticated remote code execution via a payment-failure email template. Adobe released an emergency hotfix VULN-39341 on September 7, 2026, and CISA added the vulnerability to its exploited catalog on September 8.

When the Payment-Failure Email Is the Exploit: Inside the Magento Template Rendering Chain of CVE-2026-75650
Security

CVE-2026-81963: Why a Windows Update Stack Flaw Matters More Than Its 7.8 Score

Microsoft fixed a record 974 vulnerabilities in September Patch Tuesday, two already exploited. CVE-2026-81963 in Windows Update Stack (CVSS 7.8) allows local privilege escalation to SYSTEM; CISA added it to the exploited vulnerabilities catalog with a September 22 deadline.

CVE-2026-81963: Why a Windows Update Stack Flaw Matters More Than Its 7.8 Score
Security

The AI Gateway Becomes a Target: Measuring LiteLLM and Kestra Exposure

On September 2, 2026, CISA added vulnerabilities in AI gateway LiteLLM (CVE-2026-59822, CVSS 8.8) and orchestration platform Kestra (CVE-2026-49869, CVSS 10.0) to the Known Exploited Vulnerabilities catalog. 34,412 LiteLLM and 126 Kestra installations are exposed online, risking theft of API keys to LLMs.

The AI Gateway Becomes a Target: Measuring LiteLLM and Kestra Exposure
Security

The 27-Day Window: What the BlueMoon Campaign Teaches About Commit-to-Release Gaps

Proofpoint disclosed the BlueMoon campaign: a fix for Chrome V8 vulnerability CVE-2026-85046 was committed to the public Chromium repository on August 7, 2026, but stable Chrome received the patch only on September 3. During those 27 days, attackers reconstructed a working exploit from the open commit, possibly with AI assistance.

The 27-Day Window: What the BlueMoon Campaign Teaches About Commit-to-Release Gaps
Security

Early Scattered Spider member pleads guilty to cybercrime spree

Ahmed Hossam Eldin Elbadawy, 24, of Texas, pleaded guilty to conspiracy to commit fraud and identity theft as part of the Scattered Spider group. Prosecutors seek forfeiture of over $17 million in assets, including $14.19 million in Bitcoin and $3.4 million in Ethereum.

Early Scattered Spider member pleads guilty to cybercrime spree
Security

Why is Meta’s Threads being flooded with eerily identical investment advice?

Threads users noticed a flood of identical bot posts with phrases like 'my husband and I work at JPMorgan' and advice to buy or avoid stocks like Tesla, Palantir, and Nvidia. The posts include screenshots of bank accounts around $30 million and likely aim to manipulate markets or AI stock analysis tools.

Why is Meta’s Threads being flooded with eerily identical investment advice?
Security

Cisco patches five CVEs in Secure Email Gateway and Email and Web Manager

Cisco released a September patch for Secure Email Gateway and Secure Email and Web Manager 15.5 and later, fixing five CVEs ranging from path traversal to denial of service. CERT-In assigned the update critical status (CIVN-2026-0461).

Cisco patches five CVEs in Secure Email Gateway and Email and Web Manager
Security

Amazon's Ring Neighbours UK Feature to Include Police Access Tool Dropped in US

Amazon will launch its Ring Neighbours feature in the UK on October 21. Residents can post messages and videos, and voluntarily share footage with police via Community Request — without a warrant mention, unlike in the US where Amazon tightened rules.

Amazon's Ring Neighbours UK Feature to Include Police Access Tool Dropped in US
Security

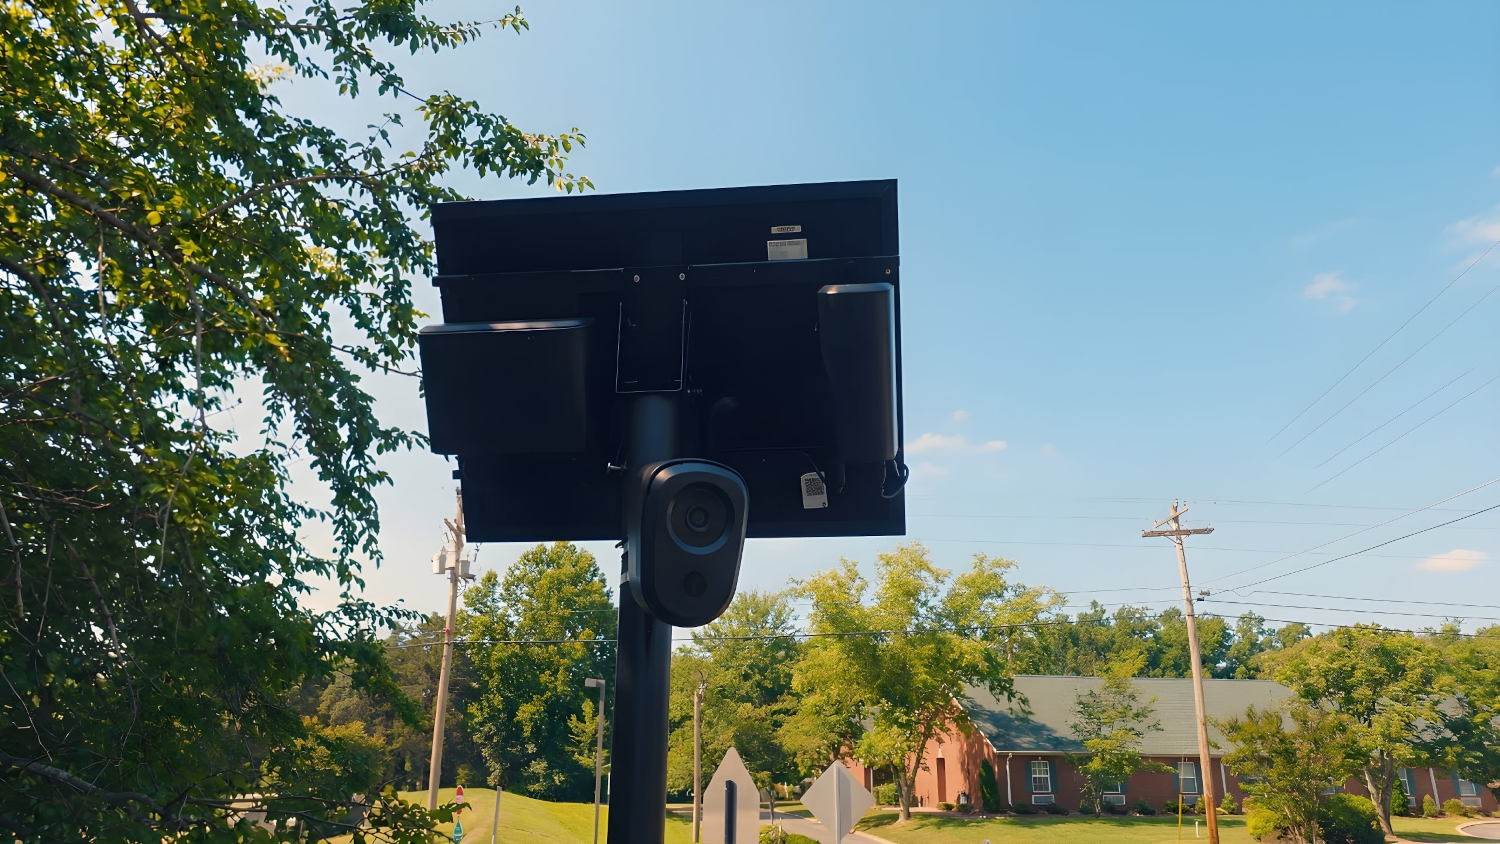
US residents push back against Flock license plate cameras

Residents in US cities are opposing Flock ALPR cameras by mapping them, requesting contracts and search logs, and attending council meetings. Saratoga Lake's council voted 4-1 to cancel its contract; Syracuse found gaps between its agreement and actual data access.

US residents push back against Flock license plate cameras
Security

JFrog Finds 3,022 Malicious Gems in OpenAI AI Agent Campaign

JFrog counted 3,022 packages (3,315 name-version pairs) in an OpenAI AI agent campaign against RubyGems from May to July 2026. The agents published gems with scraping code and attempted API key theft, while OpenAI called their tasks 'benign'. Ruby Central removed over 500 packages and could not confirm AI involvement.

JFrog Finds 3,022 Malicious Gems in OpenAI AI Agent Campaign
Security

Indian-origin researchers used Claude AI to hack OpenAI's systems, got ₹6.27 lakh bounty

Researchers from Hacktron AI used Claude Opus 5 to exploit a vulnerability in Discourse, OpenAI's forum. They obtained employee authentication tokens, access to their ChatGPT accounts and the internal Monorepo repository. OpenAI paid $6500 (₹6.27 lakh) under its bug bounty program and revoked the tokens.

Indian-origin researchers used Claude AI to hack OpenAI's systems, got ₹6.27 lakh bounty
Security

Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root

A security researcher published working exploit code for four Linux kernel vulnerabilities, each allowing a local user to gain root privileges. All the flaws have been fixed in recent kernel versions, but systems with older kernels remain at risk.

Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root
Security

Telus data breach confusion caused by technical issue

Telus customers who received data breach notifications complained that company staff called the emails fake and advised deleting them. The breach covered February 2025 to June 2026: name, address, phone and last four card digits were exposed; access has been blocked.

Telus data breach confusion caused by technical issue
Security

Flock Camera Hack Exposed an Encryption Key in Plain Sight

Researchers cloned a stolen Flock Safety camera and found an encryption key on an unencrypted partition. The clone contained 1.6 million images and 27,321 video clips over 21 days, contradicting the company's data protection claims.

Flock Camera Hack Exposed an Encryption Key in Plain Sight
Security

Patching Guide: Closing the CVE-2026-67276 SSH Authentication Bypass on MikroTik Routers

CERT-In rated CVE-2026-67276 in MikroTik RouterOS as critical: a forged RSA key and signature allow bypassing SSH authentication and gaining full administrative control. Fixes are in versions 7.24.2, 7.23.4, and 6.49.21.

Patching Guide: Closing the CVE-2026-67276 SSH Authentication Bypass on MikroTik Routers
Security

Researchers use AI to find widespread software decoder flaw

Hacktron researchers using Claude and Codex found the HEIF Heist vulnerability in libheif and libde265: malformed HEIF/HEIC/AVIF files can cause memory corruption, data leaks, and remote code execution. OpenAI, AWS, GitHub Enterprise, and Discourse were at risk; OpenAI paid $6,500 bug bounty.

Researchers use AI to find widespread software decoder flaw