chiprook

Cybersecurity News

September 19
Security

Flock Camera Hack Exposed an Encryption Key in Plain Sight

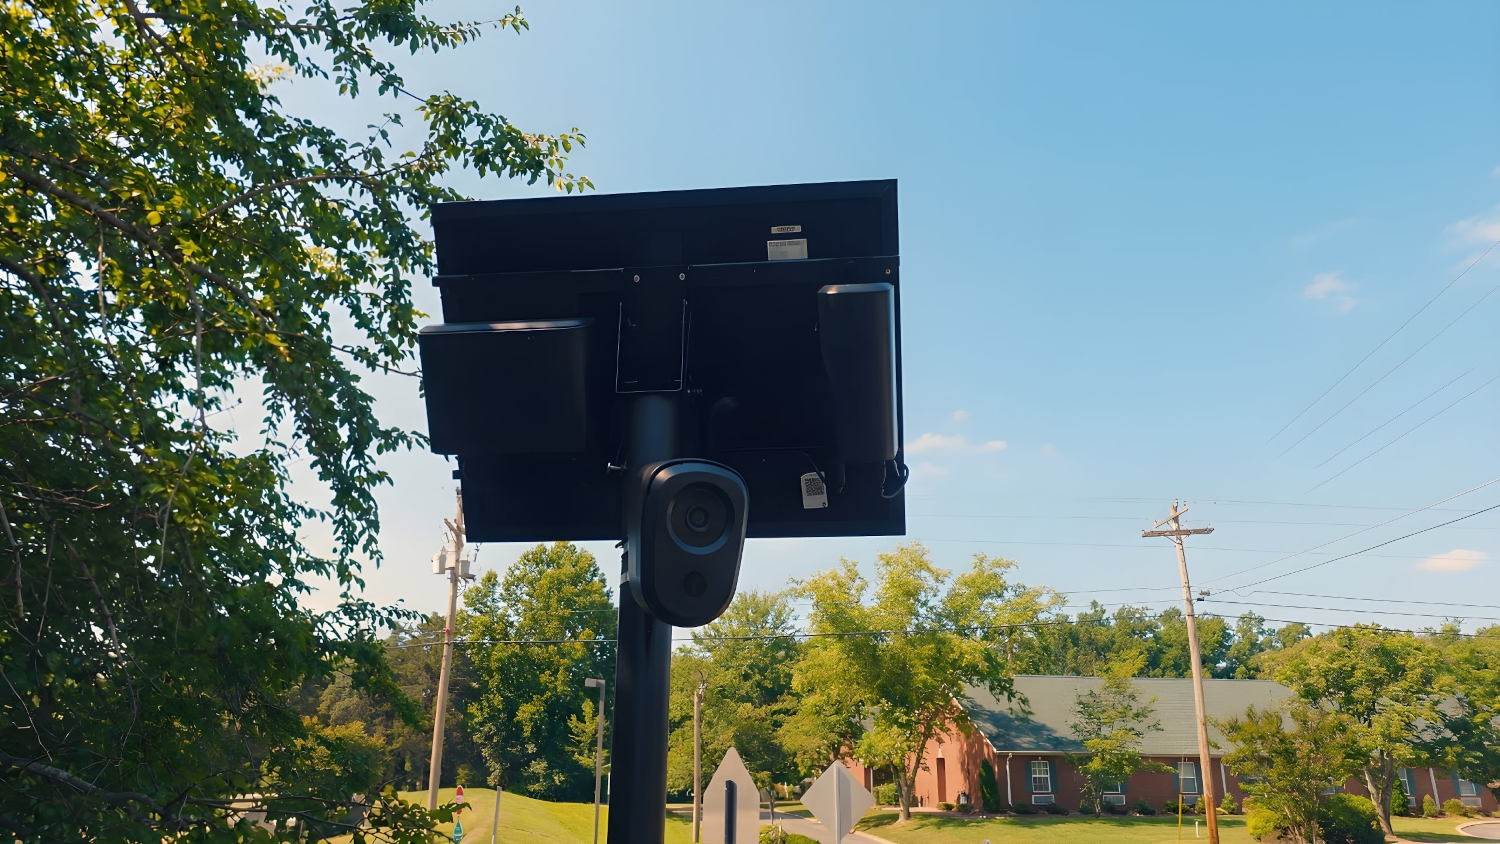
Researchers cloned a stolen Flock Safety camera and found an encryption key on an unencrypted partition. The clone contained 1.6 million images and 27,321 video clips over 21 days, contradicting the company's data protection claims.
Flock Camera Hack Exposed an Encryption Key in Plain Sight
Security

Patching Guide: Closing the CVE-2026-67276 SSH Authentication Bypass on MikroTik Routers

CERT-In rated CVE-2026-67276 in MikroTik RouterOS as critical: a forged RSA key and signature allow bypassing SSH authentication and gaining full administrative control. Fixes are in versions 7.24.2, 7.23.4, and 6.49.21.

Patching Guide: Closing the CVE-2026-67276 SSH Authentication Bypass on MikroTik Routers
Security

Researchers use AI to find widespread software decoder flaw

Hacktron researchers using Claude and Codex found the HEIF Heist vulnerability in libheif and libde265: malformed HEIF/HEIC/AVIF files can cause memory corruption, data leaks, and remote code execution. OpenAI, AWS, GitHub Enterprise, and Discourse were at risk; OpenAI paid $6,500 bug bounty.

Researchers use AI to find widespread software decoder flaw
Security

UK police data vulnerable to compromise by US government and foreign actors

A Guardian investigation found sensitive data from over 40 UK police forces is stored in Microsoft Azure, which a 2017 official security assessment deemed vulnerable to compromise by foreign actors and the US government. Some files exceed the official level, and Microsoft admitted it cannot guarantee data sovereignty.

UK police data vulnerable to compromise by US government and foreign actors
September 18
Security

New WordPress Click2Shell flaw forces theme installs, can chain to code execution

WordPress released patches for a new set of core vulnerabilities. The Click2Shell chain allows installing a theme from the official WordPress.org directory without clicking the Install button, requiring only that an administrator opens a specially crafted link. The vulnerability can lead to arbitrary code execution.

New WordPress Click2Shell flaw forces theme installs, can chain to code execution
Security

North Korea's fake job interviews infected 30,000 devices

An international warning says North Korean group WaterPlum posed as recruiters and sent fake coding tests, infecting over 30,000 devices and stealing more than $10.71 million. Over 7,000 crypto wallets were affected, with funds going to finance North Korea.

North Korea's fake job interviews infected 30,000 devices
Security

Google threat intelligence group details how one of its researchers infiltrated hacker group TeamPCP and helped disrupt its software supply chain hacking spree (Andy Greenberg/Wired)

Google's cyber threat intelligence group detailed how one of its employees infiltrated the hacker group TeamPCP and helped stop a series of software supply chain attacks that affected thousands of companies.

Google threat intelligence group details how one of its researchers infiltrated hacker group TeamPCP and helped disrupt its software supply chain hacking spree (Andy Greenberg/Wired)
Security

iProov's experimental HAPS protocol aims to close governance gaps for AI agents

iProov published an experimental HAPS (Human Approval and Presence Specification) to bind human presence and approval to machine-readable AI agent actions. The protocol on GitHub under Apache-2.0 includes a partial Rust implementation and test vectors; the approach is risk-based and independent of the presence verification method.

iProov's experimental HAPS protocol aims to close governance gaps for AI agents
Security

FBI: Fake Cop and Government Impersonation Scams Cost Victims $1.6B

From January 2025 to July 2026, IC3 received about 61,000 complaints about scammers impersonating police and government officials, with average losses over $26,000 per complaint. The most profitable variant involved video calls with fake uniforms and government backdrops: 1,809 complaints and over $140 million in losses.

FBI: Fake Cop and Government Impersonation Scams Cost Victims $1.6B
Security

AI Car Dealer Scams Are Infesting Facebook Marketplace—and They’re Working

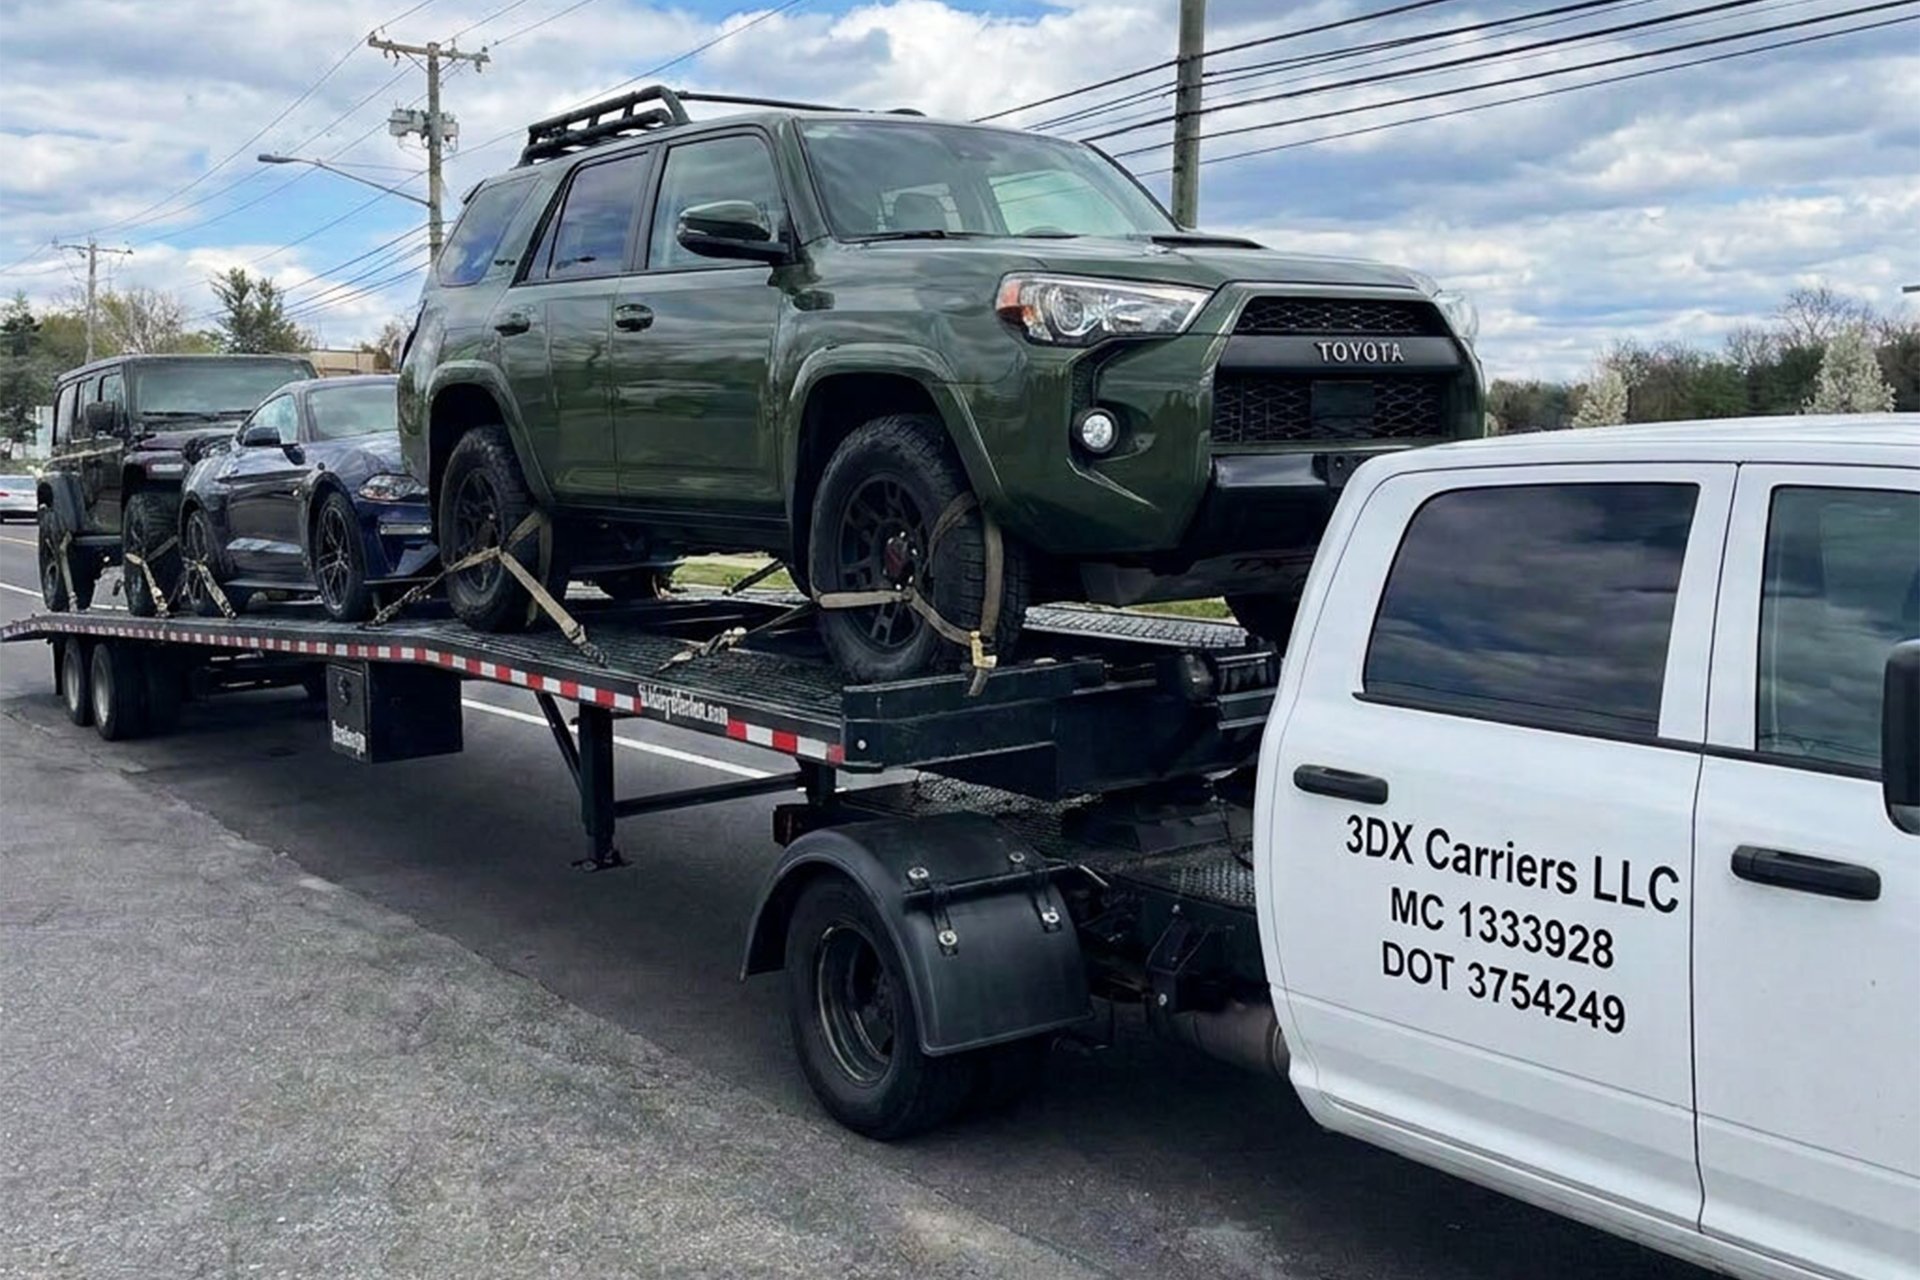
Fraudulent car listings using AI have spread on Facebook Marketplace, featuring fake dealer licenses, window stickers, and bogus GPS trackers. Photographer Will Matthews lost $36,240 after paying for a nonexistent Toyota 4Runner TRD Pro via a Tier 1 bank loan.

AI Car Dealer Scams Are Infesting Facebook Marketplace—and They’re Working
Security

Security agencies warn North Korean hackers target job seekers to steal crypto

The FBI, US Department of Defense and agencies of Japan, Australia and Germany warned about the WaterPlum (Contagious Interview) group, which poses as employers such as AI and crypto companies to attack developers and IT specialists. More than 30,000 devices in 100+ countries were infected, and about $11 million in crypto was stolen from 7,000 wallets.

Security agencies warn North Korean hackers target job seekers to steal crypto
Security

FBI, Coast Guard boarded hacked oil tankers heading towards US coast

From August 21 to 24, the FBI and US Coast Guard boarded two oil tankers heading to the US after reports of network hacks. Hackers gained control of navigation, propulsion and cargo systems on at least one vessel. The US is investigating possible Iranian involvement.

FBI, Coast Guard boarded hacked oil tankers heading towards US coast
Security

Telnet Is Still Open: Why the IoT Botnet Notices Keep Describing the Same Reachable Population

In August 2026, China's National Network and Information Security Notification Center named five cross-border botnet families — Mirai, CondiBot, Gafgyt, TBot and SoftBot. They gain initial access through Telnet and SSH brute force using factory passwords and exploitation of old vulnerabilities.

Telnet Is Still Open: Why the IoT Botnet Notices Keep Describing the Same Reachable Population
Security

T-Mobile COO Leaks Photos of iPhone 18 Pro IMEIs and Serial Numbers

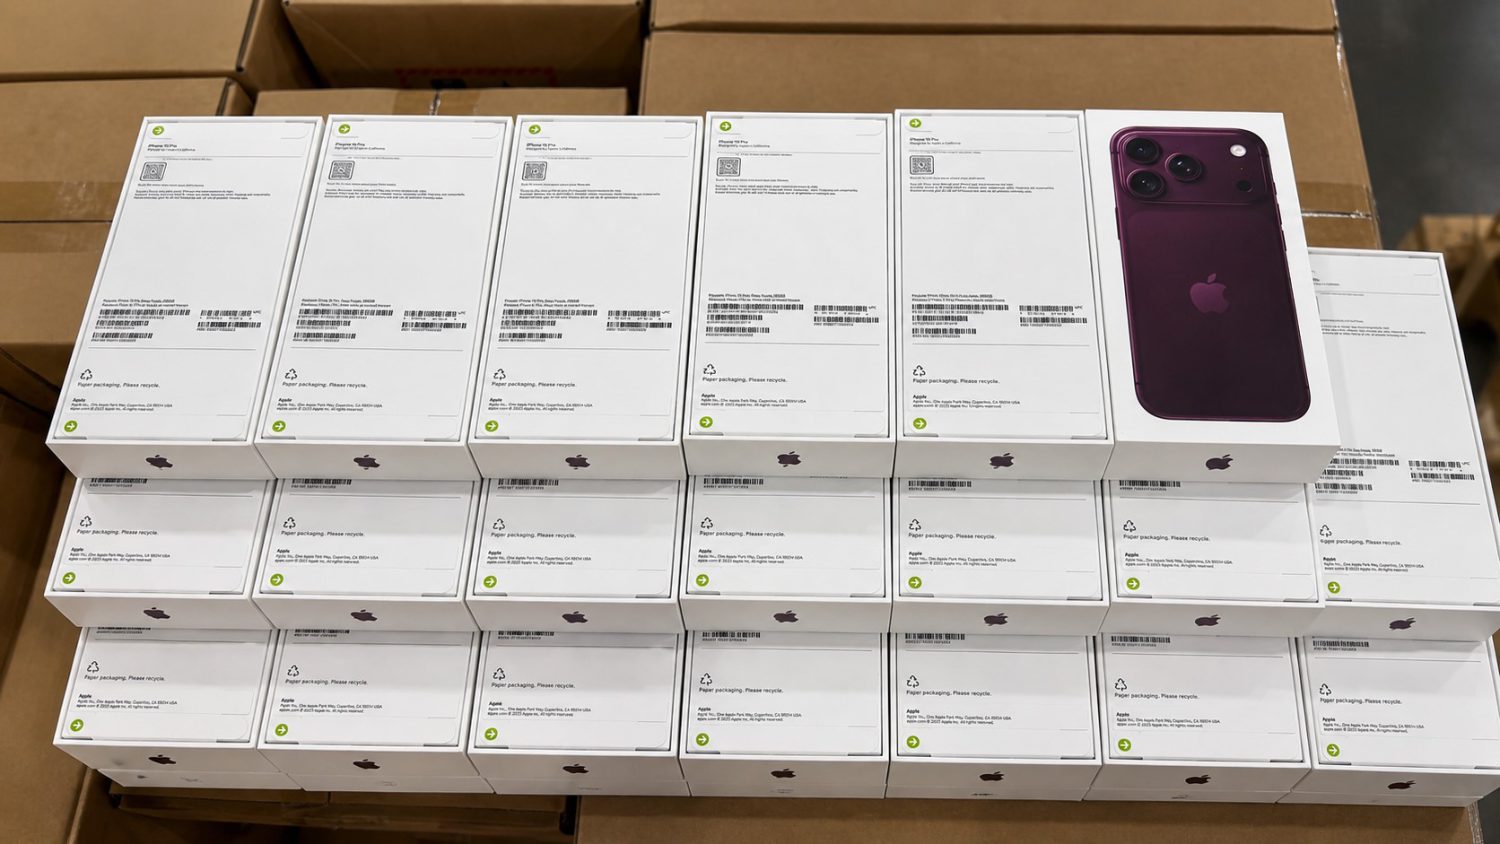
T-Mobile COO Jon Freier posted a photo on X of a warehouse with iPhone 18 Pro boxes, showing IMEIs and serial numbers of dozens of devices. The post was deleted, but the numbers could have been copied by automated tools, risking false blocking or cloning before activation.

T-Mobile COO Leaks Photos of iPhone 18 Pro IMEIs and Serial Numbers
Security

Transparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2

The Pakistan-linked group Transparent Tribe (APT36) is attacking government and defense targets in India and Afghanistan. Zscaler ThreatLabz discovered new tools RUSTYSHADE, RUSTYMOVE, PSNATCH, and BASHNATCH, with private GitHub repositories used for C2.

Transparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2
Security

Flock Safety’s Fake Police Unit Searched Real City Cameras

Flock Safety created a fictitious police account 'Flock City PD' and used its FreeForm AI search to query real city cameras in Georgia and Texas for people with Stars of David, political stickers, and protest signs. Moderation failed to block some sensitive queries, as revealed by audit logs obtained by 404 Media.

Flock Safety’s Fake Police Unit Searched Real City Cameras
Security

Fake LastPass Authenticator GitHub repos push new Rapuncel infostealer

A campaign uses SEO-optimized GitHub repositories impersonating LastPass and 39 other companies to deliver the new Rapuncel infostealer. It also installs a Microsoft-signed Alinubx.sys driver that disables 145 antivirus and EDR solutions.

Fake LastPass Authenticator GitHub repos push new Rapuncel infostealer
Security

GhostCode attackers abuse device codes to take over Microsoft 365 accounts

eSentire researchers found the GhostCode phishing kit abusing Microsoft's legitimate OAuth device authorization flow to steal Microsoft 365 access tokens. The attack registers devices in Intune and obtains a Primary Refresh Token with a 14-day lifetime, enabling persistent access.

GhostCode attackers abuse device codes to take over Microsoft 365 accounts
Security

Fake passkey setup requests lead to Microsoft 365 compromises

Microsoft Security Research linked cloud account compromises to attacks in which criminals call employees posing as IT support and ask them to update a passkey or sign-in settings. Attacks tracked since May: hackers added their own authentication methods, explored resources via Microsoft Graph and downloaded files from SharePoint and OneDrive, sometimes accessing Exchange Online mail.

Fake passkey setup requests lead to Microsoft 365 compromises
Security

Nations take action on North Korean IT workers after UN report

MSMT released a report on the North Korean IT worker scheme: in 2024 they earned up to $800 million. Argentina, Pakistan, Vietnam, and Laos took measures—investigations, arrests, and sanctions against intermediaries. China increased surveillance, making it harder for workers to enter.

Nations take action on North Korean IT workers after UN report
Security

Ransomware Developer Sentenced, Plugin4Shell AI Attack, Critical SAP Flaw

A Zurich court sentenced a Ukrainian developer of Lockergoga, MegaCortex and Nefilim ransomware to nearly 13 years in prison, with damages estimated at $123 million. SecurityWeek also reported CVE-2026-44756, a critical SAP Extended Passport flaw allowing unauthenticated code execution, and the Plugin4Shell attack on AI agents Claude Code, Codex and Copilot.

Ransomware Developer Sentenced, Plugin4Shell AI Attack, Critical SAP Flaw
Security

Iran and China Create First Autonomous AI Influence Campaigns

Iran and China, along with Israeli companies, have for the first time used open Chinese AI models and AI agents for autonomous online influence campaigns. According to NYT, this heralds a new stage of online manipulation.

Iran and China Create First Autonomous AI Influence Campaigns
Security

Hollard data hits dark web after MIP hack

Hacker group The Gentlemen has published data stolen from insurer Hollard in the dark web following a June attack on its contractor MIP Group. According to ITWeb, the attackers demanded a ransom; data of clients of about 45 South African insurance companies, mainly funeral policyholders, was affected.

Hollard data hits dark web after MIP hack
Security

CISA urges business to deploy decoys, lures, and honeypots to catch hackers in the act

The US cybersecurity agency CISA released recommendations for deploying cyber decoys—honeypots, lures, and honeytokens—to detect intrusions. The decoys complement the Zero Trust model by identifying attacker activity that uses legitimate credentials and living-off-the-land (LOTL) techniques.

CISA urges business to deploy decoys, lures, and honeypots to catch hackers in the act
Security

LNG Tanker With US Cargo Reported to Be Victim of Cyberattack

An LNG tanker en route from the US to Europe experienced system failures that the crew believed was a likely cyberattack. Details of the incident and possible damage were not disclosed.

Security

Zeek 9.0 released as LTS for network security monitoring

The Zeek project released 9.0, an LTS version of its network security monitoring system. It adds cluster event streaming, parsing of encapsulated traffic (GRE, VXLAN) and the Spicy 2.0 parser generator with up to 40% faster compilation and support for QUIC-v2 and HTTP/3.

Zeek 9.0 released as LTS for network security monitoring
Security

New Settra ransomware variant hits retail and manufacturing

Huntress described a new Settra ransomware variant used against a retailer in July and a manufacturer in September. Attackers deployed the MeshAgent RMM tool, disabled Windows recovery features and used a vulnerable driver (BYOVD).

New Settra ransomware variant hits retail and manufacturing
Security

ServiceNow's answer to AI-speed attacks will sound familiar - consolidate the mess

ServiceNow unveiled a set of security features, including Agentic Exposure Management and AI agent access control, building on its acquisitions of Armis and Veza. The company proposes 'shift zero' — real-time vulnerability detection as AI accelerates attacks.

ServiceNow's answer to AI-speed attacks will sound familiar - consolidate the mess
Security

Hacking group ‘NightEagle’ targeting China’s high-tech sector expands operations to Russia

Cyber-espionage group NightEagle (APT-Q-95), which previously attacked Chinese defense and technology companies, has shifted to Russian organizations. According to Kaspersky, the hackers entered networks via VPN using stolen credentials, then deployed the GhostContainer backdoor on Microsoft Exchange servers.

Hacking group ‘NightEagle’ targeting China’s high-tech sector expands operations to Russia
Security

Russia Claims Strikes on De Novo Data Center in Kyiv, Ukraine

Russian forces claimed strikes on Ukrainian infrastructure, including the De Novo data center in Kyiv — one of the country's largest. According to TASS, the facility served Ukrainian military servers. De Novo calls itself a sovereign cloud and AI provider serving Ukraine's largest banks.

Russia Claims Strikes on De Novo Data Center in Kyiv, Ukraine