UK Government Shifts to Service-Led Cyber Governance After Stinging Audit
The UK government is overhauling civil service cybersecurity, moving from top-down mandates to centrally built services that departments actually adopt. The shift follows a 2025 NAO report that found no proper implementation plan for the 2022 strategy and severe staffing gaps.
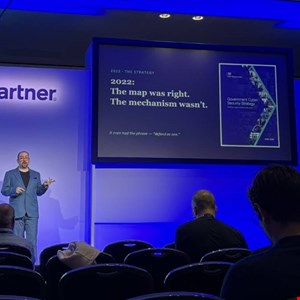
- 2025 NAO audit: the 2022 strategy had no implementation plan or way to measure results
- One in three UK government cyber roles is vacant or filled by contractors
- A central vulnerability monitoring service cut median fix time from 50 to 8 days
- UK government comprises roughly 465 separate entities with their own budgets and systems
Read next
Policy