Rust-based CikaBika Bot uses Discord as its command center
Darktrace documented a campaign spreading the Rust-written CikaBika Bot RAT via a disk image with a fake Word shortcut, with command-and-control run through per-victim Discord channels and file exfiltration via Ngrok. A Nim loader plants a malicious dbghelp.dll in Edge's folder using a PowerShell UAC bypass.
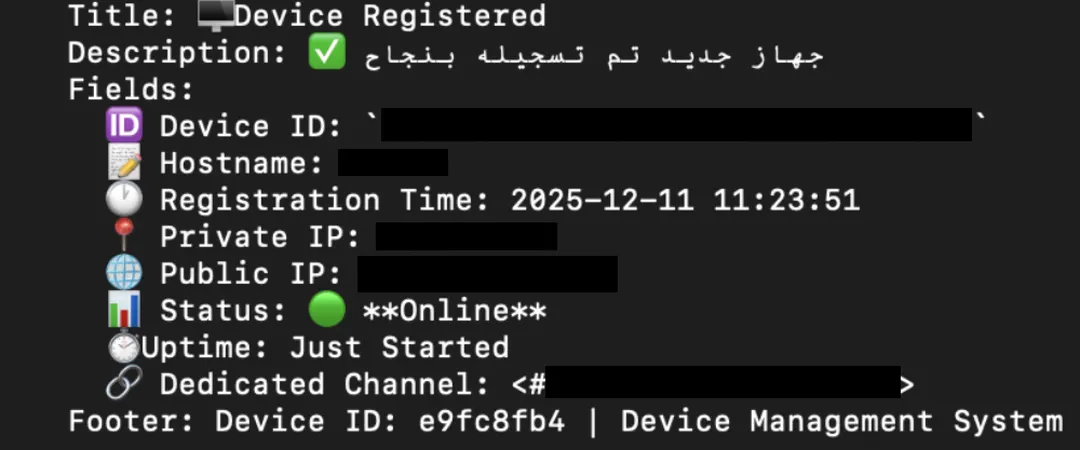
- Infection starts with a disk image, fake PDF and Word shortcut
- Nim loader and Rust DLL sideloaded as dbghelp.dll in Edge
- Each victim gets a dedicated Discord C2 channel
- Commands include shell, file theft, screenshots and screen streaming
Read next
Security