Darktrace: AI agent history is unsigned and writable by anyone
Darktrace's Signal Labs demonstrated conversation history poisoning: a malicious package or any process with write access injects a fabricated session into the harness's local database, and the model treats it as trusted context. All four tested harnesses (Claude Code, Codex, Kiro-CLI, Pi) accepted the fake history, with full Active Directory compromise reached in the lab. There is no client-side patch; researchers propose cryptographically signing every model response and verifying it server-side.
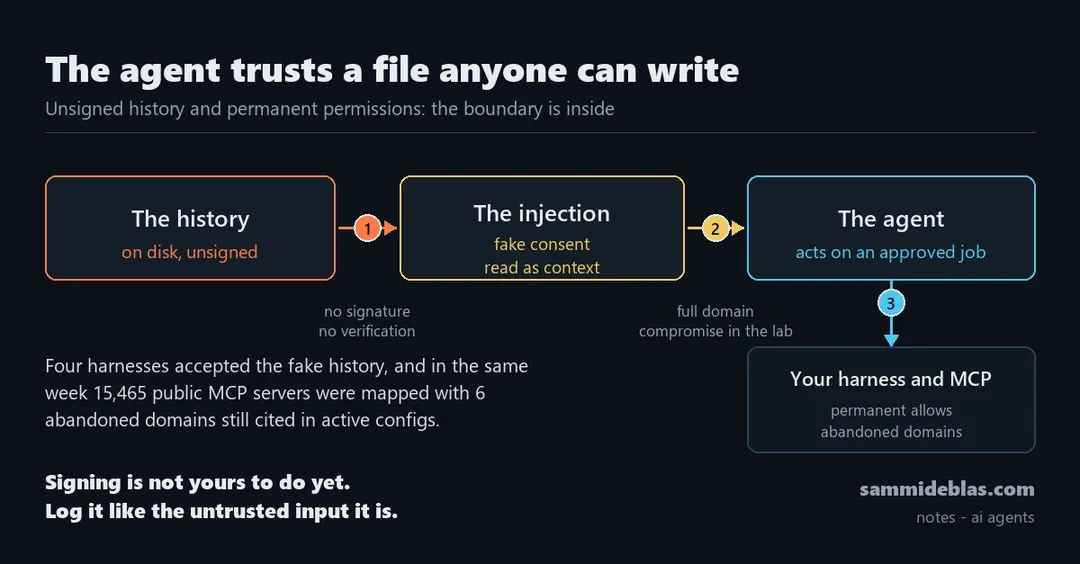
- Injected session history made agents run a pentest without user authorization
- All four harnesses tested (Claude Code, Codex, Kiro-CLI, Pi) accepted the fake history
- Full Active Directory compromise reached with Opus 4.6 and Sonnet 4.5
- OX Security: 15.6% of 15,465 MCP servers resolve outside the US, six domains abandoned
Read next
Security