IBM FlashSystem detects data theft inside the drive before ransomware encrypts
IBM FlashSystem 5600, 7600 and 9600 arrays with fifth-generation FlashCore Modules now detect data exfiltration inside the drive: the module baselines each volume's read pattern and confirms a suspected event over a 30-minute window with a false-positive rate below 1%. The capability is available from October 2026 on firmware 9.1.2 or later.
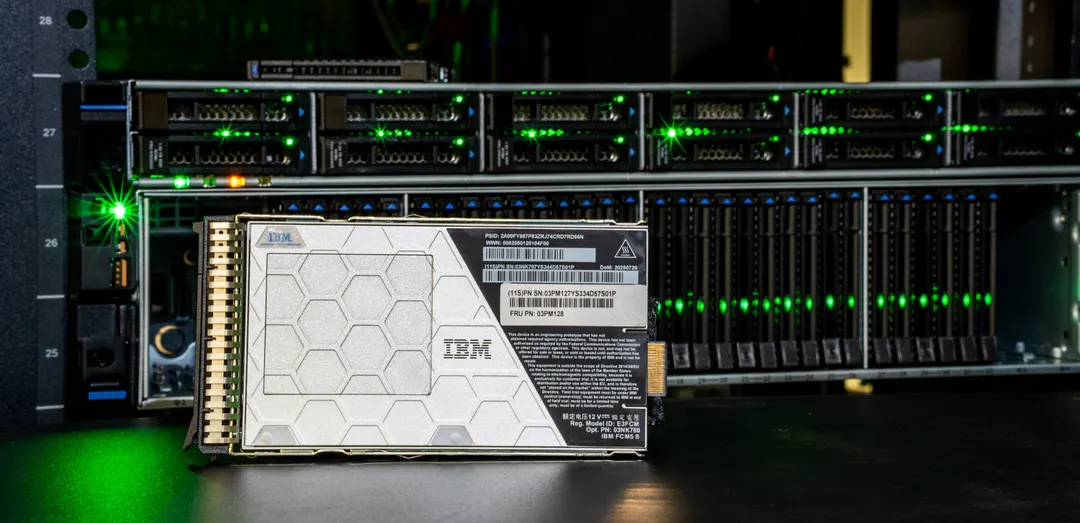
- Exfiltration detection runs in-drive, with no agents or app changes
- Confirmation window is 30 minutes; false positives stay under 1%
- Adds post-quantum ML-KEM (FIPS 203) and ML-DSA (FIPS 204)
- FlashSystem.ai claims up to 90% less effort for routine provisioning
Read next
Hardware