Researcher details OAuth Verification Trust Mismatch account takeover class
A HackerNoon researcher showed that OAuth clients trusting the email from a provider profile without checking the verified field let attackers bypass email verification and take over accounts. The demo used a Discord account confirmed only by phone number.
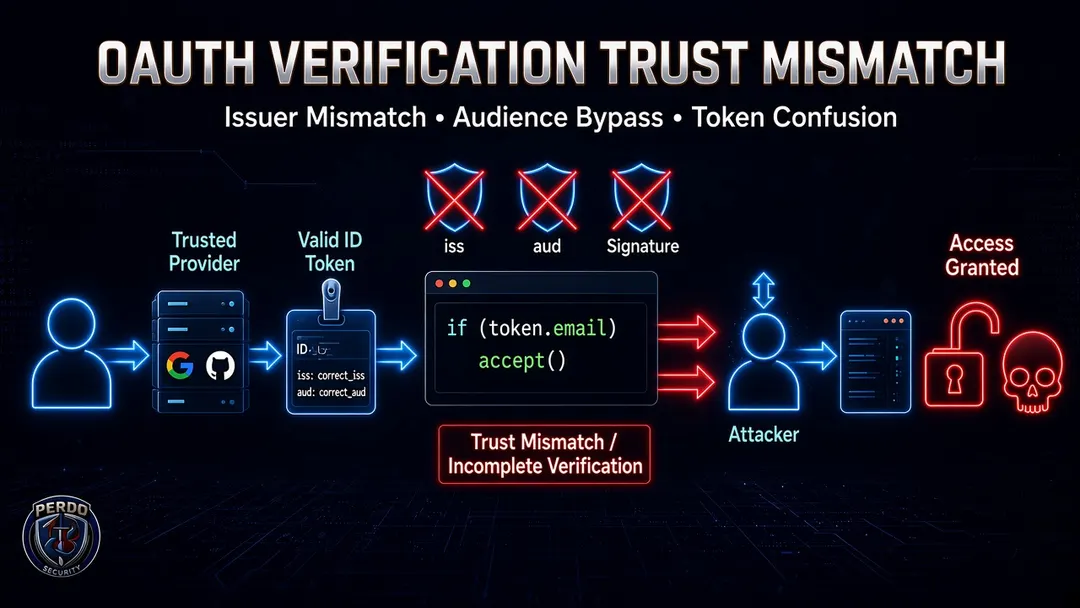
- Attack works when the client skips the verified field in the OAuth provider response
- A Discord account with unverified email completed signup on a vulnerable site
- Some apps correctly reject login when verified is false
- The vulnerability class is named OAuth Verification Trust Mismatch
Read next
Security