23 of 25 package managers install tampered packages by default
Trail of Bits tested 25 popular package managers against a fake compromised package server. Only Go and vcpkg verified every download without a lockfile, and fewer than half checked lockfile hashes by default.
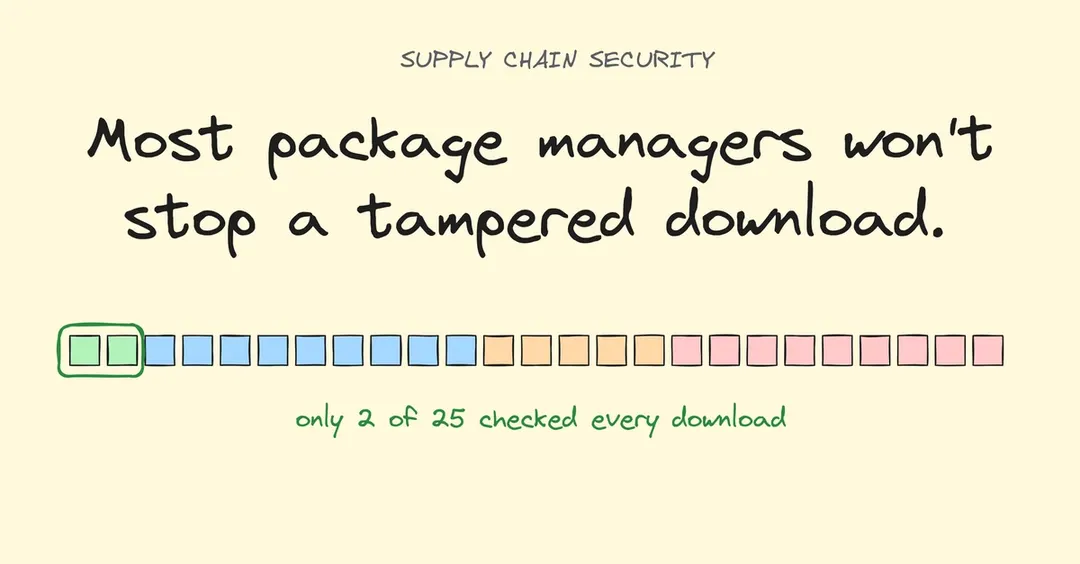
- Go and vcpkg verified all downloads even without a lockfile
- Fewer than half of the 25 tools check lockfile hashes by default
- Pub and pnpm before 11.4 overwrote the lockfile on a hash mismatch
- cpanminus connects to its repository over plain HTTP by default
Read next
Security