Slopsquatting: AI agents install packages attackers registered in advance
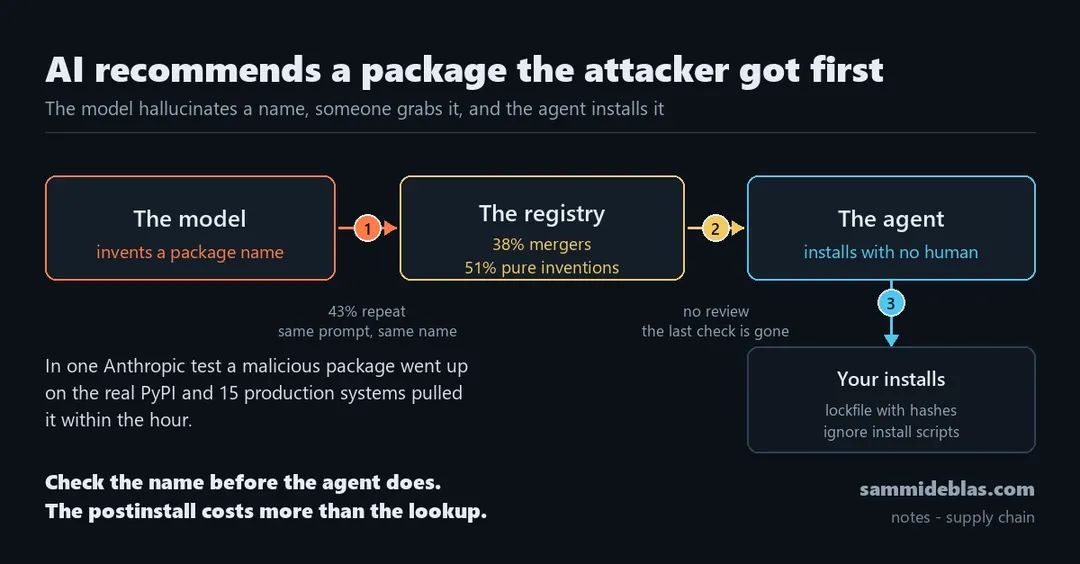
A USENIX Security 2025 study found 19.7% of AI-generated code samples reference non-existent packages, producing 205,474 invented names. Attackers pre-register these names on npm and PyPI, and coding agents install them automatically — in one Anthropic test a malicious package was downloaded by 15 real systems within an hour.
- 19.7% of code samples from 16 models referenced a non-existent package
- Models invented 205,474 distinct package names in total
- 43% of hallucinated names recur on every run of the same prompt
- Open models hallucinate 21.7% of the time vs 5.2% for commercial ones
Read next
Security