OpenCode flaw let malicious MCP servers run code at sign-in on Windows and WSL
A flaw in the OpenCode AI coding agent allowed a malicious or hijacked MCP server to execute code on a developer's Windows or WSL machine during sign-in. Anomaly, the company behind OpenCode, fixed the issue in version 1.18.33 in September.
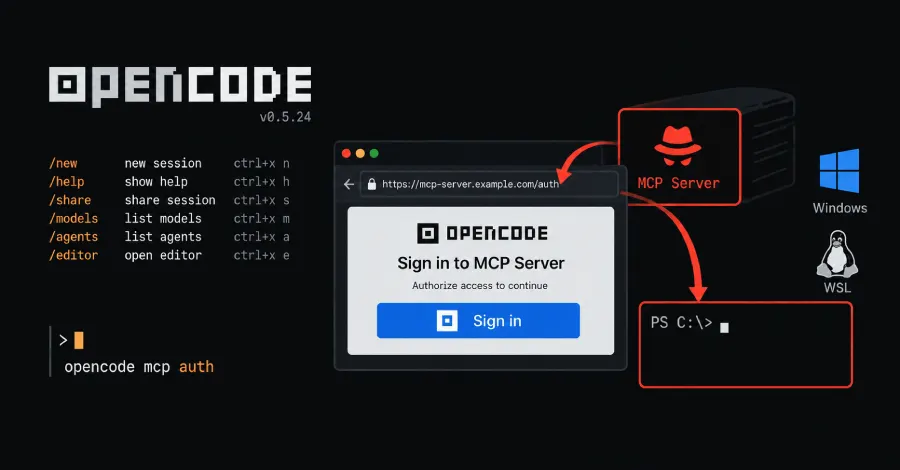
- Code ran with the developer's own access on Windows and WSL
- The attack triggered when connecting to a malicious MCP server
- The fix shipped in OpenCode 1.18.33 in September
Read next
Security