QPACK flaws can crash HTTP/3 servers with 4,000-fold memory amplification
FoxIO disclosed QPACK vulnerabilities that let an unauthenticated attacker crash many HTTP/3 servers with a single connection. A small batch of compressed headers expands in memory up to 4,000 times, enough to take down a default server. Working proof-of-concept code was released.
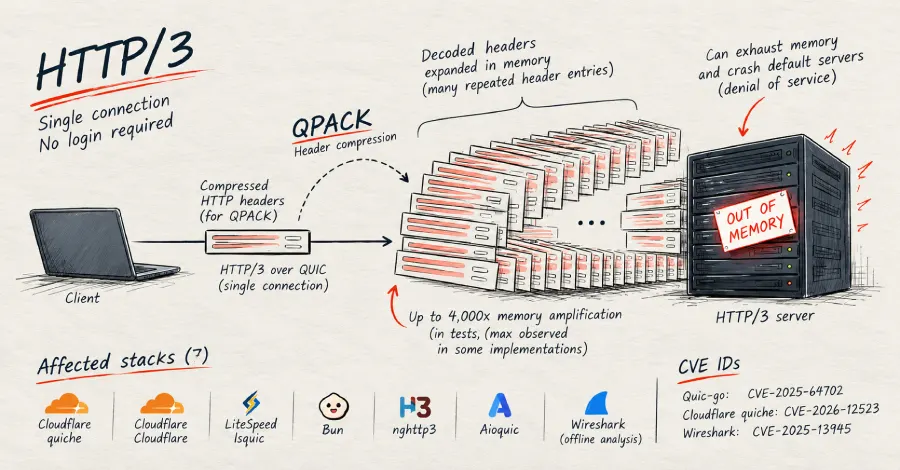
- Attack needs a single connection and no authentication
- Compressed headers expand in memory up to 4,000 times
- FoxIO released working proof-of-concept exploit code
Read next
Security