Old debug header on motherboards remains an unpatched security risk
On older motherboards with a discrete TPM, an unpopulated debug header can be abused to attack the trusted platform module. The flaw remains unpatched, and such headers still ship on production boards.
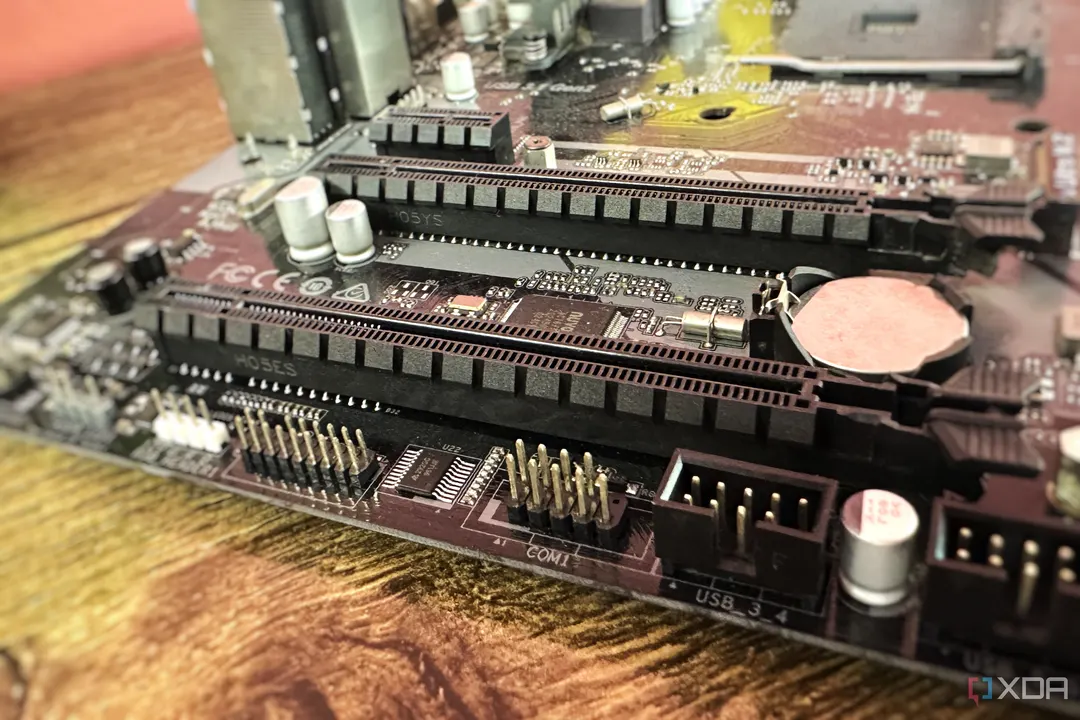
- An unpopulated debug header on older boards exposes the discrete TPM
- The vulnerability remains unpatched
- Headers persist for legacy compatibility and enterprise use
Read next
Security