DHS audit exposes TSA access control failures amid biometric expansion
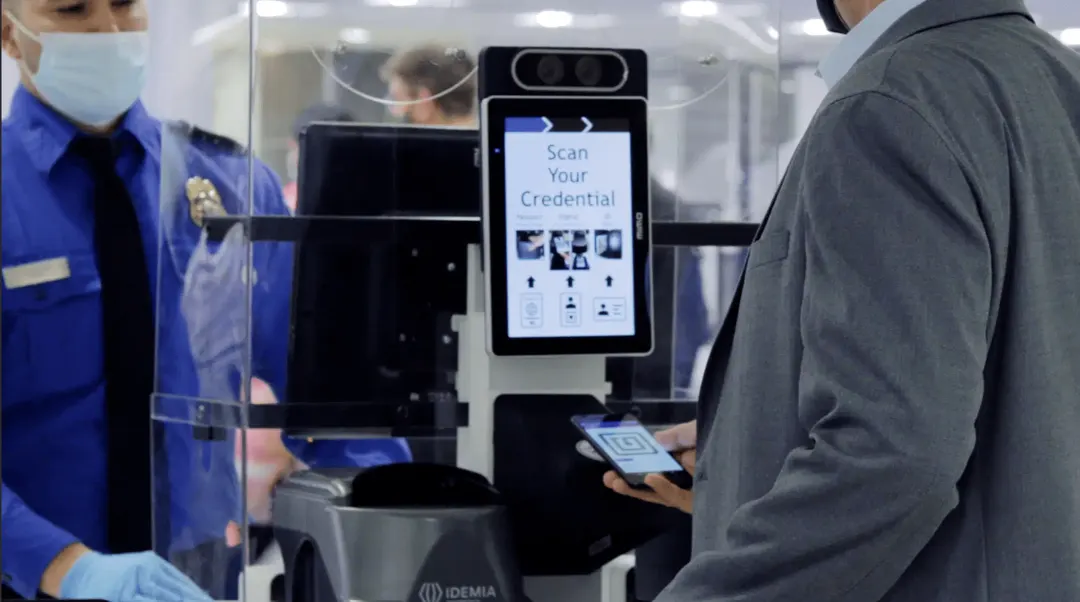
A September 30 DHS inspector general audit found that TSA mismanaged privileged accounts, created service accounts without required approvals, and failed to promptly disable accounts of former employees. A separate September 15 audit flagged weak oversight of the contractor behind the CAT-2 facial recognition system. Both reports raise concerns about protecting passenger biometric data.
- Sept 30 audit: TSA privileged accounts had inappropriate permissions
- Service accounts were created without required approvals
- Former employee accounts were not disabled on time
- Sept 15 audit: CAT-2 contractor could extract passport and license images
Read next
Security