Exploit details for Citrix NetScaler CVE-2026-88772 reveal pre-auth shellcode path
Researchers have disclosed technical details of a critical flaw in Citrix NetScaler ADC and Gateway tracked as CVE-2026-88772 (CVSS 9.5). The memory overflow in DTLS handling allows pre-authentication code execution and is already being exploited in the wild.
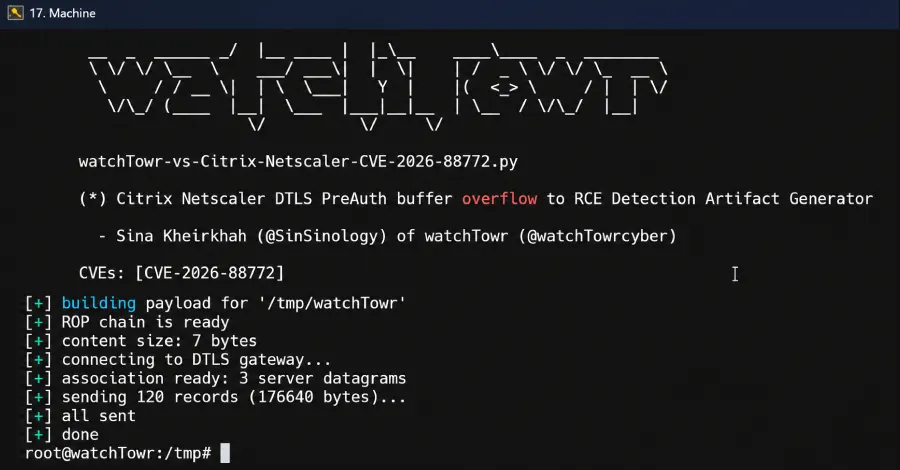
- CVE-2026-88772 carries a CVSS score of 9.5
- Memory overflow bug in DTLS protocol handling
- Pre-auth exploitation leads to shellcode execution
- The flaw is under active exploitation in the wild
Read next
Security