Warlock ransomware still exploits year-old SharePoint flaws
Symantec links the Longlegs group (Storm-2603) behind Warlock ransomware to attacks on water utilities, telecoms, governments and universities via unpatched SharePoint ToolShell flaws. At least four organizations in Portuguese- and Spanish-speaking countries were hit in two months.
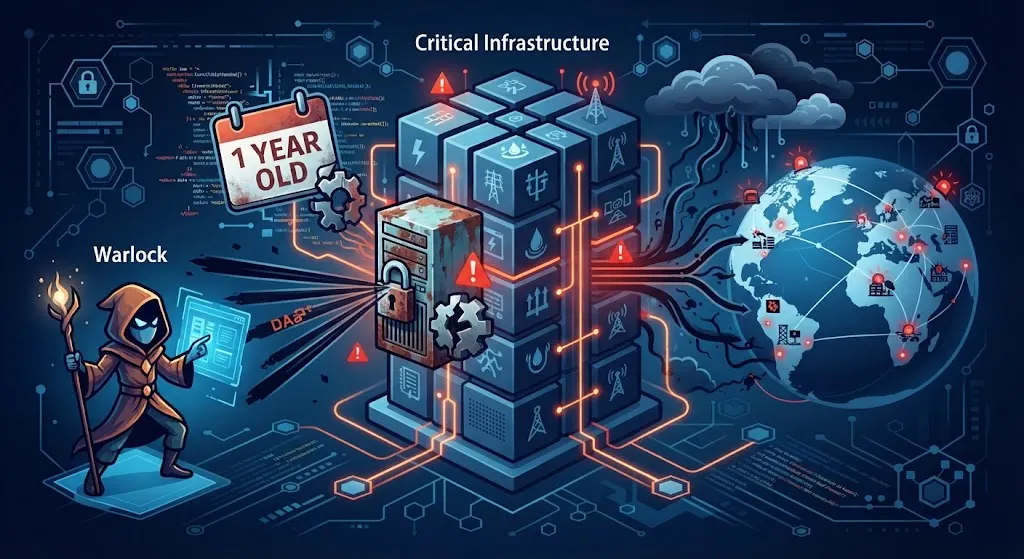
- Four victims in two months: water utility, telecom, government, university
- Attackers drop a webshell in LAYOUTS and steal ASP.NET machine keys
- They disable security software using vulnerable driver K7RKScan
- In one intrusion Warlock hit 33 hosts via SYSVOL within two hours
Read next
Security