Oracle PeopleSoft zero-day exploited by ShinyHunters was three chained flaws
The critical Oracle PeopleSoft bug exploited by ShinyHunters since May is actually three chained vulnerabilities, researchers said. Oracle patched all three under CVE-2026-35273 in June; the root is an SSRF that reaches an internal management interface via the loopback address.
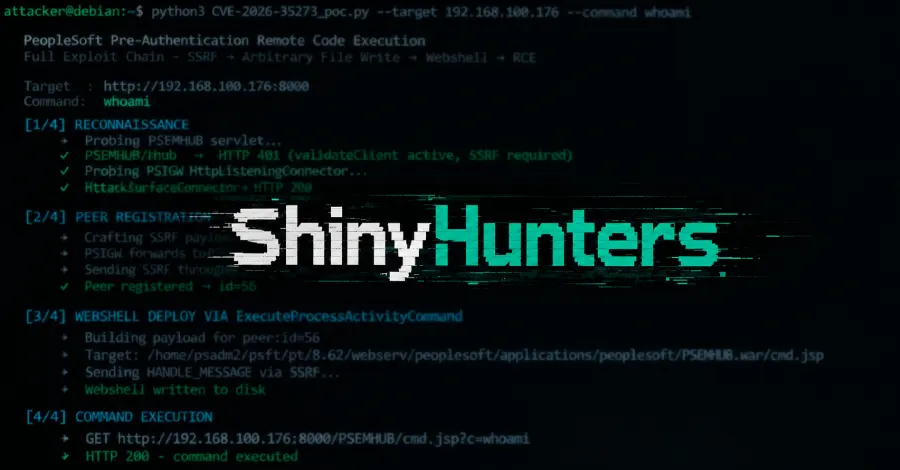
- ShinyHunters exploited the PeopleSoft flaw since May 2026
- Oracle patched three flaws under CVE-2026-35273 in June
- The chain starts with SSRF to an internal management interface
Read next
Security