PHP reissues Windows packages 8.2–8.5 to fix Brotli code execution flaw
PHP has rebuilt its official Windows packages for versions 8.2 through 8.5 to address CVE-2026-111497 in the bundled Brotli compression library. The flaw can corrupt memory and potentially execute code, reachable via the cURL extension when it auto-decompresses HTTP responses, which is off by default.
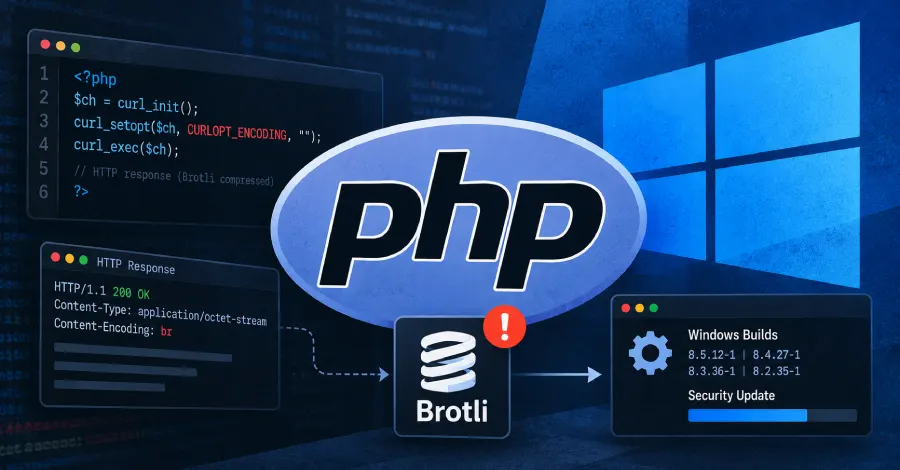
- Windows builds of PHP 8.2–8.5 affected, packages rebuilt
- CVE-2026-111497 in Brotli allows memory corruption and possible RCE
- Reachable via cURL auto-decompression, disabled by default
Read next
Security