Attackers force-pushed malware into 10 of a developer's GitHub repos
A developer found that attackers had amended the latest commit in 14 branches across 10 of his GitHub repositories, keeping his name and commit message. The injected code ran on folder open in VS Code and through build configs; researchers link the PolinRider campaign to North Korea.
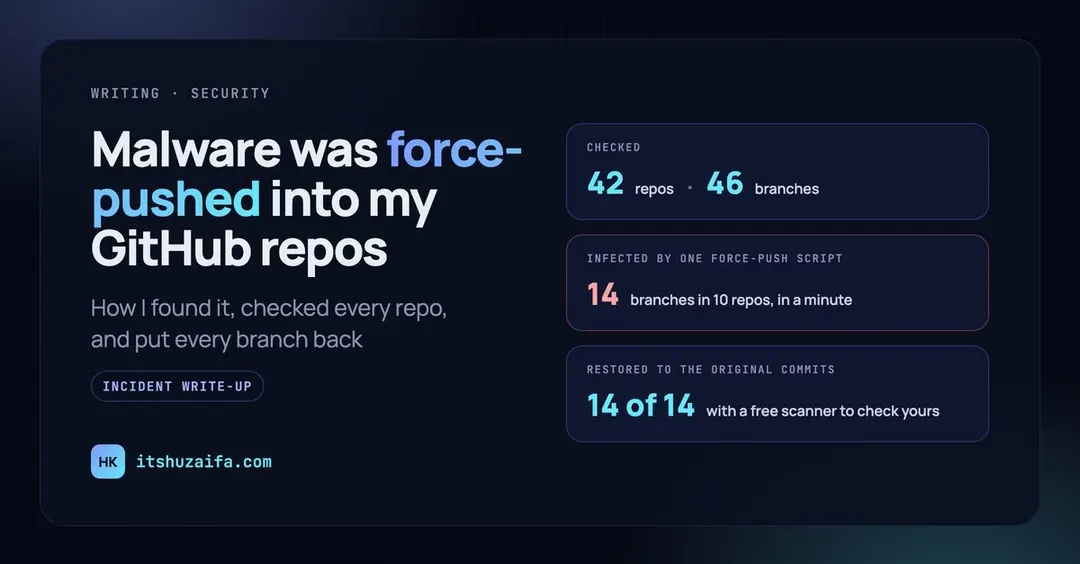
- 14 branches in 10 of 42 checked repos were infected, all force-pushed within a minute
- The commit added a VS Code task with runOn folderOpen and hidden JS disguised as a .woff font
- In two JS projects the code reached the build and deploy, forcing secret rotation
- The author revoked his token, replaced his SSH key and restored the original commits
Read next
Security