Microsoft 365 token-replay attacks compromise 97 accounts at 79 organizations
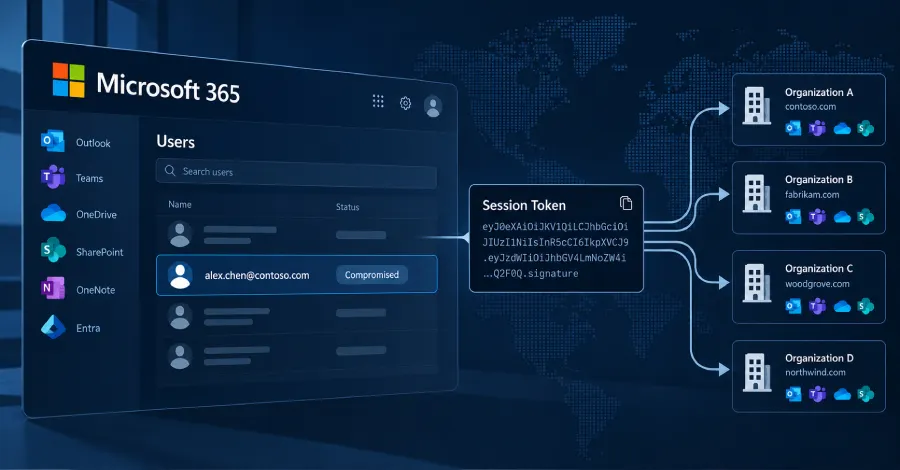
Huntress disclosed a Microsoft 365 campaign using an adversary-in-the-middle relay to capture sign-in sessions and replay stolen tokens to breach email accounts. Between July 14 and September 22, 2026, it recorded 497 successful sign-ins, with 97 accounts compromised across 79 organizations.
- Campaign observed from July 14 to September 22, 2026
- 497 successful Microsoft 365 sign-ins recorded
- 97 accounts compromised at 79 organizations
- Attack relies on AitM relay and token replay
Read next
Security