Gheist: 13,500 secret-dumping branches planted via stolen GitHub tokens
Wiz detailed Gheist, a five-week campaign that used stolen GitHub tokens to plant 13,500 branches across 850+ accounts, each with a workflow that base32-encodes env and secrets into logs and deletes the run. It targeted AI provider keys from Anthropic, Hugging Face, Groq and Nvidia; public repos were saved by GitHub's first-contribution hold, private ones were not.
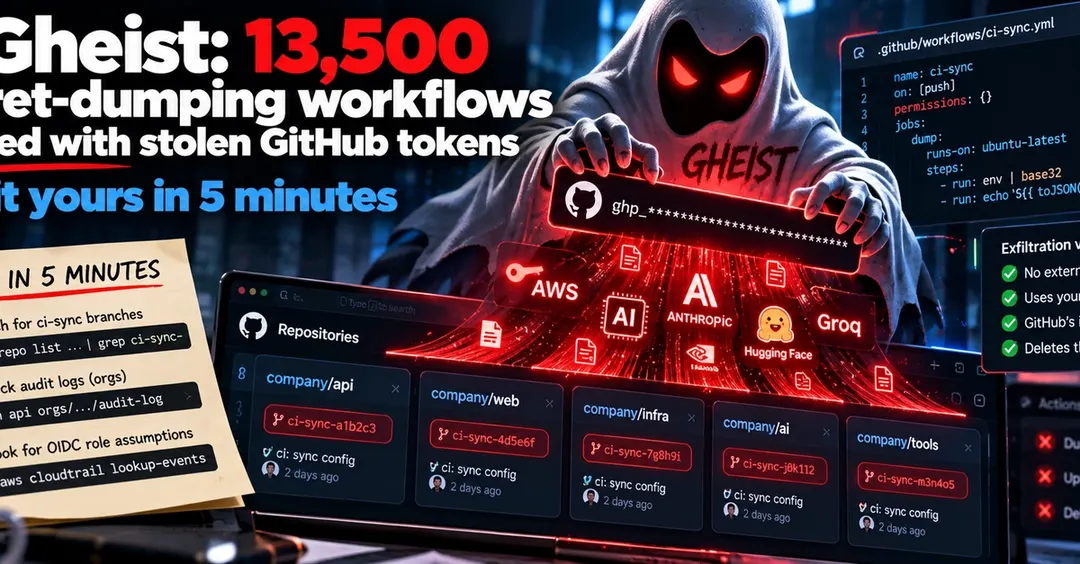
- 13,500 ci-sync-XXXXXX branches across 850+ compromised GitHub accounts
- Workflow base32-encodes env and secrets into logs, defeating GitHub masking
- Targets include Anthropic, Hugging Face, Groq and Nvidia API keys plus cloud credentials
- Public repos were protected by the first-contribution hold; private repos were not
Read next
Security