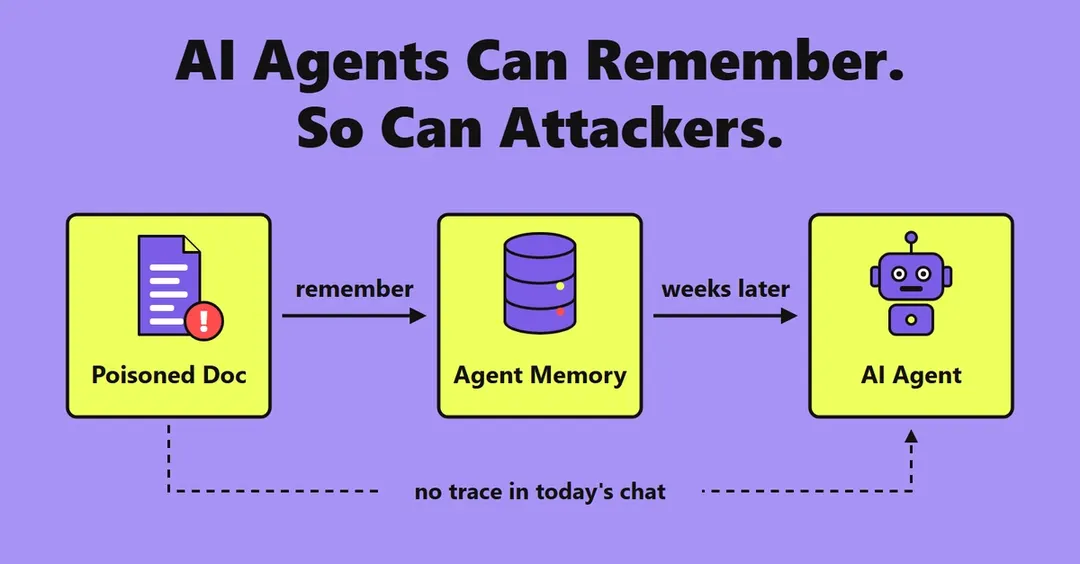
Memory poisoning in AI agents persists across sessions and fires weeks later
A write-up shows how an attacker plants a false "fact" once in an agent's long-term memory, which then triggers weeks later in clean sessions with no malicious input. Microsoft reported in February 2026 over 50 prompts from 31 companies trying to plant "remember this" instructions in assistant memory, and Cisco showed a malicious npm package rewriting Claude Code's memory files. OWASP lists Memory and Context Poisoning as ASI06 in its Top 10 for Agentic Applications.
- Microsoft: over 50 prompts from 31 companies tried to plant "remember" instructions in AI memory
- Cisco: a malicious npm package rewrote Claude Code's memory files
- OWASP lists Memory and Context Poisoning as ASI06 in its agentic Top 10
- Claude Code v2.1.50 removed user memories from the system prompt
Read next
Software