Next.js patches two critical RCEs and a Server Actions DoS
The October 14, 2026 Next.js security update fixes three vulnerabilities: two critical unauthenticated RCEs (in use cache and in SVG image optimization via sharp) rated 9.5, and a high-severity DoS in Server Actions rated 8.2. Patches ship in Next.js 16.4.1 and 15.5.28, and sharp must be 0.35.5 or later.
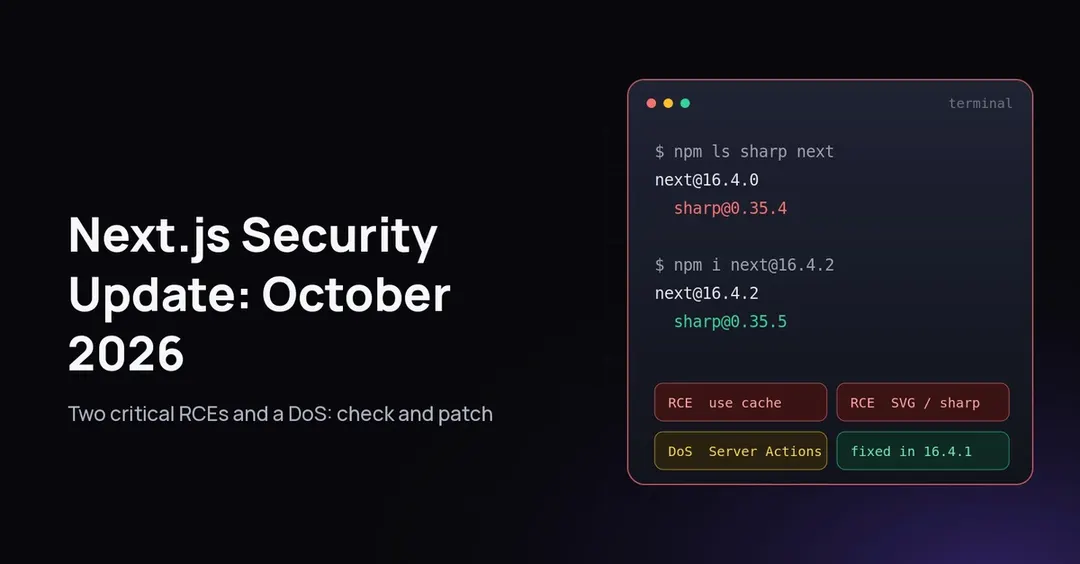
- use cache RCE affects Next.js 16.0.0–16.4.0, fixed in 16.4.1
- SVG RCE via sharp's librsvg hits glibc Linux, fixed in 15.5.28 and 16.4.1
- Server Actions DoS rated 8.2 affects versions from 13.0.0
- npm audit on next@16.4.0 reported zero vulnerabilities
Read next
Security