NSA urges immediate PHP patching as AI-found PHP2Shell flaws hit ~70% of the web
The NSA issued a formal advisory on critical PHP2Shell vulnerabilities in PHP itself, affecting up to 70% of websites. Fixes shipped October 21 in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35; the agency advises taking systems offline if patching isn't feasible.
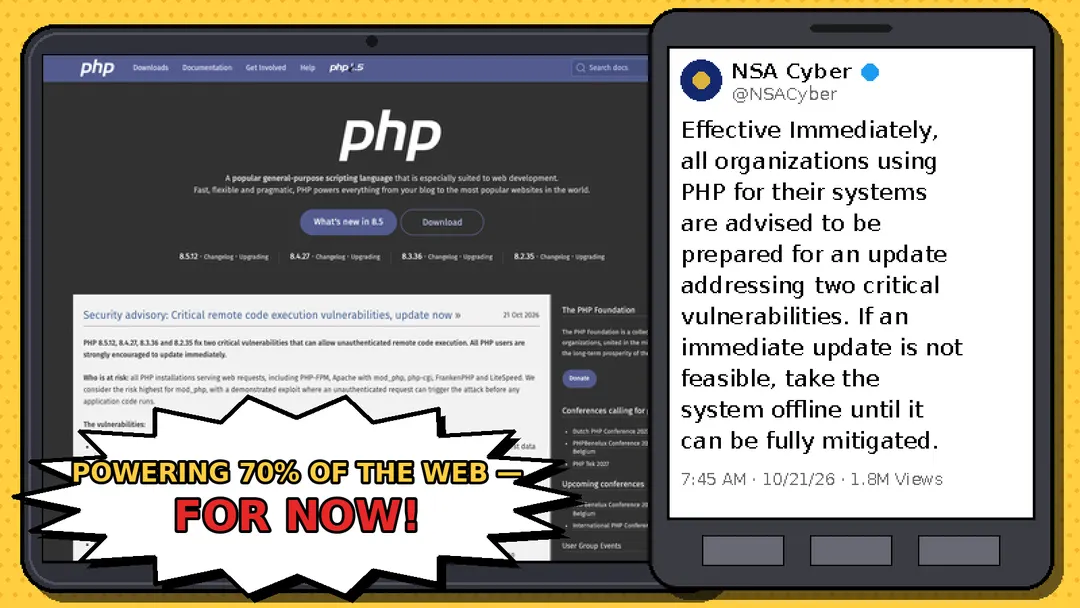
- Flaws CVE-2026-109618 and CVE-2026-109619 score 9.2 on CVSS v4.0
- About 758,000 servers run unsupported PHP 5.4–8.1
- Cloudflare enabled WAF protections for all plans nine hours before disclosure
- Vulnerable code dates back to PHP 5.4 in 2012 and is exposed in default configs
Read next
Security