Eight eMudhra intermediate CA keys compromised
Mozilla and Chrome Root Program confirmed on October 20 that the private keys of eight eMudhra intermediate CA certificates are compromised. Anyone holding such a key could issue certificates for any website that browsers would accept. Browsers and software vendors are rolling out emergency fixes.
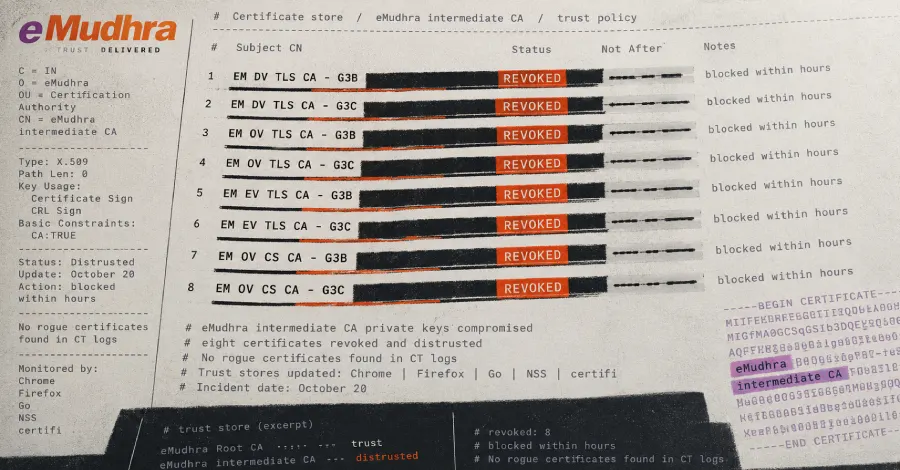
- Private keys of 8 eMudhra intermediate CAs are compromised
- Mozilla and Chrome Root Program confirmed the incident on October 20
- A forged certificate could be accepted as trusted by browsers
- Firefox 158.0.1 already blocks the compromised eMudhra certificates
Read next
Software