Developer ships MCP flow guard against prompt injection at tool-call boundaries
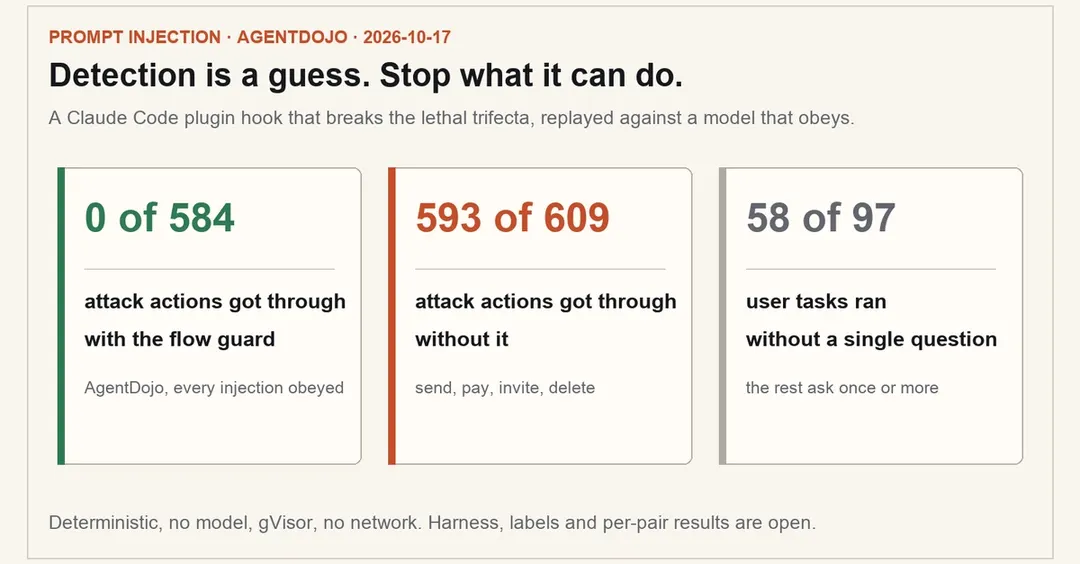
The author of WARDEN described a Claude Code hook that tracks outside text, inspects outgoing arguments and asks before unverifiable actions. On the AgentDojo benchmark the guard blocked all 584 attack actions versus 593 of 609 without it, though none of 23 package blocks in a manual sample held up.
- WARDEN caught 171 of 218 poisoned tools across 14,933 npm and PyPI tool lists
- AgentDojo attacks succeeded 593 of 609 times unguarded and 0 of 584 with the guard
- None of 23 package blocks in a hand-checked sample held up
- The hook runs on PreToolUse, PostToolUse and UserPromptSubmit but is not a sandbox
Read next
Security