Chainguard adds grayware as a third supply chain category, blocked by default
Chainguard introduced grayware as a third software supply chain category: code that behaves like malware — stealing credentials, exfiltrating data — while technically matching its stated purpose. Such packages are blocked by default, with opt-in exceptions via the policy engine. The company also announced Harness (built with Anthropic's Claude Mythos), Workspaces, Checks, MCP servers and Libraries expansion to Go and .NET.
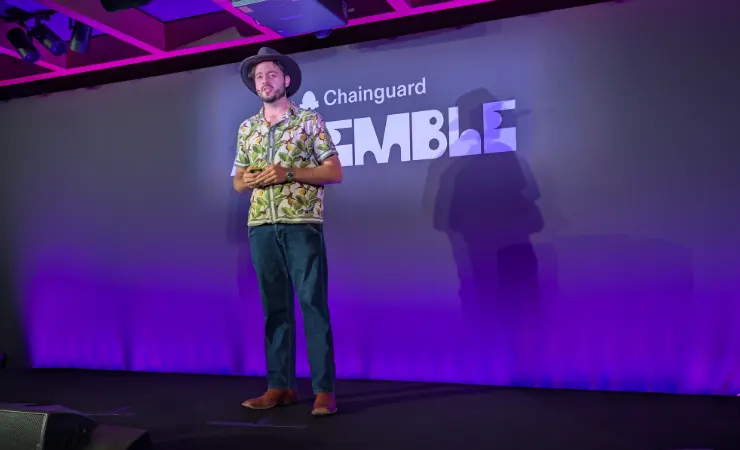
- Grayware is blocked by default, with exceptions set via policy engine
- Example: an npm package installs a Chrome extension for LinkedIn spam
- Harness found a vLLM token-poisoning flaw in a 12-hour scan
- Checks is claimed 3.5x cheaper and 12x faster than GitHub Actions
Read next
Security