GitLab AI Gateway sandbox escape leads to full RCE
CVE-2026-90970, rated CVSS 9.9, lets an authenticated Duo Agent Platform user escape the prompt template sandbox in GitLab AI Gateway and run arbitrary commands on the server. Patches shipped in versions 19.2.4, 19.3.2 and 19.4.1, with self-hosted deployments urged to update immediately.
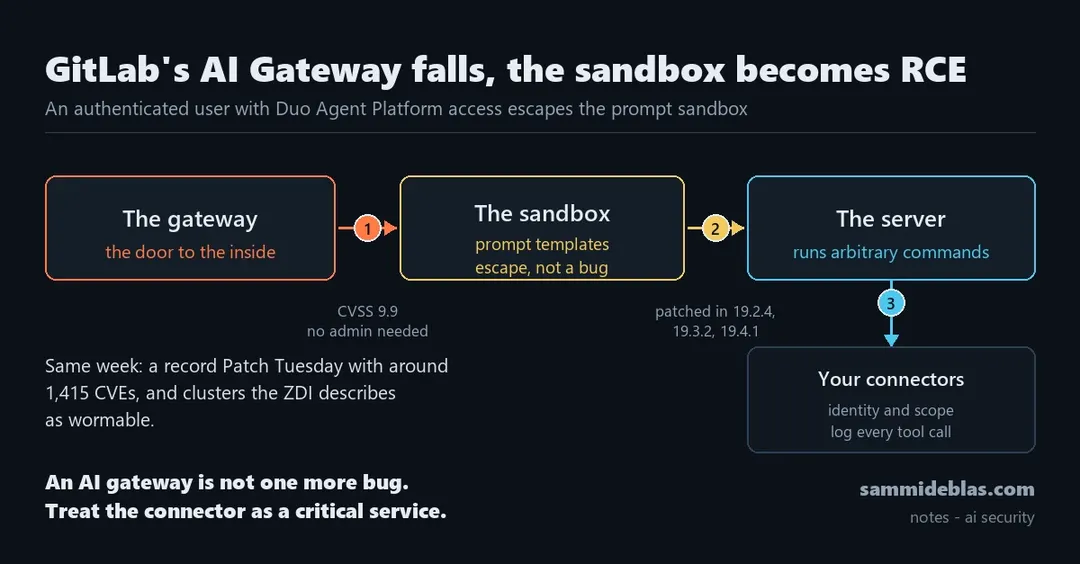
- CVE-2026-90970: CVSS 9.9 prompt sandbox escape in GitLab AI Gateway
- A regular account with Duo Agent Platform access is enough, no admin rights needed
- Fixes released in versions 19.2.4, 19.3.2 and 19.4.1
- LLM-to-internal-systems connectors should be treated as critical exposed services
Read next
Security