Four-byte write and timing bug let researchers run code in Windows SmartScreen enclave
Security researchers executed their own code inside a protected VBS enclave in Windows that guards passwords for the SmartScreen anti-phishing feature. The attack relies on a four-byte write error and a timing bug, demonstrated as a lab proof-of-concept.
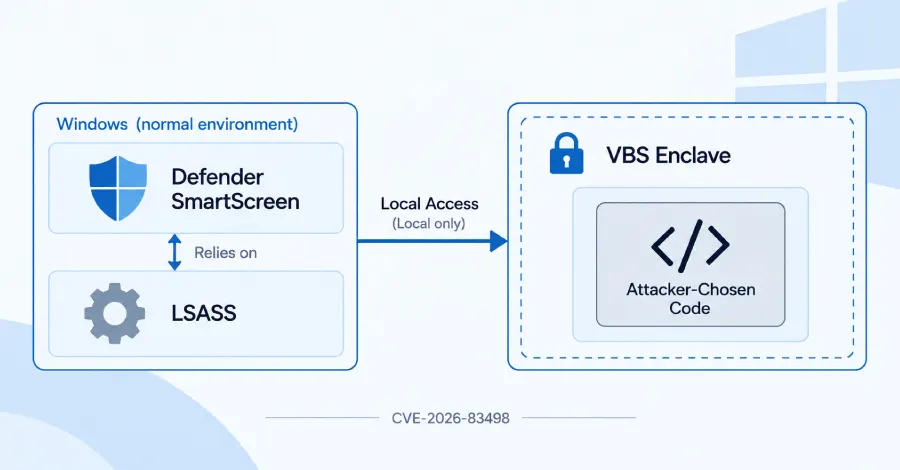
- Flaw affects the VBS enclave protecting Windows SmartScreen secrets
- Attack combines a four-byte write error and a timing bug
- Researchers' code ran inside the isolated memory region
- Exploit was demonstrated as a lab proof-of-concept
Read next
Security