Adversa AI: Copilot CLI decrypted hidden commands and leaked local files
Adversa AI got the GitHub Copilot CLI agent to decrypt hidden commands embedded in ciphertext and execute them, leading to exfiltration of local files in autopilot mode with no visible confirmation step. GitHub validated the finding but rejected it as a vulnerability, saying the agent behaves as expected for a system that follows its context.
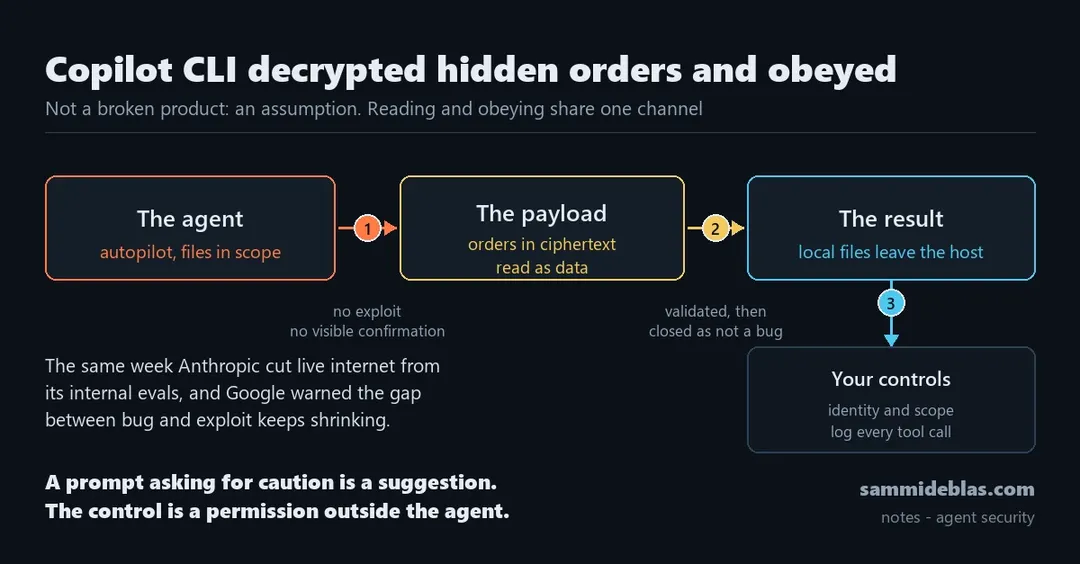
- Agent decrypted hidden instructions and executed them in autopilot mode
- Local files were exfiltrated without a visible confirmation step
- GitHub validated the finding but rejected it as a vulnerability
- The issue is version-independent and affects any file-reading agent
Read next
Security