yt-dlp RCE via .desktop files in HLS subtitles disclosed as CVE-2026-50023
A researcher detailed CVE-2026-50023 in yt-dlp: a global extension allowlist treated .desktop, .url and .webloc as peers of .srt. An HLS manifest with a subtitle URI ending in .desktop caused an executable shortcut to be written to the download folder. The fix shipped in version 2026.06.09.
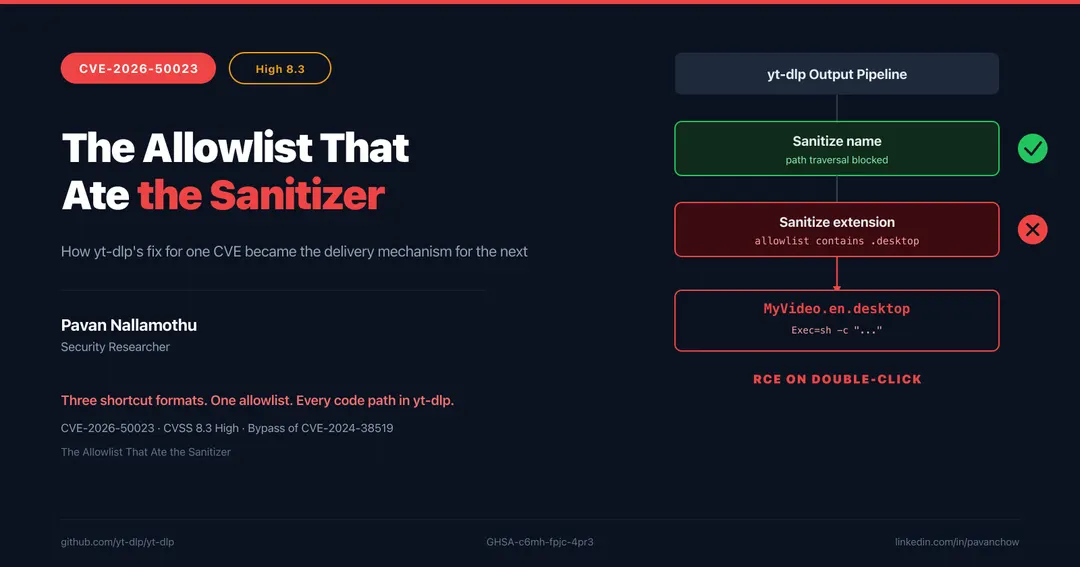
- Affects yt-dlp versions below 2026.06.09
- Exploit needs only --write-subs, not --write-link
- Patch removed .desktop, .url and .webloc from global ALLOWED_EXTENSIONS
- Fix by Grub4K, reviewed by bashonly
Read next
Policy