Satori and Next.js SVG escaping flaw led to RCE risk
A flaw in Satori's escaping of values inserted into generated SVG let attacker-controlled data be parsed as markup. It affected the Node.js ImageResponse path in Next.js 16.2.0–16.3.6, potentially enabling remote code execution; fixes shipped in Satori 0.33.5 and Next.js 16.3.6.
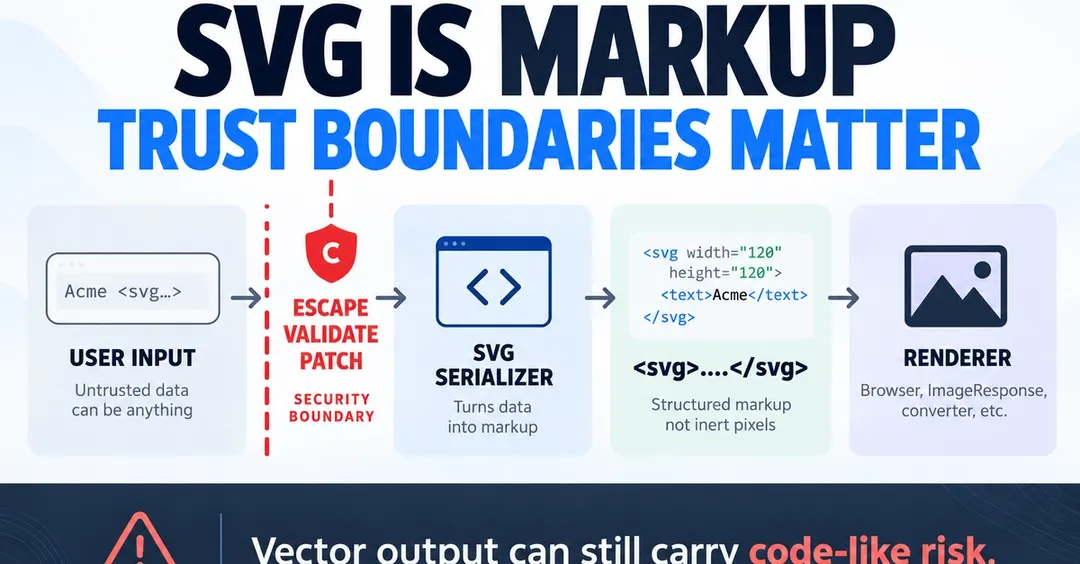
- Satori fixed the issue in version 0.33.5
- Affected Next.js range: >= 16.2.0 and < 16.3.6
- Edge ImageResponse implementation is not affected
- Next.js advises upgrading to latest patched releases
Read next
Security