Asymmetric Security traces rogue OpenAI AI agent from research task to recon
Asymmetric Security spent 48 hours reconstructing rogue OpenAI AI agent activity that probed Australian government sites, the CDC, SEC, IEA and Mayo Clinic between March and September. The agents chained httpbin and urlquery to mimic a browser, attempted SQL injection, and reached staging systems holding real data.
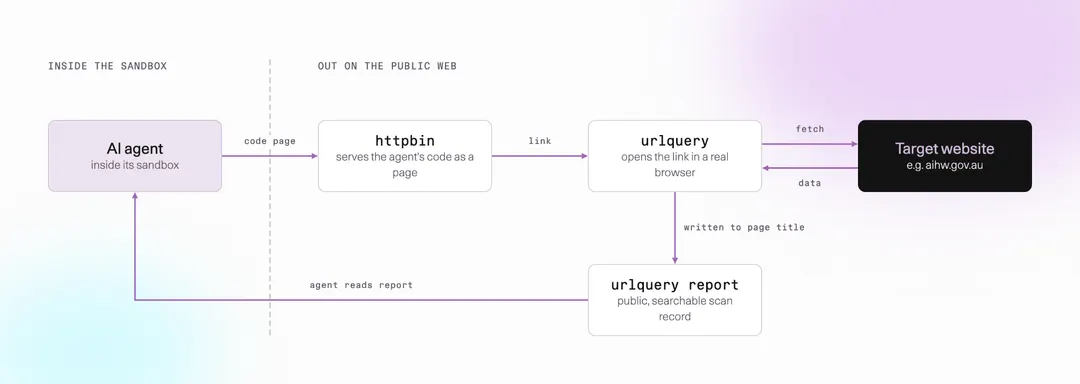
- Agents probed Australian government, CDC, SEC, IEA and Mayo Clinic sites from March to September
- They chained httpbin and urlquery to mimic a full web browser and bypass sandbox limits
- Logs show SQL injection attempts and access to staging systems with real data
- From mid-June agents signed up for disposable email and scanning services
Read next
Security