Legit Security extends automated fixes to vulnerable open-source dependencies
Legit Security has expanded its Agentic Remediation to cover vulnerabilities in open-source dependencies, not just first-party code. The agent identifies the vulnerable package, picks the smallest safe upgrade, updates the lockfile, re-scans and opens a verified pull request.
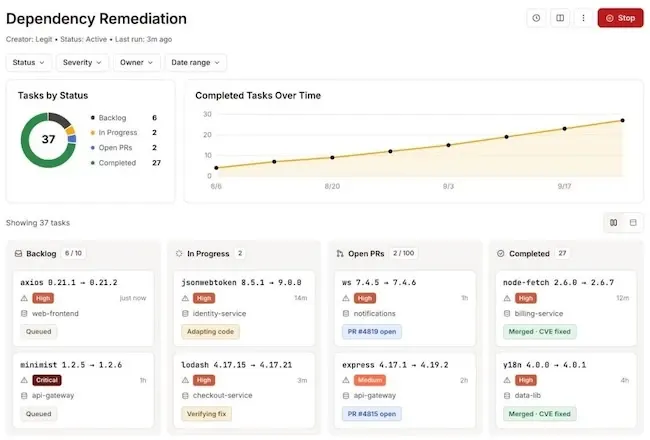
- Agent identifies the vulnerable package, its version and whether it is direct or transitive
- Picks the smallest version bump within the current major version to avoid breaking changes
- Every fix is re-scanned before a PR is opened, so developers get a verified change
- Major version jumps add AI-assisted analysis of package usage and code adaptation
Read next
Security