e-Panic Button security flaw sparks Gauteng legislature probe
The Gauteng Legislature's portfolio committee has demanded answers from the Department of e-Government after an unsecured database linked to the e-Panic Button app reportedly exposed users' identities, locations, ID numbers and medical aid details. The flaw was found by Stellenbosch University student Joel Cendras and may date back to the app's 2024 launch; the Information Regulator says it has received no breach notification.
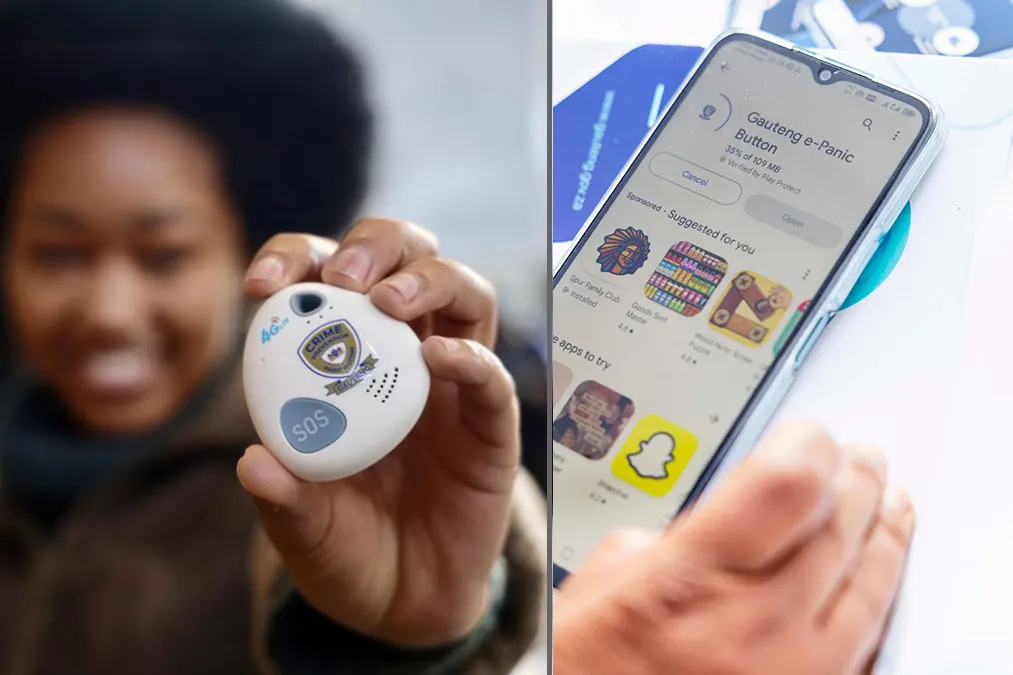
- Unsecured database reportedly held names, locations, IDs and medical data
- Flaw found by student Joel Cendras, possibly present since 2024 launch
- App has 288,307 active users and 114,414 emergency call-outs
- Information Regulator says no section 22 breach notification received
Read next
AI