CISA warns of critical pre-auth RCE flaw in MikroTik RouterOS
CISA is warning about CVE-2026-84411, a critical pre-authentication integer underflow in MikroTik RouterOS web management that allows remote code execution as root or denial of service with a single crafted request. Versions below 7.24 are affected.
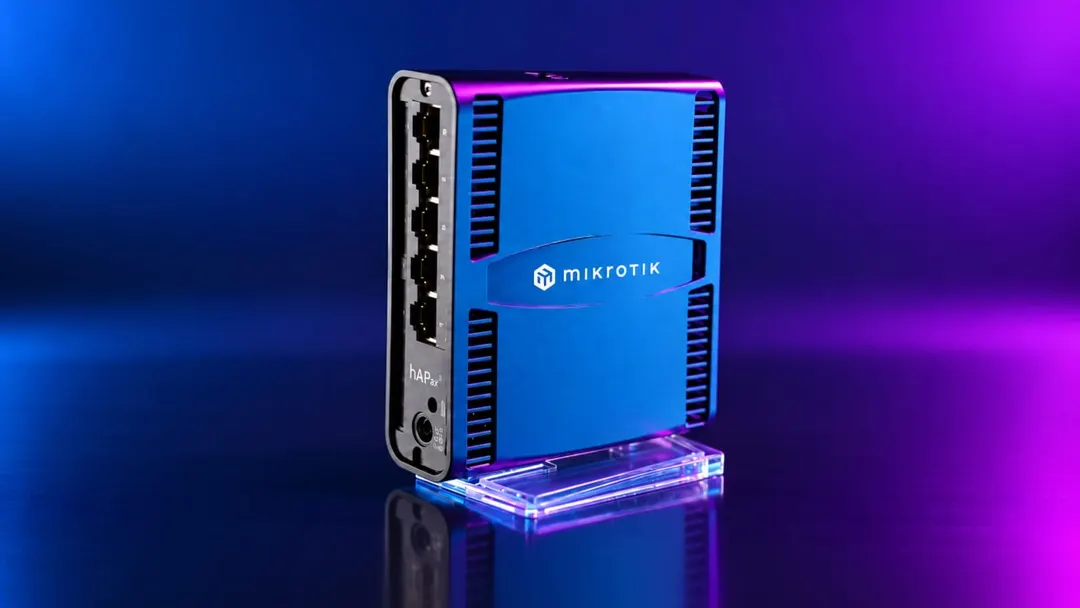
- CVE-2026-84411 is a pre-auth integer underflow in RouterOS web management
- A single request can achieve root code execution or DoS
- Versions below 7.24 are affected; update to 7.23+ recommended
- No active exploitation observed so far
Read next
Security