MCP Python SDK flaw lets malicious servers steal OAuth credentials
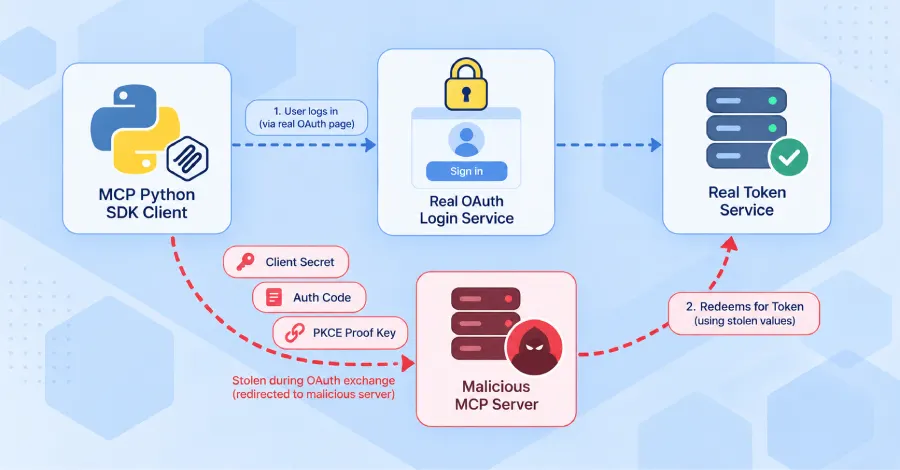
A vulnerability in the official MCP Python SDK allowed a malicious MCP server to trick applications into sending their client secret, authorization code, and PKCE proof key to an attacker-controlled token endpoint. The issue is fixed in version 1.30.0.
- SDK versions before 1.30.0 are affected
- Attackers could obtain the client secret, auth code, and PKCE key
- The fix ships in version 1.30.0
Read next
Security