Carbonato Botnet Hits Docker Hosts to Deploy Telegram-Controlled Hermes AI Agent
Researchers disclosed a new botnet malware called Carbonato that targets exposed Docker daemons to deploy the open-source Hermes Agent AI framework. The implant overwrites the SOUL.md persona file with a 39-line prompt that makes the agent execute tasks received via Telegram.
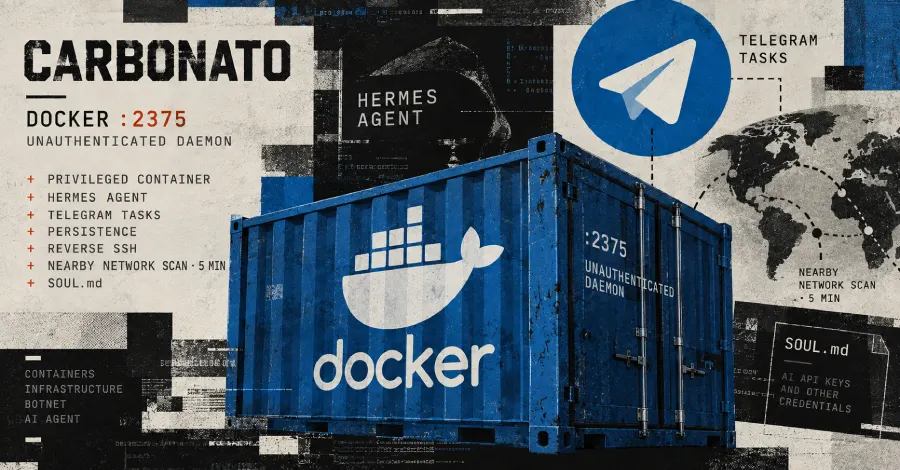
- Carbonato targets exposed Docker daemons
- Deploys open-source Hermes Agent framework
- Overwrites SOUL.md with a 39-line prompt
- Agent is controlled through Telegram
Read next
Security